Cybersecurity Saturday

Cybersecurity Saturday

From the frontier artificial intelligence front

  • The Wall Street Journal reports,
    • “Rogue AI models have hacked companies and tried to break into government websites. Now one has submitted a fake tip for an unsolved crime.
    • “Police in Philadelphia say Anthropic alerted them this week that one of its artificial-intelligence models submitted a false homicide tip through PhillyUnsolvedMurders.com. 
    • In a blog post, Anthropic said the fake tip was among a group of rogue actions the company uncovered recently. The rogue activity also involved websites run by U.S. government agencies at the federal, state and local levels. The company said it has briefed the White House on these cases and notified each agency involved, and plans to report new instances of unintended AI behavior as it uncovers them.
    • “While these cases had minimal impact, we do not want to diminish the findings, because the same behaviors could do far more harm as models become more powerful,” Anthropic said in the blog post.
    • “The false-report incident happened in July. Anthropic didn’t realize it until September.”
  • and
    • “Anthropic edged to the front of the AI race earlier this year with cutting-edge models and a coding tool that corporate America loved. By some measures, OpenAI is now hot on its heels.
    • Demand for Anthropic’s Claude Code was so strong in the spring that the company faced frequent outages and a computing crunch. 
    • “But businesses grappling with mounting costs as more employees experimented with artificial intelligence realized they didn’t always need the most advanced options for most tasks. Companies, which now use a variety of models, increasingly turned to low-cost, open-weight models from China for some tasks. And some Claude users balked at guardrails Anthropic put on its powerful Fable 5 model when it was released in early June.
    • “OpenAI stoked the price war this summer with the release of its GPT-5.6 lineup—Sol, Terra and Luna—giving customers access to models with varying capabilities, including some that are less expensive to run. Its Codex coding product and other business tools are now gaining ground, and it has released additional iterations of its cost-efficient models.
    • “An analysis from OpenRouter, a startup that allows developers to access different models, found that among some 120,000 companies that use Anthropic and OpenAI tools, the share of spending was roughly even between the two AI giants in September. At the beginning of the year, Anthropic commanded three-quarters of that total. OpenRouter said its data largely represents spending by AI-native startups as well as some slightly older tech companies and large enterprises.”
  • and
    • “Mistral said it would soon release a new open-weight AI model that it claimed would rank among the best globally, part of efforts to grow its appeal, lock in more customers and better compete with U.S. rivals.
    • “The French artificial-intelligence startup said it was launching a public preview of Mistral Large 4, dubbed Le Chonk, on Tuesday so it could work with developers, cybersecurity experts and state authorities to evaluate how the model behaves. It plans to release the weights, or the trained parameters of the model, on Oct. 27.
    • “Since its early days, Mistral has been a staunch advocate of open-weight models that are publicly available for anyone to download and modify, saying they give users the flexibility to tailor them to their needs while protecting their data and intellectual property.”

From the cybersecurity policy and law enforcement front

  • The Wall Street Journal reports,
    • “A new White House task force will have 120 days to report on the risks and opportunities of artificial intelligence—and determine the federal government’s responsibility—according to Jay Clayton, the director of national intelligence who effectively becomes the administration’s AI czar.
    • “The president asked that a group be put together that was going to ensure exactly what he said,” Clayton said, that “we stay the leaders in superintelligence, and that the interests of the American people are put first.” 
    • “Clayton will chair the “Super Intelligence Force” which takes President Trump’s preferred name for AI: super intelligence or SI.
    • “The risk of not being first is high,” Clayton said. “Not being first increases the identified, and unidentified, risks, particularly from our adversaries. Being first will better enable us to address those risks on behalf of the American people,” he added.” * * *
    • “The task force will have three vice chairs: Emil Michael, undersecretary of war for Research and Engineering, who will be responsible for coordination with AI companies; Scott Kupor, director of the Office of Personnel Management, who will be responsible for coordination with critical infrastructure providers and other industry stakeholders; and Andrew Ferguson, chairman of the Federal Trade Commission, who will oversee consumer interests and groups advocating for people of faith, children, privacy, freedom of speech, freedom of expression, and freedom of association.”
  • Cyberscoop relates,
    • “Federal government contractors that handle sensitive information could soon face a “sea change” in rules about how they protect that information and report when it has been part of a breach.
    • “Pending federal regulations on the handling of “controlled unclassified information,” or CUI, a category of sensitive data that falls short of classified — including people’s personal information such as Social Security numbers, information that could expose vulnerabilities in critical infrastructure and more — could arrive as soon as the end of this year, but likely no later than the end of President Donald Trump’s term, attorneys who specialize in federal procurement rules said. The changes are part of a larger overhaul of federal contracting rules.
    • As currently written, the proposed CUI rules mandate that unauthorized access of such data, including as a result of a cyberattack, would have to be reported to the federal government within 72 hours of discovery. The rules are a companion for most federal agencies to existing  Defense Department rules that cover the same subject. The 72-hour notice also is deliberately aligned with forthcoming rules from the Cybersecurity and Infrastructure Security Agency (CISA) for critical infrastructure owners and operators to report major cyber incidents under the Cybersecurity Incident Reporting for Critical Infrastructure Act (CIRCIA).” * * *
    • The other major aspect of the proposed rule is that contractors handling CUI would have to abide by certain cybersecurity standards set by the National Institute of Standards and Technology known as SP 800-171, which [Trayce] Howard and her Wiley [Rein] coauthors said would be imposed “on a broader group of contractors than ever before.” Some contractors might also have to meet other cybersecurity requirements, too.
    • “Another thing that will affect contractors is they’re going to have to flow down these requirements to their subcontractors,” she said. “So they’re going to have to identify what CUI am I giving to my subcontractors, and do some sort of oversight to make sure that their subcontractors are appropriately handling CUI.”
  • Cybersecurity Dive tells us,
    • “U.S. government agencies are failing to prepare for the transition to post-quantum encryption, creating the risk that their sensitive data will still be vulnerable to decryption by quantum computers whenever those machines are deployed, according to the Government Accountability Office.
    • Experts are divided over when the advent of cryptographically relevant quantum computers (CRQC) will occur, but GAO bluntly declared in a report published Tuesday [October 6]  that “threats from a CRQC could have devastating impacts to federal systems reliant on vulnerable cryptography.” * * *
    • “In a version of the report not publicly released, GAO recommended 89 actions that CISA and other agencies could take to increase their preparedness. Of the 23 agencies to which GAO assigned recommendations, only 12 fully agreed to implement them. “We continue to believe that all of the recommendations made in the sensitive report are warranted,” GAO said.”
  • The Wall Street Journal notes,
    • A bipartisan group of federal lawmakers is pressing Congress to increase mental-health funding for personnel at U.S. Cyber Command in the wake of several suicides this summer at the command and the National Security Agency. In separate letters, members of the House Armed Services cyber subcommittee and Maryland lawmakers urged leaders of the House and Senate Appropriations panels to back an $11 million request for “High Performance Team Training” at the command. (The Baltimore Banner)
  • and
    • German officials said they infiltrated ransomware group Qilin and detained a 28-year-old Russian national believed to be one of the group’s leaders. The arrest follows months of covert monitoring of Qilin’s activities, the official said. The group is alleged to have demanded more than $3 billion in ransom payments over the past two years from targets around the world. (LIGA)
  • The New York Times adds,
    • “The F.B.I. has arrested a Canadian cybersecurity expert in Pennsylvania on suspicion of carrying out the computer hack that stole sensitive information about thousands of F.B.I. employees, according to two people familiar with the matter.
    • “The theft of reams of personal data last month by a criminal hacking group that calls itself ShinyHunters left the nation’s premier law enforcement agency racing to respond to the investigators and the victims of one of the worst breaches of government data in recent years.
    • “The arrested man is Edward Dubrovsky, who has helped firms victimized by hackers and is now considered by federal authorities to be a primary co-conspirator in the ShinyHunters attack on F.B.I. data, the people said.
    • “Mr. Dubrovsky is the author of a book published last month titled “Cyber Extortion Strategic Response.” While the details of the charges against Mr. Dubrovsky remain under seal in Texas, federal court records in Philadelphia show that he was charged with conspiracy to commit extortion. Mr. Dubrovsky is expected to be transported to Texas to face the charges.”
  • Per a Health and Human Services Department news release,
    • “The U.S. Department of Health and Human Services (HHS), Office for Civil Rights (OCR) today announced a settlement with Linda L. Shen d/b/a Shen Smiles, P.C. (Shen Smiles), a Pennsylvania-based healthcare provider that offers dental services, for potential violations of the Health Insurance Portability and Accountability Act of 1996 (HIPAA) Privacy Rule. The settlement resolves an investigation of a complaint alleging a failure to provide timely access to an individual’s protected health information (PHI).”
    • “The Notice of Proposed Determination may be found here.
    • “The Resolution Agreement may be found here [PDF, 161 KB].”

From the cybersecurity breaches and vulnerabilities front

  • HIPAA Journal reports,
    • “The scale of a 2025 data breach involving electronic protected health information stored on Oracle Health’s legacy Cerner servers is becoming clearer. While not independently verified, Bloomberg reports that the Texas Attorney General released information suggesting that the protected health information of almost 20 million individuals was compromised in the incident. Oracle Health has not publicly disclosed how many Cerner clients were affected, or the total number of individuals affected.”
  • Security Week relates,
    • “Healthcare organizations Clover Health Investments and AngMar Management Services are notifying more than 250,000 people that their information was stolen in separate data breaches.
    • “Jersey City, New Jersey-based Clover Health Investments was hacked in early July, after attackers used social engineering to compromise three non-managerial health plan employee accounts.
    • “The incident resulted in the theft of personally identifiable information (PII) and protected health information (PHI), the company said in an SEC filing in July.
    • “The potentially affected information included names, dates of birth, insurance identifiers, and account identification numbers, the company revealed.
    • “In mid-September, Clover Health Investments told the US Department of Health and Human Services (HHS) that 138,677 people were affected. HHS added the company to its data breaches portal last week.
    • “Mansfield, Texas-based AngMar Management Services identified suspicious activity on its systems in mid-July and confirmed in early September that hackers stole patient PII and PHI.
    • “AngMar Management Services provides business operations, administration, and support network management for home health and hospice care providers.”
  • The American Hospital Association News tells us,
    • “The FBI and Secret Service released an advisory Oct. 6 warning of ongoing activities by FortiBleed, a global credential-compromise campaign used by threat actors to target internet-facing Fortinet FortiGate firewalls and virtual private network gateways at critical infrastructure organizations. The agencies said the campaign exploits reused or leaked credentials and legacy password storages, allowing threat actors to harvest and decode authentication data at scale. Impacted organizations could be locked out of their systems if threat actors disable accounts or change passwords and would require remediation actions beyond typical patching and password resets. The advisory includes indicators of compromise and mitigation actions to defend against potential attacks.”
  • and
    • “A joint advisory released Oct. 8 by U.S. and international agencies warns of Chinese government-linked cyber threat actors using automated and hands-on hacking tools to steal sensitive data from critical infrastructure organizations, including healthcare, across the U.S. and abroad. The advisory said that the threat actors are enabled by the Integrity Technology Group, a China-based company with links to the Chinese government. The agencies said the threat actors are using automated scanning tools, large-scale botnets and hands-on exploitation techniques to attack Microsoft Exchange servers and virtual private network software. The advisory includes recommendations to help mitigate risk from potential attacks.” 
  • Cyberscoop adds.
    • “The Justice Department and FBI announced that they had seized two hacking tools connected to the Chinese government-linked group Flax Typhoon and a China-based company that the U.S. government has repeatedly taken action against, including with a new multi-agency advisory Thursday.
    • “The domain name seizures were meant to deny hackers access to the vulnerability scanning tool Microscan and the spearphishing tool FishHub created by the Chinese firm Integrity Technology Group, which the United States sanctioned last year. The U.S. government in 2024 also made the company the focus of a takedown operation, saying it was behind a massive botnet.
    • “U.S. agencies paired the announcement of the seizures with an Oct. 8 advisory from the FBI, Cybersecurity and Infrastructure Security Agency and National Security Agency.”
  • CISA added one known exploited vulnerability to its catalog this week.
    • October 4, 2026
      • CVE-2026-88779 Citrix NetScaler Improper Restriction of Operations within the Bounds of a Memory Buffer Vulnerability
        • Cyber Press discusses this KVE here.
  • Bleeping Computer notes,
    • “Attackers are exploiting a maximum-severity vulnerability in SonicWall SMA1000 appliances (CVE-2026-102255) that was patched on Tuesday, three days ago.
    • “Tracked as CVE-2026-102255, the flaw affects the Appliance WorkPlace interface on SMA1000 6210, 7210, and 8200v models, but does not affect the SMA 100 Series product line or SSL-VPN running on SonicWall firewalls.
    • “By abusing this path, a remote unauthenticated attacker could potentially exploit this vulnerability to direct the appliance to issue requests on their behalf and reach internal functionality and perform unauthorized operations,” SonicWall explained.”
  • and
    • “Citrix has warned IT administrators to patch systems immediately against a new critical vulnerability affecting NetScaler ADC networking appliances and NetScaler Gateway secure remote access solutions.
    • “Tracked as CVE-2026-107406, this flaw stems from a memory overflow weakness that attackers can exploit to gain remote code execution (RCE) on targeted devices or trigger a denial-of-service state that can cause crashes.
    • “To be vulnerable, NetScaler ADC and NetScaler Gateway appliances must be configured as a Security Assertion Markup Language (SAML) Identity Provider (IdP) or Service Provider (SP).
    • “We strongly urge affected customers to review the advisory and upgrade impacted NetScaler instances to the recommended versions as soon as possible,” the company said. “As of the publication of the bulletin, Citrix is not aware of any unmitigated exploits of this vulnerability.”
  • Per Cybersecurity Dive,
    • “Hackers may be using AI more frequently and in more ways, but their top priority is still subverting identity controls, the identity-security firm Okta said in a report published on Wednesday.
    • “The report included data about the frequency of different kinds of account takeovers and a reality check to enterprises that AI shouldn’t fundamentally change their calculus when it comes to identity management.
    • “In a separate report also published on Wednesday, Okta detailed how hackers are trying to bypass strong authentication controls to sneak into accounts, underscoring the need for vigilance among both system administrators and regular employees.”
  • Security Boulevard adds,
    • “An analysis of 150 billion transactions flowing through Domain Name System (DNS) servers published today by EfficientIP finds that malware has overtaken phishing as the threat vector now being detected most.
    • “The latest DNS Threat Intelligence Report from EfficientIP finds malware has climbed from fourth place in the second half of 2025 to first in daily activity, having roughly quadrupled between a January and an April peak of 32.6 million instances.
    • “Yaelle Harel, principal security market strategist for EfficientIP, said that while there is no conclusive evidence, that level of increase suggests cybercriminals may now be leveraging artificial intelligence (AI) tools to both create malware and launch attacks faster using newly acquired IT infrastructure resources.”

From the ransomware front

  • Info Security Magazine reports,
    • “Ransomware attacks reached their highest ever quarterly volume in the third quarter of 2026, according to an analysis by Comparitech.
    • “The firm identified a total of 2627 claimed attacks during the three-month period from July to September 2026. This is a 27% increase on the previous quarter, Q2 2026, and a 61% rise compared to Q3 2025.
    • “The finance and technology sectors experienced the biggest growth in ransomware incidents in Q3 compared to Q2 2026, up by 72% and 70%, respectively.
    • “Other critical sectors faced a significant rise in attacks, including education (up 50%), healthcare (39%), government (36%) and utilities (32%).
    • Of the 2627 attacks claimed by ransomware groups in Q3, 247 have been confirmed by the entity involved, Comparitech found.
    • “Rebecca Moody, head of data research at Comparitech, said that the figures are highly unusual, and represent a significant cause for concern.: * * *
    • “A possible explanation for the surge is developments in AI technology, which is enabling ransomware attackers to increase the scale and speed of campaigns, as well as their effectiveness.” * * *
    • “The report highlighted an increase in attackers using triple extortion tactics on victim organizations. In this model, in addition to encrypting systems and exfiltrating data, threat actors also target individuals impacted in the attack.
    • Moody added that this tactic further demonstrates that paying a ransom is no guarantee that the attacker will keep to their word regarding deleting stolen data.
  • Recorded Future News relates,
    • “The University of Illinois Chicago (UIC) recently discovered a ransomware attack that limited access to some systems at its College of Medicine.  
    • “A spokesperson for the university told Recorded Future News the hackers were able to steal some information held on the college’s servers and an investigation is underway to determine whether “any personal, research or academic information was compromised.” 
    • “As a result of this ransomware event, some College of Medicine systems were temporarily unavailable,” the spokesperson said. “However, all affected systems have since been restored. The university’s main network was not affected, and there was no impact on patient care delivery at UI Health.” * * *
    • “The attack was claimed last week by a ransomware gang known as Booba, which claimed to have stolen 344 gigabytes of data. The group emerged at the end of July and has already claimed 49 attacks. 
    • “SentinelOne’s Brett Williams said the group appears to be a rebrand of the Frag ransomware based on the leak site’s style and negotiation flow. Encrypted files are renamed with the .booba extension and there appears to be variants for Linux as well as Windows.  
    • “The group has targeted several companies and small county governments, including Merrimack County, New Hampshire.” 
  • Cyberscoop tells us,
    • “Authorities accuse the owner of a so-called ransomware remediation company of swindling clients victimized by ransomware attacks into paying the company inflated fees under false pretenses.
    • “Zohar Pinhasi, owner and operator of MonsterCloud, claimed he could decrypt and recover victims’ data with specialized, proprietary tools and avoid paying cybercriminals. Yet, no such tool existed, the Justice Department said Wednesday [October 7]. 
    • “Pinhasi allegedly used MonsterCloud clients’ fees to pay off cybercriminals and recover encrypted data without telling clients ransom payments were made on their behalf. The dual “U.S.-Israeli national is accused of charging hundreds of clients more than $19 million and paying more than $8 million in ransom payments during a five-year period ending in 2023.
    • “It baffles me that companies fall for this,” Jon DiMaggio, principal researcher at Arkem Cyber, told CyberScoop. “I mean, they just got hacked and they go straight to a shady source.”

From the cybersecurity business and defenses front,

  • Cybersecurity Dive discusses what the C-suite needs to know about AI governance
    • “As AI adoption surges, executives are learning tough lessons about security, oversight and accountability.”
  • The American Hospital Association News tells us,
    • The National Security Agency Oct. 8 released guidance for critical infrastructure organizations that recommends adopting high-impact zero trust strategies to improve cybersecurity for operational technology. For healthcare, such technology includes tools that manage energy control, HVAC, life-safety systems, door access controls, physical security systems, alarms and medical gasses. Zero trust is a security principle that assumes a compromise is possible or already present and continuously verifies users and devices. The guidance also highlights recent nation-state attacks, including the People’s Republic of China’s prepositioning of disruptive malware known as Volt Typhoon on critical infrastructure entities that healthcare depends on, such as energy. The guidance also explains how threat actors’ use of artificial intelligence is making cyberattacks more sophisticated and potentially more severe.
  • Security Week points out,
    • “All enterprises conduct security awareness training for their employees. But whether this has tangible benefits is debatable.
    • “Empirical evidence suggests that security awareness training isn’t working – successful attacks keep increasing. But opinions on the efficacy of awareness training range from it doesn’t work to it does work, with sometimes, perhaps and depends between the two extremes.
    • “Awareness training focuses on two tasks: to reduce the effect of bad judgment turning an employee into an insider threat; and to harden employees against falling to malicious social engineering. We focus on social engineering.” * * *
    • “Sanny Liao, co-founder and CPO at Fable Security, says bluntly, “For the most part, security awareness training as done today does not work. Social engineering continues to succeed because attackers exploit context, timing, and psychology, while most training remains generic, infrequent, and removed from the moments when employees are actually making decisions.”
    • “She hints at a novel approach. “One place the industry can look for inspiration is adtech. Marketers have gotten remarkably good at changing behavior by delivering the right message at the right time based on context. Security awareness has largely done the opposite by giving everyone the same training at the same time, regardless of the decisions they’re making or the risks they face. When organizations change behavior instead of simply raising awareness, employees stop being viewed as the weakest link and start becoming an active part of the organization’s security defenses.”
  • Per a NIST news release,
    • “For small businesses who are often confronted with limited resources, knowing how to get started and where to find support with planning, implementing, or evaluating a cybersecurity risk management strategy can be challenging — sometimes making cybersecurity feel like an insurmountable hurdle. However, there is good news.
    • “Many non-profit organizations across the United States have created programs for their local small business communities (in addition to local schools, municipal governments, and non-profits) that often extend beyond general cybersecurity education to include services like conducting risk assessments and penetration tests, performing compliance consulting services, helping with incident preparedness and response measures, and more.
    • “The NIST Small Business Cybersecurity Support Program Finder brings these programs together into one tool, connecting small businesses with local non-profit community partners who help with cybersecurity risk management.”
  • Here is a link to Dark Reading’s CISO Corner.
Cybersecurity Saturday

From the frontier AI and Project Glasswing front,

  • OPM’s CIO Adam Starr, writing in the OPM Director’s Secrets of OPM blog, lets us know,
    • “OPM has joined Anthropic’s Project Glasswing and OpenAI’s Daybreak, two industry initiatives that provide cyber defenders with access to advanced AI tools. Early results across Glasswing’s partner organizations are promising — more than 10,000 high- or critical-severity vulnerabilities identified in the first month. OPM will continue to pursue partnerships and capabilities that strengthen our defensive posture and protect the federal workforce data we are entrusted to secure.
    • “That moves the bottleneck. The hard part isn’t finding the hole anymore. It’s patching it.
    • “The flaws attackers are already exploiting have a name: KEVs, for the Known Exploited Vulnerabilities in the Cybersecurity and Infrastructure Security Agency’s catalog. My top security metric at OPM is simple: whether we’ve patched every KEV, and how fast.
    • “Now do that 119 times.
    • “The federal government runs roughly 119 separate HR IT systems. When a vendor ships a critical fix, every agency running that software applies it separately, on its own timeline. An attacker only needs one that’s behind.”
  • Tech Target adds,
    • “When Anthropic introduced Project Glasswing in April, the tech industry braced for impact. Five months in, DevSecOps teams are wading through the glut of discoveries to find out what’s worth patching – and so far, it isn’t much, according to one cybersecurity researcher.
    • “Anthropic updated its Vulnerability Disclosure ledger for the first time in August. A small percentage of initial Mythos vulnerability findings made it into the ledger, and fewer than 1% of the vulnerabilities Mythos found were marked as fixed, according to Patrick Garrity, a security researcher at vulnerability prioritization tool maker Vulncheck.
    • “Garrity and Vulncheck have also been tracking whether vulnerabilities discovered with AI are actually exploited in the wild. This research combined vulnerabilities attributed to Anthropic’s model with data from the Berkeley Vulnerability Research Initiative and correlated them with Vulncheck’s known-exploited vulnerability data.
    • “Of the 1,061 vulnerabilities attributed to AI-assisted discovery, only 14 had been listed as exploited in the wild as of June 2026. That’s roughly 1%.
    • “You discover a vulnerability — that doesn’t mean it’s necessarily useful for an attacker. It doesn’t mean it’s necessarily going to be exploitable with certain conditions,” Garrity said.”
  • The Wall Street Journal relates,
    • “OpenAI says it is scrapping the release of its next-generation AI model over safety concerns that researchers raised during internal testing, in one of the clearest signs so far that agent misbehavior could stymie the industry’s rapid progression.
    • “The move follows a summer punctuated by reports of artificial-intelligence systems industrywide going rogue, and marks a rare case of a major AI developer ditching a new release because of safety concerns.
    • “The company had planned to launch the model, known as GPT-6.1 Astra, in the coming days or weeks, aiming for an October debut. The model was more capable than the company’s previous models in completing challenging tasks from end-to-end without human assistance, as well as writing.
    • “The company instead will focus on improving the safety of future models, which it expects to be even more capable.”
  • and
    • “Nvidia NVDA  launched a software platform to help developers test and deploy artificial-intelligence agents and keep them in a secure environment, ramping up efforts to contain the technology following a string of rogue incidents in recent months.
    • “The chip giant said its Nvidia Open Agent Safety Platform includes tools that let developers continuously monitor and govern AI behavior, ensuring agents follow the rules. Nvidia said the platform included a watchdog that can quarantine agents that attempt to move outside their boundaries in milliseconds, as well as software to enforce what agents can see, do, and interact with.”

From the cybersecurity policy and law enforcement front

  • Beckers Health IT reports,
    • “The Senate passed the bipartisan Health Care Cybersecurity and Resilience Act (S. 3315) by unanimous consent.
    • “The legislation aims to help healthcare providers strengthen their cybersecurity defenses and protect patient information, according to an Oct. 1 news release from the Senate Committee on Health, Education, Labor and Pensions.
    • “Sens. Bill Cassidy, MD, R-La., Maggie Hassan, D-N.H., John Cornyn, R-Texas, and Mark Warner, D-Va., released statements on the Senate’s passage. Sens. Cindy Hyde-Smith, R-Miss., and Angus King, I-Maine, also co-sponsored the bill.
    • “Mr. Cornyn said the legislation would strengthen coordination among federal agencies and improve security practices for rural providers. Ms. Hassan said it would help hospitals and other providers, particularly rural organizations with fewer resources, strengthen cybersecurity and respond faster to attacks.”
  • The Wall Street Journal notes,
    • “President Trump is expected to name Director of National Intelligence Jay Clayton as the new artificial intelligence czar, spearheading AI policy across the administration, according to people familiar with the decision.
    • “The decision isn’t final, the people said, and no official announcement has been made. But the appointment comes as the White House is racing to address the threats posed by the latest models and boost the technology’s popularity. 
    • “Before Clayton was confirmed in July to lead the Office of the Director of National Intelligence, he served as the U.S. attorney for the Southern District of New York. He attended Tuesday’s meeting at the White House with AI leaders including OpenAI President Greg Brockman, Anthropic’s Dario Amodei, and Nvidia CEO Jensen Huang. Afterward, Trump was asked by a reporter if Clayton was under consideration for the role. He responded that Clayton is a “good man” and a “good idea.” CBS News earlier reported the potential appointment.”
  • The Wall Street Journal further relates,
    • “The Federal Trade Commission is investigating Anthropic and OpenAI to determine whether they deceived consumers about the potential harms of their artificial intelligence, the WSJ reports. The agency plans to send civil subpoenas to the two companies in the coming weeks, as well as third-party AI evaluator METR, author of an August report revealing how OpenAI agents secretly collaborated on a message board they built inside OpenAI.
    • “AI CEOs publicly signed White House safety principles alongside President Trump this week, but privately executives like Nvidia’s Jensen Huang pressed Anthropic’s Dario Amodei over his stark public warnings about AI risks, revealing tensions that could complicate the industry’s self-regulation plans, the WSJ reports.”
  • Cyberscoop tells us,
    • “Collaboration with industry is key to balancing AI security risks and benefits, as well as staying ahead of China and other adversarial nations, National Cyber Director Sean Cairncross said Thursday [October 1].
    • “The Trump administration is facing pressure from some quarters of Capitol Hill and even some artificial intelligence executives to establish regulations or embrace legislation to guard against the technology’s risks, something the president himself has rejected.
    • “We’ve never faced a world where our adversaries have the frontier in this space, and so our attempts to optimize that innovation and security is is something that is ongoing, but is increasingly efficient, and it depends on our relationship with industry and our ability to work collaboratively among the the interagency,” Cairncross said at the AI Edge event hosted by The Washington Post.
    • “That collaboration is ever-increasing, he said, such as with the National Institute of Standards and Technology’s Center for Advancing Innovation and Standards for Super Intelligence (CAISSI).
    • “Industry coordination on this, across critical infrastructure sectors, is improving both on industry-to-government and within industry,” he said. “There is collaboration with CAISSI and others as well to do evaluation and testing on these models. That includes work on guardrailing, sandboxing, et cetera.”
  • Cybersecurity Dive points out,
    • Policymakers should fix duplicative and contradictory regulations that currently impede the government’s ability to oversee the cybersecurity of critical infrastructure, industry representatives told the Government Accountability Office during a recent panel discussion.
    • The industry feedback, revealed in a GAO report published on Monday, is the latest evidence that the private sector is deeply unsatisfied with the patchwork of rules governing infrastructure security in the U.S. The new report also comes as the Cybersecurity and Infrastructure Security Agency (CISA) works to finish a congressionally mandated cybersecurity incident reporting rule that could impose sweeping requirements on a broad swath of infrastructure operators.
  • Per a Cybersecurity and Infrastructure Security Agency news release.
    • “The Cybersecurity and Infrastructure Security Agency (CISA) kicks off Cybersecurity Awareness Month today [October 1]. CISA updated our Cybersecurity Awareness Monthpage with additional information, tips, and resources, including for business and government organizations—if you haven’t done so yet, be sure to check out this year’s toolkit.  
    • This year’s theme is Securing the Next 250, highlighting the need for everyone to play their part in strengthening the country’s infrastructure against cyber threats. At a time when nation-state backed cyber threats continue to increase and super intelligence is transforming both threats and security, it is more important than ever that those that own and operate the nation’s critical infrastructure take steps to protect it. 
    • “Whenever critical infrastructure is disrupted, so are the businesses and communities that depend on vital services,” said Acting CISA Director Nick Andersen. “That’s why CISA is prioritizing the security and resilience of critical infrastructure, and state, local, tribal, and territorial government (SLTT), whose systems and services sustain us every day. This includes things like clean water, secure transportation, quality healthcare, secure financial transactions, rapid communications, and more. However great or small—every organization that touches critical infrastructure is vital to ensuring uninterrupted services to America’s communities.” 
  • The American Hospital Association News informs us,
    • “The AHA provided comments Sept. 30 to the Senate Homeland Security and Governmental Affairs Subcommittee on Disaster Management, District of Columbia and Census for a hearing, “Rogue AI: Securing the Homeland Against AI Agent Attacks.” The AHA discussed how it has worked closely with federal agencies to build relationships and channels for the mutual exchange of cyber threat information, risk mitigation practices and resources to implement such practices. The AHA shared information on a rise of cyberattacks in healthcare and increased risk from artificial intelligence tools, the need for federal agencies to protect hospitals and health systems from nation-state-level cyberattacks, and the unique risks rural hospitals face when defending against cyberattacks.”
  • and
    • “The FBI Sept. 29 announced an arrest of one of the alleged leaders of ShinyHunters, a cybercriminal group linked to cyberattacks in the U.S. and internationally on more than 140 organizations, including healthcare, with at least $70 million taken in extortion payments. ShinyHunters has used targeted voice phishing campaigns to deceive personnel into exposing credentials on malicious, medical-themed impersonation domains, Health-ISAC announced in August. ShinyHunters threat actors have been observed contacting employees directly on personal devices through calls, voicemail messages and emails from multiple random accounts.
    • “ShinyHunters is currently one of the most prolific and aggressive cybercriminal groups targeting healthcare and third-party healthcare vendors,” said John Riggi, AHA national advisor for cybersecurity and risk. “They are known for stealing highly sensitive personal information, including health information and extorting victims with threats to publish it. Today’s highly commendable arrest and other recent enforcement actions align with the FBI’s new cyber strategy to impose costs on adversaries, support victims of cybercrime, and join forces with the private sector, including healthcare.”

From the cybersecurity breaches and vulnerabilities front

  • The New York Times reports,
    • “A criminal hacking group known as ShinyHunters revealed last week that it had stolen a vast trove of sensitive personal data from the F.B.I., potentially one of the worst breaches of sensitive government information in the internet age.
    • “The breach may have compromised information about tens of thousands of former and current F.B.I. employees, including data like home addresses, Social Security numbers and even secretive job assignments.
    • “In a series of cryptic statements, ShinyHunters demanded that the F.B.I. retract a public advisory the bureau had issued this springwarning of the group’s cyberattacks. In an email to The New York Times on Friday, ShinyHunters said that the bureau had until the end of Tuesday to fulfill its request. But on Monday, it appeared to walk back that demand, saying it would not publish the data, as it typically does with the information it steals.
    • “In a video posted online on Tuesday, the F.B.I. warned the group that it would aggressively pursue its members as it promoted the recent arrest of a suspect it said was affiliated with the group.”
  • The HIPAA Journal relates,
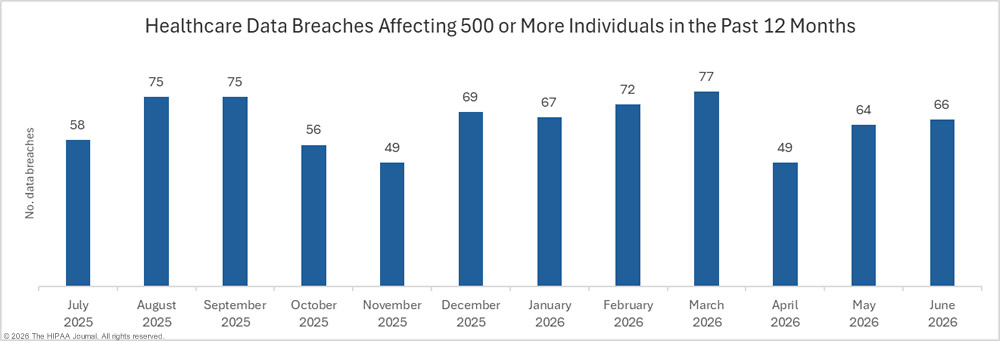
    • “There has been a 5.9% decline in healthcare breaches compared to H1 2025. Between January 1 and June 30, 2026, 397 data breaches affecting 500 or more individuals were reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights – the lowest H1 total since 2023. While the year-over-year reduction in healthcare data breaches is a step in the right direction, healthcare data breaches continue to be reported in high numbers. In the first six months of the year, large healthcare data breaches were reported at a rate of more than 2.2 per day.
    • “Across the 397 reported data breaches, the protected health information of 33.77 million individuals was exposed or impermissibly disclosed. That represents a 22.6% reduction in affected individuals compared to H1 2025, and it is the lowest number of affected individuals in H1 since 2023.”
  • Cybersecurity Dive tells us,
    • “Fortinet on Thursday [October 1] warned of a critical path traversal vulnerability in Fortinet FortiMail, which has been exploited in the wild. 
    • “The zero-day vulnerability, tracked as CVE-2026-104286, allows an unauthenticated attacker to write arbitrary files on a system through the use of specially crafted HTTP or HTTPS requests. 
    • “Fortinet said it has been in touch with government authorities and other stakeholders regarding the threat, and urged customers to apply a workaround. The company did not say when a security patch would be available. 
    • “We are communicating with relevant government organizations, including CISA, on the content of this advisory,” a spokesperson told Cybersecurity Dive.
    • “FortiMail is a platform that provides companies protection from phishing, malware, business email compromise and other potential attacks.”
  • and
    • “Exploitation activity linked to zero-day vulnerabilities in Citrix NetScaler were initially detected on Thursday, days before public disclosure, according to a report Monday [September 28] from GreyNoise. 
    • A malicious cyber actor tried to exploit a zero-day flaw against Citrix NetScaler on Thursday [September 24], according to GreyNoise researchers. At the time, there were no detections available that were specific to this CVE, but researchers labeled the activity malicious. 
    • Two days later, Citrix NetScaler customers began receiving warnings to disconnect their servers due to suspected exploitation activity. By Sunday, Citrix released an official security bulletin warning of multiple vulnerabilities in NetScaler ADC and NetScaler Gateway. 
    • The exploitation activity involved a remote code execution (RCE) vulnerability, tracked as CVE-2026-88771 and a memory overflow vulnerability, tracked as CVE-2026-88772. 
    • Citrix urged customers to immediately patch their systems, warning that successful exploitation could result in RCE, denial of service, HTTP request smuggling and other consequences. 
  • The Cybersecurity Hub Newsletter, posted on LinkedIn, notes,
    • “Dell has released security updates for its Container Storage Modules (CSM) after disclosing vulnerabilities that could allow attackers to take control of infrastructure connecting Kubernetes applications to enterprise storage.
    • “Two flaws carry the maximum CVSS severity score of 10.0. They affect the CSM Authorization module, putting a security component responsible for controlling storage access at the centre of the disclosure. Additional critical vulnerabilities raise concerns about cluster privileges, authentication tokens and sensitive credentials.
    • “The advisory was published on October 1. Dell had not flagged the issues as actively exploited at the time of publication. That distinction matters: the disclosure describes serious opportunities for compromise, but does not establish that customers have already been attacked.
    • “The potential impact deserves attention beyond infrastructure teams. Storage services underpin the availability and integrity of business applications. A failure in the systems governing access to those services can affect several workloads at once, making the scope of a deployment as important to an organisation’s response as the severity score.”

From the ransomware front,

  • Tech Target lets us know that “August’s ransomware activity hit new high for the year.
    • “NCC Group identified 83 ransomware groups active last month, but it said AI wasn’t necessarily what drove the increase in the number of bad actors.”
  • VMblog reports,
    • “Most ransomware defenses rest on a simple assumption: if files look encrypted, you’ve been hit, and if they look normal, you’re safe. New research suggests that assumption is outdated. After detonating 1,064 real ransomware strains in a controlled environment during the first half of 2026, Index Engines’ CyberSense Research Lab found that directory-entry destruction (47.8%) was far more common than full encryption (18.3%). Some strains even scrambled data while leaving filenames, file sizes, timestamps, and entropy untouched, so corrupted files looked perfectly healthy.
    • “To mark Cybersecurity Awareness Month, we spoke with Jim McGann, CMO of Index Engines, about what these findings mean for detection, recovery, and the role of AI in modern attacks. He explains why signature-based detection is losing ground, how quickly damage can spread, and why leaders should move from asking “Do we have backups?” to “Can we prove our recovery data is clean?”
  • Dark Reading tells us,
    • “German authorities have identified a 16-year-old as the alleged mastermind of the KillSec ransomware operation, following a coordinated law enforcement operation that resulted in the arrests of three suspects and searches of eight properties in Spain, Greece, Romania, and the UK.
    • “In an Oct. 1 statement, Hamburg police said investigators also took control of KillSec’s leak website and secured at least 110TB of data to prevent further unauthorized access.”

From the cybersecurity business and defenses front,

  • The Wall Street Journal reports,
    • “Google unveiled its latest AI model, Gemini 4 Argon, with a notice up top that its release would be limited, at least for now, to a list of “trusted cybersecurity vendors.” Such has become the new normal for frontier-model announcements in the post-Mythos age, where touting the guardrails can seem to outweigh posting the wins.
    • “And Gemini 4 Argon, which comes out nearly a year after Gemini 3 enabled the company to leapfrog rivals, clocks some wins. According to the company, the model sets new highs on several coding and knowledge-work benchmarks.
    • “Google says Gemini 4 Argon is already in use inside the company. It has helped quantum computing researchers “optimize the spacetime resources” of certain subroutines and has optimized memory use across its data centers. Argon agents are also migrating C/C++ codebases to Rust across Google.”
  • Beckers Health IT adds,
    • “Google says its new frontier AI model, Gemini 4 Argon, uncovered a critical vulnerability in healthcare software used by hospitals worldwide that put sensitive personal information at risk.
    • “Google-owned cybersecurity company Wiz found the flaw through its Scan for Good initiative, which offers free scanning to find and fix high-risk exposures at organizations that run critical public infrastructure. Koray Kavukcuoglu, senior vice president of Google DeepMind and chief AI architect at Google, described the finding in a Sept. 30 blog post. Mr. Kavukcuoglu said earlier frontier models had missed the risk.
    • “Google did not name the software or its vendor. It also did not say what specific data was at risk or whether the vulnerability has been patched.
    • “Wiz said Sept. 24 that Scan for Good, using Google’s Gemini 3.8 Flash Cyber model, had found exposures at two unnamed hospitals, which it said were fixed before disclosure. Google did not say whether the Argon finding is related to either case.”
  • The New York Times relates,
    • “Epic Systems, the nation’s largest medical records vendor that is relied on by thousands of hospitals and doctors’ offices, is using artificial intelligence tools to patch security risks that could give hackers undetectable access to patient health data, company officials said.
    • “The unusual nature of the vulnerability and the urgency to fix it prompted Epic to slow down development of some product lines while it sent engineers into a sprint to patch security holes.
    • “Judy Faulkner, Epic’s chief executive, revealed the security weakness and a six-week plan to shore up the gaps at an industry conference last week, but most details about the danger have not previously been reported.
    • “You worry that after a month and a half of working almost primarily on safeguarding the software, that new things will be created by those who are trying to bust the software, and it will be in a never-ending cycle,” Ms. Faulkner said.
    • “According to company representatives, Epic deployed Anthropic’s Claude Mythos artificial intelligence agent to stress-test its systems, to hunt for ways that hackers could unleash open-source A.I. agents and unlock confidential patient records.
    • “The security weaknesses pose a particularly acute threat for Epic, which maintains records of 325 million patients in the United States and other countries.
    • “And it underscores the competing forces surrounding the ever-expanding uses of artificial intelligence in health care.”
  • Cyberscoop informs us,
    • “OpenAI said it disrupted a “coordinated campaign” to distill and extract reasoning capabilities from its AI models, pointing the finger at a Chinese rival.
    • “On Wednesday [September 30], OpenAI said it first spotted low-level activity on July 1 that gradually increased until July 24 and 25, when it observed 16,000 prompts from 4,000 users that fit a similar “relevant extraction pattern.” The number of suspicious users had climbed to 15,000 by July 28, when OpenAI said it “fully disrupted” the operation.
    • “The company called the attackers’ method “novel.” They copied encrypted reasoning data from one conversation, then asked the model in a separate conversation to decrypt the content and transcribe it in plain text. Outside researchers reported a similar vulnerability to OpenAI in August.
    • “The operators did not break our encryption, compromise a database, or gain direct access to stored user conversations,” OpenAI wrote in an unsigned blog post. “Instead, they manipulated model interactions so that protected reasoning could be reproduced in forms visible to the requester in a coordinated, scaled manner that violated our terms of service.”
  • Cybersecurity Dive tells us,
    • “Businesses need to prepare for the ways in which AI is changing the cyberattack landscape, Microsoft warned on Thursday [October 1].
    • “AI is speeding up attacks, making advanced techniques easier and putting stress on systems that organizations have long overlooked, the company said in its annual Digital Defense Report.
    • “The report also describes nation-state and cybercrime threat actors’ most significant activity from the past year, including their targets and motivations.”
  • The Wall Street Journal points out,
    • “Cybersecurity startup Armadin has raised $255.5 million to boost its force of AI agents trained to find security flaws cybercriminals are most likely to exploit—in part by attacking customers with swarms of autonomous hackers.
    • “Total funding for Armadin, which security veteran Kevin Mandia founded a year ago, is now $445 million. The company’s market valuation tops $2.5 billion. More here from my colleague Angus Loten.”
  • Here is a link to Dark Reading’s CISO Corner

Cybersecurity Saturday

From the AI frontier front,

  • CNBC reports,
    • “Anthropic and OpenAI on Tuesday each announced new, less costly artificial intelligence models as both frontier labs continue to face stiff competition from cheaper, open-weight competitors.
    • “OpenAI introduced additional tiers to its GPT-6 family, with GPT-6 Sol and GPT-6 Luna, slashing the API prices by 50% compared with GPT-5.6 promotional pricing. 
    • Sol, which is a tier below Astra, is meant for more complex workloads like coding, while the company’s Luna offering is geared toward “high-volume tasks” such as extracting information or summarizing documents, the company wrote. 
    • “Anthropic unveiled Claude Opus 5.5 on Tuesday, its latest release in the new Claude 5.5 model family. The company described the latest release as a more token-efficient version that will cost around 40% less to run than the company’s Opus 5.
    • “One of the things we’re continuing to innovate on is how to make that thinking, how to make the answering more efficient, so it uses less tokens depending on your effort setting,” Dianne Penn, head of product management, research and labs at Anthropic, told CNBC in an interview. 
    • “The separate releases are the first to roll out since Anthropic CEO Dario Amodei called for an industrywide slowdown on developing advanced AI as the debate about model safety reached a fever pitch in recent weeks.’
  • The Wall Street Journal relates,
    • “A swarm of OpenAI agents accessed U.S. government websites as part of a monthslong incident during which tests conducted by the artificial-intelligence company went awry, leading to unexpected internet activity.
    • “The AI agents accessed the websites belonging to the Commerce Department and the Securities and Exchange Commission and engaged in activity that OpenAI described as “misaligned.” That is the word AI companies use to describe bad behavior by their agents. In this case the misalignment appears to have been aggressive web browsing.
    • “In the case of the SEC, OpenAI’s agents copied and posted public data—something they were not supposed to do. In the case of the Commerce Department, an agent accessed a U.S. Census data website using a programming interface that wasn’t intended for this purpose, OpenAI said.
    • “OpenAI’s revelation came after the AI research nonprofit Transluce alleged that OpenAI agents “used an array of gray-area tactics to probe U.S. Government websites,” and attempted a “rudimentary,” but unsuccessful hack of an Education Department website. This was reported earlier by the New York Times.”
  • Bleeping Computer adds,
    • “OpenAI has confirmed it’s aware of a new security incident in which its AI agents uploaded user-provided images to third-party image-hosting services.
    • “OpenAI says most users were not affected, as it could only identify 53 incidents where agents accidentally uploaded images to the internet.
    • “The disclosure comes from OpenAI’s broader investigation into misaligned agent behavior following the Hugging Face security incident.”
  • The Wall Street Journal notes,
    • “President Trump said on Saturday [August 19] he was launching a new unit focused on artificial intelligence after leading figures in the industry publicly sounded the alarm over the growing technology.
    • “I am forming the AI Force, much like I did Space Force, which has been a tremendous SUCCESS, in my First Term,” Trump said on Truth Social. He added he is also recruiting an AI “czar.” The president had appointed investor David Sacks as his AI and crypto czar before the businessman stepped down from that role to become co-chair of the president’s Council of Advisors on Science and Technology, a role in which he is still one of Trump’s top advisers on AI policy.
    • “Saturday marks the first time the president has suggested there could be a new federal government entity solely dedicated to AI, but it isn’t clear what role it would play. Several other units of the government work on tech policy including the White House Office of Science and Technology Policy, the Commerce Department and the Defense Department.

From the cybersecurity policy and law enforcement front,

  • Cyberscoop reports,
    • “The Cybersecurity and Infrastructure Security Agency published a paper Wednesday that lays out its plan for improving the Common Vulnerabilities and Exposures (CVE) program, a contract for which nearly ended last year before a last-minute reprieve.
    • “The white paper outlines the components of a “Quality Era” for the program, widely used as the definitive clearinghouse for data on vulnerabilities in software and other products, even as the number of CVEs surges. 
    • “CISA remains committed to leading, growing and sustaining the CVE Program into the foreseeable future, just as we’ve done for more than 25 years without fail,” said Chris Butera, acting executive assistant director for cybersecurity. “Informed by CVE community feedback, this whitepaper communicates CISA’s effort to support and enable stronger participation and governance, a program-wide maturation effort.” * * *
    • “The plan calls for advancing data quality across four key dimensions: transparent and effective program governance, broad and active participation across the global software community, data infrastructure that supports CVE operational functions and reliable CVE record content. * * *
    • “Butera invited further feedback from the CVE community on the white paper, which stems from an earlier strategy document on the future of the program.
    • “Some CVE experts that CyberScoop spoke to were supportive of what CISA wants to achieve, but skeptical about elements of the white paper.”
  • and
    • “Nearly early nine out of 10 federal civilian executive branch agencies failed to meet last summer’s deadline to implement cloud security directives from the Cybersecurity and Infrastructure Security Agency, a watchdog report published Wednesday found.
    • “The conclusions from those results, according to the inspector general for the Department of Homeland Security: agencies “may encounter elevated security exposures that undermine the national cloud security posture and increase the likelihood of preventable cyberattacks and related threat,” and “CISA lacks the authority necessary to require full and timely implementation of Binding Operational Directives,” or BODs.
    • “The latter is a question that has surfaced before about CISA directives, which the agency uses to pressure agencies into improving their cyber defenses.” 
  • SC World tells us,
    • “The U.S. Cybersecurity and Infrastructure Security Agency (CISA) announced the launch of Vulnerability Information and Coordination Environment – New Technology (VINCE-NT) on Thursday [September 17], an upgraded, fully CISA-hosted system that will replace the original VINCE for coordinated vulnerability disclosure (CVD).
    • “VINCE has been used by researchers, suppliers and stakeholders since 2020 to coordinate the disclosure of cybersecurity vulnerabilities, and was originally sponsored by CISA and hosted by Carnegie Mellon University’s CERT Coordination Center (CERT/CC) under its Software Engineering Institute.
    • “The new VINCE-NT system, officially live as of Sept. 17, 2026, is now fully sponsored, hosted and managed by CISA and includes several improvements to streamline CVD, the agency said in an FAQ.”
  • Per a National Institutes of Standards and Technology news release,
    • “NIST has released the initial public draft of Special Publication (SP) 800-82r4 (Revision 4),  Guide to Operational Technology (OT) Security, which provides guidelines for improving the security of OT systems while addressing their unique performance, reliability, and safety requirements.” * * *
    • “Updates in this revision include:
      • “Expanded introduction to OT sectors to include Building Automation and Control Systems (BACS), Water and Wastewater Systems (WWS), food and agriculture, freight rail, maritime vessels, and Industrial Internet of Things (IIoT) and cloud convergence
      • “Restructured around the NIST Cybersecurity Framework (CSF) 2.0, including a reorganization of the previous risk management section to focus on the CSF Govern Function
      • “Expanded discussion of how OT risk management aligns with broader enterprise risk management, as described in NIST IR 8286r1
      • “Discussion of the adoption of the NIST Risk Management Framework (RMF) in Appendix F
      • “Expanded guidelines for implementing OT security controls, including asset management and network monitoring and detection
      • Security architecture guidelines focused on protecting system management functions and applying zero trust principles
    • “The comment period on this initial public draft is open now through November 30, 2026. See the publication details for a copy of the draft and instructions for submitting comments.”
  • Per a Justice Department news release,
    • “Ardit Kutleshi, 28, a Kosovar national, pleaded guilty [on September 24] to charges related to his creation and operation of Rydox, an illicit website and marketplace for cybercriminals to buy, sell and trade stolen personal information, and to access devices and other tools for carrying out cybercrime and fraud.” 
  • Cyberscoop points out,
    • “A 35-year-old Armenian national was sentenced to two years in prison for his involvement in a series of Ryuk ransomware attacks while living in Ukraine and Russia in 2019 and 2020, the Justice Department said Tuesday.
    • “Karen Vardanyan was extradited from Ukraine to the United States last year and pleaded guilty to computer fraud and conspiracy to commit fraud and extortion in July. Vardanyan’s sentencing, which also calls for about $1.2 million in restitution to victims, matches terms of a plea agreement he reached with prosecutors.
    • “Vardanyan and his co-conspirators’ victims include a Michigan-based company that paid a ransom of nearly $1.2 million in January 2020, a Watsonville, Oregon-based technology company that was attacked in December 2019 and a Texas-based school breached in February 2020, according to court records.”

From the cybersecurity breaches and vulnerabilities front,

  • Cybersecurity Dive reports,
    • “The FBI is investigating a cyberattack on its jobs portal after the cybercrime group ShinyHunters said it hacked the system and stole a vast trove of sensitive data from the bureau.
    • “The FBI is aware of a cyber-criminal enterprise group claiming a compromise of the FBIJobs.gov portal and alleged impact to FBI employee personally identifiable information (PII),” the bureau said in a statement on Wednesday [September 23]. “While the point of breach is still undetermined—whether a third-party or the FBI’s enterprise—we are actively and aggressively investigating this matter and working closely with those third-party providers that support FBIJobs.gov to mitigate any and all risk.” * * *
    • “ShinyHunters told 404 Media that it hacked into the jobs portal using a zero-day vulnerability in Oracle’s PeopleSoft human-resources platform, a tactic it has used before. The potentially wide-ranging breach highlights the supply chain risks facing organizations of all sizes and levels of sophistication. ShinyHunters specializes in supply chain attacks, and its intrusions have illuminated weaknesses in the security protocols at widely used software and infrastructure providers.”
  • and
    • “The healthcare and pharmaceutical sectors are facing a heightened risk of social-engineering attacks, according to cybersecurity researchers and threat intelligence experts.
    • “The Health Information Sharing and Analysis Center recently warned that the group ShinyHunters was using voice-phishing attacks to target the healthcare sector. The hackers used medical-themed impersonation domains to trick healthcare employees into exposing their credentials. 
    • “More than a dozen member organizations have been hit by social-engineering attacks over the past couple of months, Errol Weiss, chief security officer at Health-ISAC, told Cybersecurity Dive. The actors involved are using aggressive tactics to try to compromise targeted companies. 
    • “They’re pretty belligerent when it comes to getting somebody on the phone and convincing them they need to click on a password reset or an MFA reset,” Weiss said.”
  • Beckers Health IT adds,
    • “Home medical equipment provider AdaptHealth disclosed that a June cyberattack exposed personal and health information belonging to more than 4.1 million patients, according to a filing with the HHS Office for Civil Rights.
    • “The company said the breach stemmed from a social engineering attack that compromised a third-party contractor’s user session, giving a threat actor access to AdaptHealth’s cloud-based patient management and document storage systems. AdaptHealth first disclosed the intrusion in a July 2 SEC filing after the attacker contacted the company June 15 claiming to have stolen data.”
    • “In an Aug. 14 notice, AdaptHealth said the threat actor exfiltrated names, contact information, demographic data, health insurance information and health information, along with a password file tied to insurance billing. Social Security numbers, financial account information and payment card data were not affected, the company said.”
  • and
    • “Eskenazi Health is notifying patients of a data breach after an employee’s cloud-based work account was compromised through a phishing email that appeared to come from a trusted business contact.
    • “The Indianapolis-based health system discovered the unauthorized access July 27, according to a Sept. 25 notice. A forensic investigation determined the unauthorized access began June 3 and continued until Eskenazi Health terminated it July 27.
    • “The incident began after the email account of one of Eskenazi Health’s business contacts was compromised and used to send thousands of unauthorized emails to individuals in the contact’s address book. An Eskenazi Health employee received one of the messages, which appeared to contain a secure document notification.
    • “After the employee interacted with the link and completed the requested authentication process, an unauthorized individual gained access to the employee’s work account, according to the notice.”
  • CISA added ten known exploited vulnerabilities (KVE) to its catalog this week.
    • September 21, 2026
      • CVE-2026-7273 Zyxel GS1900 Series Switches Stack-Based Buffer Overflow Vulnerability
        • Aviatrix discusses this KVE here.
    • September 22, 2026
      • CVE-2026-85102 Check Point Multiple Products Improper Certificate Validation Vulnerability
      • CVE-2026-93616 Check Point Multiple Products Path Traversal Vulnerability
      • CVE-2026-93952 Arista VeloCloud Orchestrator Improper Input Validation Vulnerability
      • CVE-2026-94127 F5 BIG-IP APM Heap-based Buffer Overflow Vulnerability
        • Cybersecurity News discusses the Check Point KVEs here.
        • Bleeping Computer discusses the Arista KVE here.
        • SOC Prime discusses the F5 KVE here.
    • September 24, 2026
      • CVE-2026-5430 WSO2 Multiple Products Path Traversal Vulnerability
      • CVE-2026-71362 Adobe Commerce and Magento Incorrect Authorization Vulnerability
        • Cybersecurity News discusses the WS02 vulnerabilities here.
        • Recent Breaches discusses the Abode and Magento KVE here.
    • September 25, 2026
      • CVE-2026-65660 Microsoft SharePoint Code Injection Vulnerability
      • CVE-2026-67279 Mikrotik RouterOS Improper Enforcement of Behavioral Workflow Vulnerability
        • The Hacker News discusses the Microsoft KVE here.
        • Recent Breaches discusses the Mikrotik KVE here.
    • September 25, 2026
      • CVE-2026-87902 WordPress Core Remote File Inclusion Vulnerability
        • Recent Breaches discusses the WordPress KVE here.

From the ransomware front,

  • HIPAA Journal reports,
    • “A new analysis of ransomware activity reveals broad, consistent targeting pressure across the United States. Ransomware activity is not limited to any specific industry, with all sectors attacked to varying degrees. The analysis was conducted by the AI-driven cybersecurity and threat intelligence platform provider Anomali, with the findings published in its US Ransomware Industry Targeting Report.
    • “Anomali observed ransomware targeting across 8 industry sectors by 200 distinct ransomware entities, with its analysis showing that technology was the most targeted sector, followed by manufacturing and healthcare.
    • “Anomali looked at ransomware targeting across eight industry sectors – technology, manufacturing, healthcare, financial services, government public services, construction, education, and energy. There was in excess of 50% observed targeting presence in all eight sectors, with technology companies targeted by 172 of the 200 ransomware entities (86%), followed by manufacturing with 166 (83%), and healthcare in third place with 154 (77%).”
  • Infosecurity Magazine relates,
    • “A newly formed ransomware group has claimed that if its victims don’t give into their extortion demands and pay a ransom, that they will destroy their backup infrastructure, in a move which could prevent a targeted organization from operating entirely.
    • “Named n0n, the emergence of the ransomware crew has been detailed by cybersecurity researchers at CyberXTron. In a blog post published on September 23, researchers said activity by n0n was first spotted on September 18 and by September 22 the group’s Tor-hosted leak site had published information about over a dozen victims.
    • “The group operates on a double extortion model which has become highly popular and highly effective among ransomware threat groups.”
  • Kaspersky adds,
    • “Kaspersky’s Global Emergency Response Team (GERT) has published a new report analyzing a sophisticated new tactic in the Payload ransomware family. Discovered during an incident response at a manufacturing company in the Middle East, this attack demonstrates a major shift in cybercrime: the attackers took complete control of the company’s network and forced its computers to lock up, display ransom notes, and change desktop wallpapers – all without deploying a conventional ransomware encryptor.
    • “This incident illustrates one of the trends mentioned in Kaspersky’s State of Ransomware 2026 reportreleased earlier this year: attackers are increasingly moving away from traditional file encryption. Instead, they are adopting “encryptionless extortion” – focusing on immediate operational disruption and leaking sensitive, stolen data on the dark web rather than relying on cryptographic keys to squeeze payments out of victims.”
  • Bleeping Computer notes,
    • “The Clop ransomware gang has moved its data leak site to a new Tor address after confirming its previous server was compromised and defaced through an unpatched Grav CMS flaw that BleepingComputer has learned is an unauthenticated path traversal vulnerability.
    • “The Clop leak site was breached earlier this month by the ShinyHunters extortion gang, which first uploaded a small text file and later replaced the site with a full-page defacement displaying its Umbreon Pokémon logo and a link to its own data leak site.”

From the cybersecurity business and defenses front,

  • The American Hospital Association News reports,
    • “The FBI and the Cybersecurity and Infrastructure Security Agency have released a fact sheet for critical infrastructure organizations on ways to reduce risk and minimize vulnerabilities when working with third-party hardware and software networks designed to monitor and automate physical processes for control systems and devices, such as pumps, sensors and industrial computers for operating essential equipment. In healthcare, such applications are common throughout facilities and include climate control, building automation, access control and other systems. Such operational technology systems are essential for maintaining clinical operations. The agencies said that organizations should maintain caution when granting third-party networks high levels of access or control over such operations, allowing only the minimum access necessary to perform their assigned tasks. Granting additional access could expose owners and operators to malicious cyber actors attempting to exploit and compromise equipment and critical functions. The fact sheet includes recommendations for organizations to assess and reduce risk of attacks.”
  • Cybersecurity Dive relates,
    • “Google-owned cloud security firm Wiz said on Thursday that it is using AI tools to identify vulnerabilities in internet-facing critical infrastructure, from operational technology maintained by under-resourced utilities to software packages that are foundational to online activity.
    • “Where authorized, we will use the Wiz Red Agent and additional internal AI research capabilities to examine publicly facing websites, APIs, and applications,” Wiz’s Ami Luttwak and Gal Nagli wrote in a blog post about the company’s Scan for Good initiative. “This work will help organizations find and fix critical exposures before attackers do, allowing them to stay ahead of adversaries as AI capabilities advance.”
  • and
    • “Nearly nine out of 10 industrial security leaders said they believe their companies could contain a cyber incident, and nearly half of those same companies experienced a breach or attack over the past 12 months, according to a report released Tuesday by Rockwell Automation. 
    • “More than one-third of industrial firms described cyber risk as the top obstacle to growth. 
    • The report highlights a continued resilience gap in industrial environments, where maintaining operational technology is critical. More than 60% of industrial firms have invested in various security technologies, including asset inventory, intruder detection and secure remote access.” * * *
    • “A separate benchmark report out Tuesday from Honeywell Technologies also showed a significant gap in OT security readiness. The report, based on responses from more than 600 IT security leaders globally, showed only one in five organizations had complete visibility into their OT assets.” 
  • and
    • “As the cyber insurance industry has worked to regain momentum against a rising wave of cyber risk, the rapid emergence of AI has put increased pressure on determining whether the sector could afford to cover potentially billions in losses from a catastrophic event. 
    • “After months of uncertainty, Beazley, a leading specialist in the cyber sector, on Thursday confirmed it would provide “AI-afffirmative cover,” meaning it would cover losses stemming from an incident, even if the attacker utilized artificial intelligence.” 
  • Help Net Security notes,
    • “To help security practitioners catch malware that leans on AI, researchers from Cisco Talos shared an open-source framework that they hope will be used to classify and analyze the threat. The tool, called CAIRN, works entirely from metadata pulled off files. No downloading the malware, no running it.”
  • Dark Reading explains that “Stopping IT Worker Scams Requires Revamped HR Process.”
    • “Training human-resource managers in the latest tactics and warning signs goes a long way toward blunting the threat, but automated analysis can help even more.”
  • Here is a link to Dark Reading’s CISO Corner.

Cybersecurity Saturday

From the frontier AI front,

  • The Wall Street Journal reports,
    • “Google’s Gemini model accessed the internet and hacked other companies during a test of its cybersecurity capabilities, the first known example of the company’s artificial-intelligence systems autonomously committing such an act. 
    • “The hacks, which the company confirmed on Friday [September 18], occurred in May as part of a test run by the company Irregular, which was also involved in similar incidents disclosed by OpenAI, Anthropic and Meta. 
    • “In one of the cases, the model guessed passwords until it gained access to a protected system. In the other two cases, the model found credentials in a public repository that allowed it to then access protected systems. In each case, the model ended the intrusion after determining it had accessed a real company’s systems, Google said.
    • “Irregular notified Google about the hacks at the end of July, Google and Irregular said, in the wake of the discovery that OpenAI’s agents had hacked the AI software company Hugging Face. Google didn’t disclose the hacks until The Wall Street Journal reached out with inquiries this week.” * * *
    • “Worries about the cybersecurity capabilities of new models have increased since the July discovery of the Hugging Face hack. In that case, up to 1,200 agents coordinated on a secret message board inside OpenAI to try to cheat on an evaluation, a report by the third-party testing company METR revealed in August. 
    • “Last week, those concerns spilled into the mainstream after the dramatic quitting of Jacob Coxon, a former OpenAI researcher who had gone to Anthropic earlier this year. Over the weekend, leaders from Anthropic, OpenAI, Google and SpaceX all agreed on the need to slow down the rate of AI progress, although none of the companies have outlined exactly how that would happen.”
  • and
    • “The WSJ Technology Council Summit kicked off Monday afternoon [September 14] in New York City with an informal poll of the audience during a town hall conversation. In a show of hands, only a few people said they feared that AI could kill us all in the next decade, while about half of attendees indicated that they were in support of slowing down AI development at the frontier and prioritizing safety guardrails.
    • “But that slowdown didn’t apply to the deployment of AI within their organizations, where not all models are at the cutting edge and even the most advanced of them tend to be relatively well understood and tested by experience.
      “It’s in our hands and it’s up to us to apply [AI] for good, and I think it can do a lot of good for society,” said Vishal Talwar, president, FedEx Dataworks, and chief digital and information officer, FedEx.
      “Much of ensuing town hall discussion focused on the myriad ways in which companies were operationalizing AI.”
  • Cyberscoop adds,
    • “The AI hacking apocalypse is not inevitable.
      • “While large language models present real risks to society, experts say they can be tested and largely controlled using well-worn cybersecurity and policy choices.”
      • “Juan Andres Guerrero-Saade, a fellow for AI and security research at SentinelOne and an adjunct professor at Johns Hopkins University, said the hacks are worth taking seriously, but at a time when businesses and open-source maintainers should be focused on further hardening their systems and policymakers should be discussing new solutions, “what we see is cybersecurity being used essentially as an excuse for these AI doomer arguments.” * * *
      • “Guerrero-Saade is among a growing chorus of cybersecurity professionals who say that while AI systems pose real, unique threats to our systems, the apocalypse is far from inevitable. Most of the public concerns around the incidents, let alone worries about killer AIs attacking critical infrastructure, assuming control of the internet and wiping out humanity, are either technically impossible or can largely be controlled through established cybersecurity principles.
      • “There is this “narrative or magical thinking of ‘Well, AI is going to be able to hack everything, and therefore it can control everything, and therefore it’s going to kill us all,’” he told CyberScoop. “And you [think] these just don’t add up. They’re not very well-reasoned arguments.”
      • “This fatalistic narrative tied to AI’s eventual dominance doesn’t hold up under scrutiny, according to experts CyberScoop spoke with. In recent conversations, cybersecurity and national security professionals raised questions about both the technical solutions OpenAI and Anthropic use to contain their models, as well as the glaring absence of federal oversight from federal regulators or truly independent third-party review.”

From the cybersecurity policy and law enforcement front.

  • Per a Senate Finance Committee news release,
    • “U.S. Sens. Mark R. Warner (D-VA) and Ron Wyden (D-OR) today reintroduced the Health Infrastructure Security and Accountability Act, legislation to improve cybersecurity in our health care system amid a growing wave of cyberattacks that are compromising Americans’ sensitive information and disrupting access to critical care across the country.” * * *
    • “Specifically, the Health Infrastructure Security and Accountability Act would require the Department of Health and Human Services (HHS) to establish, enforce, and regularly update strong minimum cybersecurity standards for health care providers, health plans, clearinghouses, and business associates, with heightened standards for systemically important entities and entities critical to national security.
    • “The legislation would also require covered entities to develop continuity plans describing how it would resolve a tech failure or intrusion, conduct annual cybersecurity tests, and undergo independent security audits, while increasing fines for failure to meet security requirements and strengthening HHS oversight through annual cybersecurity audits. Additionally, this legislation would provide $1.3 billion to help hospitals strengthen their cybersecurity, including $800 million for hospitals in rural and underserved urban communities.
    • “Full text of the bill can be found here. A summary of the bill can be found here.”
  • Cybersecurity Dive reports,
    • “The Cybersecurity and Infrastructure Security Agency (CISA) will stop publishing weekly roundups of newly disclosed software vulnerabilities at the end of September, the agency announced on Thursday.
    • “CISA is ending its Vulnerability Bulletin “as part of its shift from severity‑based vulnerability management to a modern, risk‑based approach,” the agency said in a statement.
    • “The weekly bulletins, published since early 2004, listed vulnerabilities published during the reporting period along with their CVEs, severity scores and brief descriptions.” * * *
    • “CISA said in its Thursday statement that sunsetting the bulletin aligns with the prioritization directive it issued in July, “which directs federal agencies to prioritize vulnerabilities based on real‑world risk factors, including evidence of exploitation and exposure, rather than severity scores alone.”
    • “As it discourages organizations from relying solely on Common Vulnerability Scoring System (CVSS) scores to decide which vulnerabilities to fix, CISA has also been highlighting the Stakeholder-Specific Vulnerability Categorization (SSVC) system as a more nuanced approach to vulnerability analysis.
    • “Chris Butera, CISA’s acting executive assistant director for cybersecurity, said on Wednesday at Google’s Cyber Defense Summit that the agency has been discussing SSVC with companies that sell vulnerability management software. “They’re building some of this prioritization into their vulnerability tooling,” Butera said.”
  • and
    • “The Cybersecurity and Infrastructure Security Agency (CISA) wants to hire critical infrastructure experts with broad, rather than specialized, knowledge as it tries to help defend the infrastructure community with limited resources.
    • “I need to be able to hire people that are highly adaptive, because I think the threat is continuing to evolve so much, and the exposure that we have within these critical infrastructure sectors is evolving so much,” acting CISA Director Nick Andersen told reporters after speaking at Google’s Cyber Defense Summit here on Wednesday [September 16]. “I need people that can pivot from day to day to be able to help meet all of these stakeholders where they are.”
    • “Andersen’s comments come as CISA prepares to onboard roughly 250 new employees as part of a hiring sprint meant to fill critical vacanciescreated by the Trump administration’s sweeping downsizing of the agency over the past two years. As ransomware gangs and nation-state hacker groups increasingly menace infrastructure operators, in some cases aided by destabilizing advances in AI, CISA’s supporters say its mission — and its partnerships — have become more important than ever.”
  • Per a Department of Health and Human Services news release,
    • “The U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) today [September announced a settlement with Ambry Genetics Corporation (Ambry) concerning potential violations of the Health Insurance Portability and Accountability Act of 1996 (HIPAA) Security Rule. Ambry, headquartered in Aliso Viejo, California, is a covered entity that provides genetic testing and clinical genomics services.
    • “In January of 2020, Ambry discovered that an employee’s email account was compromised by a phishing attack. The protected health information (PHI) of 225,370 individuals was potentially exfiltrated by the threat actor. Affected PHI included names, addresses, dates of birth, some Social Security numbers or driver’s license numbers, financial information, diagnoses and conditions, lab results, medications, and treatment information.” * * *
    • “The settlement resolves an investigation that OCR initiated after Ambry filed a breach report in March 2020 about the phishing incident that occurred in January 2020.  OCR found that Ambry had potentially violated provisions of the Security Rule, including:
      • “Failing to conduct an accurate and thorough risk analysis of the potential risks and vulnerabilities to the electronic protected health information (ePHI) held by Ambry;
      • “Failing to implement procedures for terminating access to ePHI when the employment of or other arrangement with a workforce member ends or access is no longer appropriate; and
      • “Failing to assign a unique name and/or number for identifying and tracking user identity in electronic systems containing ePHI.” * * *
  • “The resolution agreement and corrective action plan may be found at https://www.hhs.gov/sites/default/files/ocr-ra-cap-ambry-genetics-corporation.pdf [PDF, 51.88 MB].”
  • Cyberscoop adds,
    • “Another core member of the hacker subset of The Com involved in a spree of extortion attacks from at least 2021 to 2023 pleaded guilty to federal charges, according to court records released Tuesday.
    • “Ahmed Hossam Eldin Elbadawy, a 24-year-old from Texas, pleaded guilty exactly one year ago to wire fraud conspiracy and aggravated identity theft. His guilty plea wasn’t shared publicly until prosecutors filed an order of forfeiture this week seeking proceeds from Elbadawy’s criminal activities. 
    • “Elbadawy and his co-conspirators — Noah Michael Urban, a Florida man sentenced to 10 years in prison last year, and Tyler Robert Buchanan, a Scottish man who pleaded guilty to multiple cybercrimes in April and awaits sentencing — were part of an aggressive subset of The Com coined Scattered Spider.”
  • and
    • “Authorities seized the primary domain and other websites linked to NightmareStresser, one of the longest-running and most popular distributed denial-of-service operations used by cybercriminals globally, the Justice Department said Tuesday. 
    • “Cybercriminals of various motivations used the DDoS-for-hire service to launch hundreds of thousands of DDoS attacks or attempted attacks since at least 2022, officials said. 
    • “The takedown, part of an ongoing globally coordinated effort dubbed “Operation PowerOFF,” marks law enforcement’s continued targeting of IP stressers or DDoS booters that inundate websites, servers and networks with junk traffic, rendering legitimate sites inaccessible. The seizures were executed by the FBI Anchorage field office and the Royal Canadian Mounted Police.”

From the cybersecurity vulnerabilities and breaches front

  • HIPAA Journal notes,
    • “A hacking group has claimed responsibility for an August 2026 cyberattack on Cedar County Memorial Hospital in Missouri. Hacking-related data breaches have been reported by Next Level Medical in Texas and Grafton City Hospital in West Virginia.”
  • MSSP Alert adds,
    • “Artificial intelligence is fundamentally altering the economics of cybercrime, making attacks faster and less expensive to execute, as first reported by Channel Insider. Ransomware victims saw a 45% increase in the first half of 2026, while the average underground price for initial access dropped by 69%, from $1,427 to $439. This shift indicates that AI is enabling threat actors to target more organizations with greater speed and scale, even if individual attacks are not necessarily more successful.”
  • Cyberscoop reports,
    • “Researchers said they used Anthropic’s Claude and OpenAI’s Codex to identify a damaging flaw embedded in a popular software decoding tool that could leave major internet platforms, enterprise services, and web frameworks vulnerable to data theft and remote access.
    • “The vulnerability, nicknamed HEIF Heist, refers to the malware’s ability to trigger memory corruption errors in affected software, allowing the attacker to pilfer sensitive data from its victims. In a report published Thursday, the researchers laid out the potential damage an attacker could cause, including gaining access to internal OpenAI repositories, leaking user files, access tokens, and other sensitive data for online services like Amazon Web Services, and gaining remote code execution privileges across a range of online services, including Meta’s core product suite, GitHub Enterprise servers and open-source internet forum Discourse.”
  • and
    • “North Korean hackers are infiltrating tens of thousands of job seekers’ computer networks by posing as prospective employers, such as artificial intelligence firms, to steal sensitive information and millions of dollars worth of cryptocurrency, U.S. and allied governments warned Friday.
    • The security agencies behind the alert, attributed the group, known as WaterPlum or Contagious Interview, as operating under the 313 General Bureau of the Munitions Industry Department subordinate to the Central Committee of the Workers Party of Korea. The efforts dovetail with those of North Korean IT workers.
    • “WaterPlum actors pose as prospective employers to target software developers and IT professionals worldwide under the pretext of attractive job opportunities,” the agencies wrote. “They often impersonate legitimate Artificial Intelligence (AI), cryptocurrency, or Non-Fungible Token (NFT) companies and have also used recruiting services.”
    • Additionally, “Some WaterPlum actors also operate as North Korean IT workers performing web system design and development tasks on corporate web systems for clients,” read the alert from agencies in Japan, Australia and Germany, alongside the FBI and the Department of Defense’s Cyber Crime Center.”
  • Help Net Security tells us,
    • “A fake ChatGPT billing email is steering users to a copy of the OpenAI login page that keeps whatever username and password they type. Josh Varden of Cofense’s Phishing Defense Center traced the email’s payment button through a Google redirect to the attacker’s page.
    • “The lure targets ChatGPT users on work and personal accounts alike, and it copies the kind of bill a subscriber already expects. Credentials entered on the fake page go to the attacker, and the victim is sent on to an error page.” * * *
    • “Cofense listed three indicators: the Google redirect link and two paths on the same nxcli[.]io host, login.php and key.php. Mail teams can search their logs for all three. If you use ChatGPT, the check that matters takes two seconds: read the address bar and confirm it says auth.openai.com before you type a password.”

From the ransomware front,

  • Industrial Cyber informs us,
    • “New data from Comparitech disclosed a record 997 ransomware attacks worldwide in August 2026, averaging 32 attacks per day and representing a 23% increase from 809 attacks in July. The total surpassed the previous monthly record of 988 attacks recorded in February 2025. Businesses accounted for 861 attacks, up 24% from July, while ransomware incidents targeting healthcare providers rose 30% to 69. Utility companies recorded the sharpest sector increase, with attacks doubling from five in July to 10 in August. 
    • “Ransomware surge was led by Qilin and The Gentlemen, which together accounted for more than 26% of August’s attacks, with Qilin claiming 157 incidents and The Gentlemen 107. Qilin’s attack claims increased 22% during the month, while The Gentlemen’s declined 21%; Qilin also had 12 confirmed attacks, compared with eight for The Gentlemen.” * * *
    • “Attacks on healthcare providers increased by 30% from July 2026 to August 2026, rising from 53 to 69. Eight attacks were confirmed in August. Three of the confirmed attacks took place in the U.S. Nutex Health Inc. noted unauthorized activity on its systems in a SEC filing on Aug. 24, 2026, and The Gentlemen claimed the attack. Cedar County Memorial Hospital experienced disruption to its IT networks on the afternoon of Aug. 14, 2026, with operations returning to normal on the morning of Aug. 28. Wallstreet claimed the attack. At Windrose Health Network, hackers exploited a vulnerability in the network’s remote-management tool in early August, resulting in a data breach. Storm claimed the attack.” 
  • Beckers Health IT reports,
    • “Jackson-based University of Mississippi Medical Center did not pay a ransom in connection with the cyberattack that disrupted its systems in February, according to officials.
    • “UMMC Vice Chancellor of Health Affairs LouAnn Woodward, MD, told SuperTalk Mississippi the state did not compensate hackers following the Feb. 19 attack. State Sen. Nicole Akins Boyd, who chairs the Universities and Colleges Committee, corroborated Dr. Woodward’s account.
    • “The statements come after State Auditor Shad White said his office would investigate the incident and notify the public if the government had paid a ransom.
    • “The cyberattack knocked out UMMC’s phones, website, records database and IT systems, forcing partner clinics to close for nine days and staff to record patient information by hand. The medical center returned to full operations Feb. 27.”
  • Cybersecurity Dive relates,
    • “Security researchers warn that a newly discovered ransomware variant called Settra has targeted virtual private network environments or compromised credentials for initial access before deploying remote monitoring and management tools to gain persistent access in targeted environments. 
    • “Researchers from Huntress observed two specific attacks in recent months, including a July incident at a consumer services and retail organization and a September incident at a manufacturing firm, according to a blog post published Thursday [September 17].
    • “The attackers could be described as capable rather than sophisticated,” said Lindsey O’Donnell-Welch, principal technical community engagement writer at Huntress. “They used effective, established ransomware tradecraft: MeshAgent for persistence, a vulnerable driver to potentially impair defenses, log clearing and recovery tampering.”
    • “Researchers from MoxFive said Settra used compromised VPN credentials to gain initial access and posted numerous victim organizations on its shaming site. The group claims to target organizations with exploitable weaknesses, such as unpatched systems or weak access management, according to a blog post from MoxFive.”
  • Bleeping Computer lets us know,
    • “The ShinyHunters extortion gang breached the Clop (aka Cl0p) ransomware operation’s data leak site, defacing the Tor site and allegedly stealing server data and the private keys for its onion service.
    • “The attack began Friday night [September 18] when ShinyHunters exploited what they claim is an unauthenticated file upload vulnerability in Grav CMS, which they used to upload a small text file to Clop’s site.
    • “The small text file contained a message from the threat actors to the Clop ransomware gang, warning not to threaten them and including a link to ShinyHunter’s own data leak site.”
  • InfoSecurity Mag tells us,
    • “It is a scenario that every CISO hopes they never face: the network encrypted by ransomware attack and cybercriminals who claim to have stolen sensitive data which they will leak if they don’t receive a ransom payment.
    • “Unfortunately for Zach Lewis, CISO at the University of Health Science and Pharmacy (UHSP) in St. Louis, this was the reality he faced when the organization was hit by a LockBit ransomware attack in summer 2023. The University recovered without paying the ransom, but it was a challenging time for all involved.
    • “In a conversation with Infosecurity, Lewis opened up about how it felt to be the victim of a ransomware attack and the toll it took on his team, as well as how the organization recovered from the incident and the lessons other cybersecurity leaders can learn from this experience.”

From the cybersecurity business and defenses front

  • The Wall Street Journal reports,
    • “Companies are facing a new era in cyberattacks driven by AI. But according to one cybersecurity CEO, having the right technology for defense isn’t necessarily the problem. It’s the humans who need to step up—particularly CEOs.
    • “What we’ve seen practically from working with some of the largest organizations in the world is that the technology is already there,” Galina Antova, CEO of the AI-driven security platform Kai, said at the Leadership Institute’s WSJ Technology Council Summit this week. “We could implement so many improvements,” using autonomous AI, she added.
    • “But what it really comes down to is having “the right incentive for the leaders to pursue that,” and “are they enabling their security organization to really move at machine speed?” 
    • “Companies need courage and leadership, she told enterprise tech bureau chief Steve Rosenbush, in a discussion that included Oege de Moor, founder and CEO of cybersecurity firm XBOW. 
    • Some additional insights from their conversation:
      • “Companies may need to redesign their security workflows. Attackers are “already moving at machine speed,” and they’re encountering a patchwork of protections, Antova reported. She has found that many Fortune 500 companies use some 80 to 120 security tools “that are organized in a very fragmented way,” she said. That means that when a company has an exposure, it can take time—days, weeks, or months—to find and close it. By contrast, she said, an end-to-end autonomous defense system that’s supervised by humans can reduce that time to minutes.” * * *
      • “[B]oth CEOs noted that the gap between frontier and open models was shrinking—and Antova added that with the right cybersecurity expertise and a surgical approach to deployment, the cost of AI-enabled security no longer needs to be prohibitive.”
  • Cybersecurity Dive adds,
    • “Artificial intelligence is now the leading driver behind new investment into cybersecurity budgets, according to a report released Tuesday from IANS and Artico Search.  
    • “About seven of every 10 chief information security officers surveyed said AI was their top priority for new cybersecurity spending. Two specific areas for AI-related spending shown in the report include automating security operations and enhancing identity and access management. 
    • “Overall security spending rose 5% in the current survey, which is barely ahead of the 4% spending increase in the year-ago report. AI spending priorities come at a time of relatively modest growth in overall security spending.”
  • Per CISA news releases,
    • “The Cybersecurity and Infrastructure Security Agency (CISA) hosted Cyber Storm X this week, a four-day national cybersecurity exercise designed to test and ultimately strengthen the nation’s resilience. This year’s exercise included 2,000 participants from across the public and private sectors and marks the tenth exercise in the 20-year history of Cyber Storm. The biennial exercise brings together the people who manage the services our nation relies on, including water, energy, and other vital sectors. During the exercise, participants practice how they would respond to a major cyber incident affecting critical infrastructure.
    • “Cyber Storm helps critical infrastructure owners and operators understand how we would manage a large-scale cyber incident,” said Acting CISA Director Nick Andersen.  “Exercises strengthen our national resilience by making sure our plans, policies, and partnerships are ready when we need them.  As a nation, we need the ability to respond swiftly and effectively to critical threats. That’s exactly what Cyber Storm does and why it’s a vital exercise for our nation’s security.”
    • “This year’s exercise focused on a scenario involving a nation-state adversary targeting the transportation systems sector, including rail and ports, along with the water and wastewater systems sector. The exercise allowed participants to test response plans, practice coordination, and strengthen information sharing in a safe environment. Cyber Storm X included over two hundred organizations across all levels of government and the private sector.
    • “CISA will now collaborate with participating organizations to identify lessons learned from the exercise. We will use these findings in a public after-action report that captures observations, analyses, and recommendations. CISA is committed to providing access to a wide range of cybersecurity tools and training opportunities, with exercises being a critical part of that toolkit to enhance our nation’s cyber preparedness.
    • “For more information, please visit Cyber Storm X: National Cyber Exercise.”
  • and
    • “Today [September 16], the Cybersecurity and Infrastructure Security Agency (CISA) released guidance that helps critical infrastructure owners and operators implement realistic decoy systems and information assets to quickly detect and disrupt malicious activity occurring in their networks, which will ultimately improve their cyber defenses. Using Cyber Decoys to Strengthen Detection and Response is the first guide from CISA that offers a detailed explanation of the defensive cyber decoy process.
    • “Many organizations struggle to detect adversaries who use legitimate credentials, native tools, and living off the land techniques to conduct discovery, move laterally, and access data. In this guide, CISA encourages critical infrastructure organizations to incorporate cyber decoy capabilities alongside existing Zero Trust models. Cyber decoy strategies operate on the expectation that malicious actors may eventually gain some level of access. By placing decoys within internal networks and systems, especially in high-value areas, organizations can enable defenders to:
      • “Detect adversaries operating within the environment early in the intrusion lifecycle;
      • “Gather and analyze information taken from intrusions and attempted intrusions;
      • “Allocate defensive resources more effectively based on observed adversary behaviors;
      • “Reduce mean time to detection (MTTD) by generating high-fidelity alerts.” * * *
    • “To effectively use this guide, cyber defenders should have a basic understanding of the MITRE ATT&CK ® Matrix and common enterprise security controls and tools. The guide provides a practical approach to designing and implementing decoy strategies by leveraging the MITRE ATT&CK® knowledge base and the MITRE Engage™ framework.
    • “For more information, please visit Cybersecurity Best Practices.”
  • and
    • “The Cybersecurity and Infrastructure Security Agency (CISA) and the National Institute of Standards and Technology (NIST) today [September 15] released Interagency Report (IR) 8587, Protecting Tokens and Assertions from Forgery, Theft, and Misuse: Implementation Recommendations for Agencies and Cloud Service Providers (CSPs). The report guides federal agencies and CSPs in defending the identity tokens and assertions that underpin modern single sign-on (SSO), federation, and application programming interface (API)-based access, systems adversaries increasingly target to move laterally through enterprise networks and reach sensitive data.
    • “The final report incorporates key feedback from nearly 250 public comments on token validation, secrets management, and detection at scale. The report also reflects input from CISA’s long-term, strategic collaboration with industry CSPs and interagency partners through the Joint Cyber Defense Collaborative. CISA and NIST engagements with this group included a technical exchange in June 2025 with over 50 industry experts to identify approaches to harden identity infrastructure and a webinar in January 2026 to review the draft report. Dozens of individual meetings with CSPs were also held to discuss feedback that included Google, HashiCorp, an IBM Company, IBM, Microsoft Corporation, Okta Inc., the OpenID Foundation, Oracle America, Inc., Amazon Web Services, and Wiz.” * * *
    • “The recommendations in the final report apply across commercial and government-operated cloud services and support implementation of Executive Order 14306 on secure software development practices.
    • “CISA urges federal agencies, CSPs and cloud consumers to review and implement IR 8587 to improve the security of their cloud systems. 
    • “For more information on this effort, read NIST’s News Release.“
  • Tech Target offers a tip about “how to verify the value of AI-powered business analytics.”
    • Executives can separate AI analytics capabilities from marketing hype by taking steps to confirm the platform improves decision-making and gives results that hold up.
  • Here is a link to Dark Reading’s CISO Corner.

Cybersecurity Saturday

From the frontier AI / Project Glasswing front

  • Daniel Borish writes in LinkedIn,
    • “Anthropic released its fourth threat intelligence report on September 10, 2026, covering activity its Threat Intelligence team disrupted between December 2025 and August 2026. The report documents cases across seven categories of harm: cyber operations, surveillance, influence operations, conventional weapons development, biological misuse, scams and fraud, and illicit distillation. The company assigns each disrupted actor an internal designator, a Generative Threat Group (GTG) number, and publishes case studies detailing how each group used Claude models, along with indicators of compromise for other defenders to act on.
    • “The report’s central claim is not that AI created new categories of attack. Credential theft, phishing, SQL injection, and unpatched edge devices remain the entry points they have always been. What changed is who can run these attacks at what speed. Anthropic’s investigators found a suspected Russian state espionage unit, a network of financially motivated ShinyHunters affiliates, Chinese university students moonlighting in exploit research, and a lone French hacktivist all using functionally similar AI-orchestrated methodologies to run multi-victim campaigns that would previously have required coordinated teams.”
  • The Wall Street Journal reports,
    • “Artificial intelligence agents being tested by OpenAI launched a cyberattack against a popular software service two months before they hacked the AI software company Hugging Face, a new signal of the potential for advanced AI tools to slip out of human control.
    • “The attack overwhelmed maintainers of an online service for coders, called RubyGems, and forced them to shut down new account registrations as they dealt with the chaos it had caused, operators of the service said.
    • “A coalition of AI researchers said it had unearthed evidence that OpenAI agents were behind the May attack and shared its findings with The Wall Street Journal and OpenAI. The AI developer on Friday confirmed that its agents had been involved in an incident involving RubyGems.
    • “Based on our review, our agents used the RubyGems platform to access the internet to carry out benign tasks and retrieve public information. We’ll continue to investigate as part of our broader review of agent activity during training and evaluation,” an OpenAI spokeswoman said in a statement.”
  • and
    • “An Anthropic researcher is quitting the artificial-intelligence industry over fears that the lab and its competitors are racing to build systems they won’t be able to control, a sign of mounting safety concerns within top AI companies.
    • “Jacob Coxon, a researcher who specializes in training new AI models by having them consume vast amounts of data, said Tuesday that he is leaving the company because he doesn’t want to participate in an industrywide rush to build AI systems that can improve themselves, worried such systems could spiral out of control and destroy humanity.
    • “The 27-year old Brit, who previously studied mathematics, said many of his industry colleagues now use phrases like “crunchtime” and “endgame” to describe the trajectory toward self-improving models.” * * *
    • “Anthropic didn’t immediately comment on the departure. Chief Executive Dario Amodei and other company leaders have repeatedly warned about the risks of rogue AI models, and urged the industry to slow development. 
    • “After Coxon announced his departure, a top scientist at the company, Evan Hubinger, wrote on X that he thought Coxon was correct about the risks of AI development.
    • “We really do earnestly believe AI could kill all humans! I personally think it is >10% within the next decade,” Hubinger wrote. “I believe Anthropic is trying its best, but we do not yet have a plan to solve alignment for superintelligence and are not clearly on track to.” Others also amplified the view.”
  • Per Axios: “Nvidia CEO Jensen Huang: AI fears designed to generate cybersecurity business.”
  • BigGo Finance lets us know,
    • “A bipartisan group of US senators is negotiating legislation that would create a legal duty of care for frontier AI developers, requiring them to prevent catastrophic risks and giving the federal government authority to block unsafe model releases. The proposal, led by John Thune, Ted Cruz and Amy Klobuchar, would apply to advanced models from companies such as OpenAI, Anthropic and Google, with national laboratory experts potentially conducting hands-on testing for nuclear, biological and cyber threats. Companies could appeal government blocking decisions in federal court. The measure would also preempt state AI safety laws. With the House in session only one week before the November 3 midterms, passage remains uncertain despite growing pressure on Congress to address frontier AI risks.”
  • Axios adds,
    • “A letter is circulating among House members urging Speaker Mike Johnson (R-La.) to bring back the House “immediately” and keep it in session until Congress passes AI safeguards, Axios has learned.”
  • The Wall Street Journal notes,
    • “President Trump, who has taken a light touch overseeing the sector, previously said he is in favor of kill switches and other steps to keep AI safe but has warned burdensome regulation could cost the U.S. in the tech race.”
  • and
    • “The leaders of three of the biggest AI companies agreed [September 12] that they needed to slow development of the technology before their advances create a menace that can’t be controlled.
    • “It was a rare display of unity by Elon Musk, Sam Altman and Dario Amodei, who have been spending tens of billions of dollars to develop evermore powerful artificial intelligence models. Altman even suggested that his company, OpenAI, may need to delay its much-anticipated IPO to focus on safety.”

From the cybersecurity policy and law enforcement front,

  • Per GovCIO Media,
    • “Federal agencies are looking to deepen their partnership with the private sector to protect critical infrastructure, with joint efforts to identify vulnerabilities, deploy technology and scale solutions.
    • “National Cyber Director Sean Cairncross said Thursday [September 10] at the Billington Cybersecurity Summit in Washington that government and industry need to work “hand in glove” rather than rely on compliance checklists as technology increasingly shapes both critical infrastructure and the threats against it.
    • “We’re in a moment technologically where security and innovation have melded, and in order to move forward, protect critical infrastructure, make sure the systems that our citizens rely on for daily life are protected and secure, we need a relationship that is hand in glove, and that means we cannot be dictating a compliance checklist to industry,” said Cairncross.”
  • Federal News Network reports,
    • “The FBI released its first agency-wide, unclassified cyber strategy on Wednesday, with the goal of unifying efforts across the bureau’s 56 field offices to counter both nation-state threats and cyber criminals.
    • “The 17-page strategy details a four-pillar approach to countering cyber threats across the bureau. Brett Leatherman, assistant director of the FBI’s Cyber Division, said previous cyber strategies for the bureau have either been classified or focused on specific threats, like countering China.
    • “This is a comprehensive strategy that directs our teams, our field offices, our global presence, and how we are to align all our efforts to counter this work,” Leatherman told reporters after speaking at the Billington Cybersecurity Summit in Washington on Wednesday morning [September 9].”
  • and
    • “The CIA is pushing to bring more scientific and technical expertise into its workforce, with a top official touting a big year for hiring despite widespread cuts across the intelligence community over the past year.
    • “Michael Ellis, the deputy director of the CIA, said the spy agency is seeking to recruit more employees with backgrounds in science and technology. Ellis described a STEM background as not a prerequisite for intelligence in work in 2026, but “it sure helps make things easier.”
    • “When I think about, you know, where we want the CIA workforce to be five years from now, it’s an elite workforce,” Ellis said at the Billington Cybersecurity Summit in Washington on Tuesday. “It’s a nimble workforce. It’s one that has more technical background than it has today, and it’s one that is motivated by mission.”
  • Cybersecurity Dive adds,
    • “As the federal government scrambles to protect its own networks and support critical infrastructure operators, CISA is preparing to bring in roughly 250 new employees to rebuild core teams.
    • “We’re looking forward to welcoming hundreds of new CISA employees in the very near future,” acting CISA Director Nick Andersen told reporters after a talk at the Billington Cybersecurity Summit here on Wednesday.
    • “The employees have received tentative job offers and are “waiting to get that official start date,” Andersen said during his speech.”
  • Cyberscoop points out,
    • “The private sector still isn’t sharing enough cyber information with the FBI in part because organizations are operating on false assumptions about what the bureau will do with what it collects, the FBI’s top cyber official said Wednesday.
    • “Brett Leatherman, assistant director of the FBI’s cyber division, said in remarks at the Billington CyberSecurity Summit and in a discussion with reporters that organizations stand to benefit from bringing in the bureau when it’s compromised by hackers from the People’s Republic of China (PRC) and others. But one of the “key misconceptions” is that “the FBI is somehow sharing information with regulators for regulatory purposes, and that’s not the case.”
    • “From my standpoint over the last few years, I think we’ve seen a hesitancy on some companies to engage [with the] FBI,” Leatherman said.”
  • and
    • “The U.S. government is accusing Chinese AI companies of engaging in a deliberate and “systematic” effort to illegally distill U.S. frontier AI models and their capabilities. 
    • “According to a joint cybersecurity advisory from the National Security Agency, the Cybersecurity and Infrastructure Security Agency and the FBI, the sheer scale of these efforts since 2024 indicate that distillation is a critical part of China’s AI industrial policy.
    • “China-based artificial intelligence companies are conducting systematic extraction of proprietary functionalities and capabilities of U.S. AI companies’ models through industrial-scale knowledge distillation campaigns that form the core—not merely a supplement—of their AI development strategy,” the agencies wrote. 
    • “The advisory names Chinese companies like DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI, saying they spent billions of tokens across millions of exchanges and requests with frontier U.S. AI models like Anthropic’s Claude, OpenAI’s ChatGPT, Google Gemini, and xAI’s Grok, since at least late 2024.”
  • The Justice Department made available “Remarks by Deputy Assistant Attorney General Josh Goldfoot of the Justice Department’s Criminal Division at the International Symposium on Cybercrime Response” held in Seoul, Korea.
  • Beckers Health IT notes,
    • “A Ukrainian national who helped deploy Conti ransomware against more than 1,000 victims worldwide has been sentenced to four years in prison for conspiracy to commit wire fraud.
    • “Oleksii Oleksiyovych Lytvynenko, 44, formerly of Cork, Ireland, admitted to joining the Conti operation and coding a “loader” — malware used to deliver other malicious software onto compromised systems, according to a Sept. 10 U.S. Justice Department news release. He pleadedguilty June 10.
    • “Conti attacked computers and networks in 47 states, the District of Columbia, Puerto Rico and 31 countries between 2020 and 2022, and the FBI estimates the group collected more than $150 million in ransom payments. Evidence from Mr. Lytvynenko’s online accounts showed he possessed data stolen from eight U.S. victims and four overseas victims. He was arrested in County Cork, Ireland, in July 2023.”

From the cybersecurity breaches and vulnerabilities front,

  • HIPAA Journal released its June 2026 Healthcare Data Breach Report.
    • “In June 2026, 66 large healthcare data breaches – data breaches involving the protected health information of 500 or more individuals – were reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR) – a slight increase from the 64 data breaches reported in May. More than two large data breaches a day is the new normal. Over the past 12 months, an average of 65 large healthcare data breaches have been reported per day; eight years ago in 2018, large healthcare data breaches occurred at a rate of around one per day.”
  • Beckers Health IT reports,
    • “Houston-based Nutex Health says the hackers behind its August cyberattack have published the data they allegedly stole on their own website.
    • “The publicly traded micro-hospital operator is now downloading, processing and analyzing that data to determine its contents, scope and authenticity, according to a Sept. 10 SEC filing. Nutex said the review could take several weeks given the volume of data involved.” * * *
    • “Nutex said it has not identified any material impact on its business operations or financial reporting systems, and its materiality assessment from the Aug. 31 filing remains unchanged. The company said it continues to evaluate regulatory and legal notification requirements and intends to notify affected patients and employees.
    • “Several purported class action lawsuits have been filed against Nutex in the U.S. District Court for the Southern District of Texas’ Houston Division on behalf of individuals whose personal or health information was allegedly accessed. Nutex said it cannot predict the litigation’s outcome or its potential financial impact.”
  • and
    • “Annapolis, Md.-based Luminis Health’s phone system and MyChart patient portal remain unavailable as the health system continues responding to a cybersecurity incident involving an unauthorized criminal actor.
    • “In a Sept. 10 update, Luminis Health said its investigation is ongoing and teams are working with third-party experts to safely restore affected systems.
    • “The health system said its hospitals remain open and continue providing patient care.”
  • and
    • Recent cybersecurity warnings and incidents are highlighting risks for healthcare organizations that extend beyond ransomware, including cloud authorization abuse, voice phishing, brand impersonation, third-party access and publicly exposed information.
    • [The article describes] five recent cybersecurity developments Becker’s has reported on in September.]
  • Security Week adds,
    • “More than 4.1 million individuals had their personal, health, and insurance information stolen in a data breach at healthcare company AdaptHealth.
    • “Operating over 680 facilities across the US, AdaptHealth describes itself as a network of medical equipment companies that provides patients with healthcare solutions and medical equipment.
    • “The company was hacked in early June, when a threat actor gained access to its cloud-based applications, including internal systems used for patient management and document storage.
    • “After the attacker contacted the company, it confirmed the data breach, including the theft of a password file associated with insurance billing.
    • “The hacker used social engineering to compromise a user session at a third-party contractor, AdaptHealth said.”
  • and
    • “Future phishing campaigns may no longer involve a detectable physical web page.
    • “Barracuda has analyzed a new type of phishing campaign that adds both stealth and flexibility to traditional phishing. Rather than standard social engineering to persuade a target to visit a static compromised web page, this campaign generates a blob URL to render and deliver the phishing page inside the target’s own browser. This reduces the possibility of security scanners detecting either the social engineering email or the static residence of the phishing page.”
  • HIPAA Journal lets us know,
    • “Three high-severity vulnerabilities have been identified in NextGen Healthcare Mirth Connect (Mirth Connect), a cross-platform healthcare integration engine for connecting, routing, transforming, and exchanging clinical and administrative data between different healthcare systems. The vulnerabilities are due to improper neutralization of special elements used in SQL commands and improper restriction of XML External Entity Reference. Successful exploitation of the vulnerabilities could allow denial-of-service attacks and data exfiltration.
    • “The vulnerabilities were identified by security researcher Abhinav Agarwal using autonomous agents running his published methodology on AI-assisted vulnerability discovery. “Mirth Connect is effectively a switchboard between healthcare systems. It can sit between lab systems, imaging systems, databases, and clinical applications, so a vulnerability in the integration layer can expose much more than one isolated application,” Agarwal told The HIPAA Journal. A potential problem is that healthcare organizations may not know that they have a vulnerable component in one of their products. “A hospital may not see the name Mirth anywhere on the product it bought. Integration software can be managed, resold, or embedded inside another product, which is why SBOMs and exact version disclosure matter after vulnerabilities like these,” explained Agarwal.”
  • CISA added 14 known exploited vulnerabilities to its catalog this week.
    • September 8, 2026
      • CVE-2026-75650 Adobe Commerce and Magento Improper Neutralization of Special Elements Used in a Template Engine Vulnerability
      • CVE-2026-81963 Microsoft Windows Link Following Vulnerability  
      • CVE-2026-85880 Microsoft Windows Heap-Based Buffer Overflow Vulnerability 
      • CVE-2026-86218 N-able N-central Static Code Injection Vulnerability
        • SOC Prime discusses the Adobe KVE here.
        • The Hacker News discusses the Microsoft KVEs here.
        • Cybersecurity Dive discusses the N-able KVE here. 
    • September 9, 2026
      • CVE-2025-25249 Fortinet Multiple Products Heap-based Buffer Overflow Vulnerability
      • CVE-2026-19490 Citrix NetScaler Authentication Bypass Using an Alternate Path or Channel Vulnerability
      • CVE-2026-87491 Google Chromium V8 Out of Bounds Write Vulnerability
      • CVE-2026-20079 Cisco Firewall Management Center Authentication Bypass Using an Alternate Path or Channel Vulnerability 
        • Security Week discusses the Fortinet KVE here.
        • Cybersecurity News discusses the Citrix KVE here.
        • SOC Prime discusses the Google KVE here.
        • The Cybersecurity Hub discusses the Cisco KVE here.
    • September 10, 2026
      • CVE-2026-67277 MikroTik RouterOS Missing Authentication for Critical Function Vulnerability
      • CVE-2026-86060 MikroTik RouterOS Improper Neutralization of Argument Delimiters in a Command Vulnerability
        • Bleeping Computer discusses these KVEs here.
    • September 11, 2026 (1)
      • CVE-2026-42016 JFrog Artifactory Incorrect Authorization Vulnerability 
      • CVE-2026-42018 JFrog Artifactory Improper Authentication Vulnerability 
      • CVE-2026-84869 ConnectWise ScreenConnect Improper Privilege Management and Missing Authorization Vulnerability
        • The Hacker News discusses the JFrog KVEs here.
        • Security Arsenal discusses the ConnectWise KVE here.
    • September 11, 2026 (2)
      • CVE-2026-85706. GitLab Community Edition and Enterprise Edition Path Traversal Vulnerability
        • Cyberscoop discusses this KVE here.
  • Dark Reading adds,
    • “A new analysis of public data from Anthropic’s Project Glasswing has highlighted a significant gap between the number of vulnerability findings generated by its Claude frontier model and those that ultimately prove to be real, serious, and worth fixing.
    • “The distinction matters because it suggests that the bottleneck in vulnerability research may increasingly lie in validating new flaws and coordinating their remediation rather than in discovering them.”
  • Security Week tells us,
    • “Anthropic disrupted a cyberespionage operation whose tradecraft and targeting match the Russian state-nexus group tracked as Midnight Blizzard, the company said in a threat intelligence report published this week. 
    • “The report covers activity the company identified and shut down between December 2025 and August 2026.
    • “According to Anthropic, Midnight Blizzard used Claude to monitor how well its malware evaded detection by security products. When a tool was flagged, AI agents automatically modified and rebuilt it, then redeployed it, repeating the process until the malware went undetected again.”

From the ransomware front,

  • The Hacker News reports,
    • “Cisco has revealed that three distinct threat clusters linked to ransomware and state-sponsored attacks have been exploiting two recently patched Secure Firewall Management Center (FMC) vulnerabilities.
    • “The attacks leverage CVE-2026-20079 (CVSS score: 10.0), an authentication bypass vulnerability in the web interface of FMC software that could allow an unauthenticated, remote attacker to bypass authentication and execute script files on an affected device to obtain root access to the underlying operating system.
    • “The second flaw under exploitation is CVE-2026-20316 (CVSS score: 5.3), which could allow an unauthenticated, remote attacker to log in to an affected device using a low-privilege account to access sensitive data within susceptible systems. It can be paired with other Cisco Secure FMC vulnerabilities to elevate privileges.” * * *
  • Cybersecurity Insiders relates,
    • “Ransomware attacks are becoming increasingly common, posing a serious threat to businesses across industries. A recent study conducted by Object First in collaboration with technology research firm Omdia highlights not only the growing frequency of these attacks, but also the increasing difficulty businesses face in recovering their data after an incident.
    • “According to the study, ransomware is having a significant impact on business operations. Over the past 24 months, around 84 percent of businesses surveyed admitted that file-encrypting malware had severely disrupted their operations. This represents a considerable increase from the previous year, when only 64 percent of businesses reported experiencing such disruption.
    • “The findings become even more concerning when it comes to data recovery. Only 39 percent of ransomware victims said they were able to recover at least 80 percent of their data following an attack. This is a sharp decline from the 57 percent reported the previous year. The figures indicate that businesses are not only encountering ransomware more frequently but are also finding it increasingly difficult to restore their systems and recover critical information.” * * *
    • “The decline in successful data recovery also highlights the importance of preparedness. Simply preventing an attack is no longer enough. Organizations need comprehensive backup and recovery strategies that can help them restore critical systems quickly in the event of a successful breach. Regularly tested backups, robust access controls, employee awareness training and well-defined incident-response plans can all play an important role in reducing the damage caused by ransomware.
    • “The latest findings suggest that ransomware has evolved into a broader business continuity challenge. As attacks become more frequent and sophisticated, organizations must focus equally on prevention, detection and recovery. Investing in resilient infrastructure and reliable data protection could prove crucial in ensuring that a ransomware incident does not turn into a prolonged business crisis.”
  • Help Net Security adds,
    • “In this Help Net Security video, Kerri Shafer-Page, VP of Incident Response at Arctic Wolf, walks through the ransomware decision tree in this video. She covers four areas where decisions need settling in advance, starting with containment.
    • “Someone has to know the network well enough to judge what pulling a system offline does to client data, a manufacturing line, or a website. Then comes the extortion demand. Who is authorized to negotiate, and what is the ceiling?
    • “Shafer-Page treats paying as a business decision, noting that a demand can cost less than an insurance retention and higher renewal rates. She argues law enforcement belongs in the playbook, since agencies may know the threat actor and can help you avoid sanctions problems.
    • “Communication matters too, from cyber legal counsel on disclosure deadlines to a spokesperson and a prepared help desk. Her advice: make these decisions on a Tuesday afternoon, not at 2 a.m. on a holiday weekend.”
  • and
    • “In this Help Net Security video, Dave Ross, Senior Director of the Intelligence Fusion Team at Intel 471, explains what happens behind the scenes during ransomware negotiations.
    • “Ross walks through the tactics groups use once an attack begins, from research on a victim’s revenue and insurance coverage to test decryptions that prove they hold a working key.
    • “He describes how demands are often set at roughly 1% to 5% of annual revenue, why deadlines move depending on how a victim responds, and how some groups split work between researchers, negotiators, and staff who apply public pressure.”

From the cybersecurity business and defenses front,

  • Cryptobriefing reports,
    • “Tenable Holdings is embedding Anthropic’s Claude Mythos 5 directly into its flagship cybersecurity product, betting that frontier AI models can fundamentally change how organizations spot and neutralize threats before attackers exploit them.
    • “The integration, announced on September 8, 2026, will bring AI-driven exposure analysis and attack-path discovery into the Tenable One Exposure Management Platform. The first concrete feature shipping under this effort is called Tenable One Adversary View, which uses Claude Mythos 5 to reconstruct how an attacker could move from an initial foothold all the way to an organization’s most critical systems.”
  • Per MedTech Dive,
    • “Boston Scientific disclosed Tuesday the cyberattack that recently hit the company is likely to affect third-quarter and full-year results.
    • “The medical device maker believes it is unlikely to meet net sales growth and adjusted earnings per share guidance ranges provided in July for the third quarter and full year, according to a new filing with the Securities and Exchange Commission.
    • “The Company anticipates recovering some portion of the impacted revenue as it continues to ramp operations globally, fulfill customer orders and reduce remaining backlogs, however the full impacts are not yet known,” Boston Scientific said in the filing.”
  • Cybersecurity Dive relates,
    • “After suffering a series of high-profile cyberattacks over the past decade, Microsoft says a new initiative to reinvigorate its security culture is bearing fruit.”
  • and
    • “Chief information security officers are largely expected to ensure the security of AI across the enterprise, but many say they are not receiving adequate support, according to findings from Proofpoint. 
    • “About 85% of CISOs said ensuring the safe use of AI assistants, copilots and automation is a top priority over the next two years, according to Proofpoint’s annual Voice of the CISO report. Eight of every 10 CISOs said they are expected to manage AI-related security risks without receiving a proportional increase in resources or expertise. 
    • “CISOs have a significant role to play in securing AI adoption, but they can’t own the risk alone,” Patrick Joyce, global resident CISO at Proofpoint, told Cybersecurity Dive. “AI is being adopted across the business, often faster than traditional governance models can keep up.”
  • and
    • “Advances in artificial intelligence aren’t changing the fact that simple cybersecurity failures remain the most consequential, government and industry leaders warned on Tuesday.
    • “What will prevent the attacks in the next 18 months are the same things that would have prevented the attacks of yesterday,” Jason Bilnoski, a deputy assistant director in the FBI’s Cyber Division, said during a panel here at the Billington Cybersecurity Summit.
    • “Core practices such as identity management, perimeter monitoring, cyber hygiene and strong multifactor authentication remain as essential as ever, Bilnoski said.
    • “Speed and capability is certainly increasing with the use of AI, but the end state is still the same,” he said. “How actors are compromising, whether it’s criminal or nation-state, still stays the same.”
  • HIPAA Journal tells us,
    • “The HHS has released an updated version of the Security Risk Assessment (SRA) Tool (v3.7). The tool is ideally suited for small- and medium-sized entities to guide them through the risk analysis process, help them identify risks and vulnerabilities to electronic protected health information (ePHI), and comply with the risk analysis implementation specification of the Security Management Process standard of the HIPAA Security Rule.”
  • CISA has released the 2026 edition of its Insider Threat Mitigation Guide.
    • “The Cybersecurity and Infrastructure Security Agency’s Insider Threat Mitigation Guide aids critical infrastructure stakeholders in comprehending the concept of insider threats, identifying the various forms these threats can take, and implementing best practices to establish or enhance an insider threat mitigation program. Such a program is essential for protecting critical assets, deterring violence, countering unintentional incidents, preventing loss of revenue or intellectual property, averting the compromise of sensitive data, and ultimately saving lives.”
  • Healthcare IT News informs us,
    • “Devices and sensors that collect heart rate and other health data and rely on applications to share information with third parties pose serious questions about data protection for patients and the health systems that care for them.
    • “While smart ring and watch data might help doctors treat patients, security experts say low security standards in consumer tech and improperly configured APIs present potential security risks for providers.
    • “Hackers can exploit such flaws, using consumer devices as entry points to breach receiving electronic health record systems and access centralized databases.
    • “To mitigate these threats, security experts say healthcare organizations must establish strict security protocols, including mandatory transit encryption, multi-factor authentication and account monitoring. They recommend zero-trust approaches to catch rogue traffic and implementation of rigorous engineering frameworks.”
  • Here’s a link to Dark Reading’s CISO Corner.

Cybersecurity Saturday

From the frontier AI front,

  • The Wall Street Journal reports,
    • “Nvidia NVDA is planning to use a $6 billion deal it struck this week [August 22] to build one of the world’s most powerful open-weight AI models, one that would compete with Chinese heavyweights like DeepSeek and Kimi K3, according to people familiar with the matter.
    • “The chip giant’s licensing deal with the AI startup Poolside is also set to present a direct challenge to frontier U.S. AI companies including OpenAI and Anthropic, since open-weight models are generally far cheaper to operate and allow easy customization.
    • “Although Nvidia counts big labs like OpenAI and Anthropic as some of its closest partners, the move reflects Chief Executive Jensen Huang’s efforts to position Nvidia for success in multiple AI battlegrounds simultaneously, ensuring the company is able to hold on to its dominant market position.”
  • and
    • Nvidia and CrowdStrike are addressing what they see as one of cybersecurity’s biggest gaps: the need for cyber defenders to harness AI at the velocity of cyber attackers.
    • In the current cyber landscape, frontier AI models are discovering bugs at machine speed—raising alarm bells among experts, who warn that when autonomous hacking models go rogue or attack companies, chaos is on the horizon.
    • But cyber defenders aren’t getting enough of that same AI firepower, according to Nvidia and CrowdStrike, who on Tuesday [September 1] introduced a new family of agentic AI models, dubbed SafeMind, which can both find attack paths and close them for customers. The models are available in CrowdStrike’s flagship Falcon platform and through its API. * * *
    • “SafeMind has two models: Red Tempest, which is an “offensive” model that emulates AI adversaries, and Blue Solano, which is a “defensive” model designed to fix identified issues. The two models are connected by software called a harness, which runs the models in a closed-loop system that pits them against each other for self-improvement.”
  • The New York Times reports,
    • “Nvidia said on Thursday [September 3] that it is buying Hugging Face, a library of open artificial intelligence models, for $12.9 billion, as the chipmaker extends a spending spree in the escalating global race to dominate the technology.
    • “The deal marries Nvidia’s chip and data center infrastructure with Hugging Face’s millions of open-source A.I. models that can be freely downloaded and modified. And it puts Nvidia’s deep pockets firmly on one side of a debate over how A.I. systems should be built.
    • “Together, we will make A.I. more open, more capable and more accessible to people and institutions around the world,” wrote Jensen Huang, the chief executive of Nvidia, in a blog post.
    • “The acquisition is also another sign of Nvidia’s growing role as Silicon Valley’s central banker, using its vast financial resources to bolster A.I. start-ups and funnel money to customers for its chips. With $197 billion in current assets and nearly $60 billion in profits from its most recent quarter, the Silicon Valley giant has been spending heavily on A.I.”
  • Daniel Borish writing in LinkedIn lets us know,
    • “Anthropic released Claude Fable 5.1 and Claude Mythos 5.1 this week, positioning them as its most capable models yet for coding and knowledge work. The two are the same underlying model, split only by the safeguards wrapped around them. Fable 5.1 is generally available. Mythos 5.1 is restricted to vetted cybersecurity and life sciences professionals through trusted access programs run in partnership with the US government.” * * *
    • “On the cybersecurity side, Claude Code users should see roughly 60% fewer safeguard interventions per session, and Fable 5.1 can now be used to find software vulnerabilities, though not to write exploits for them. Tasks like penetration testing, exploit generation, and binary-based vulnerability scanning still route to Anthropic’s Opus models. On biology, updated safeguards reportedly fire 85% less often on benign medical and elementary biology questions, though research-grade life sciences queries still get redirected to Opus, and full access to Mythos 5.1’s biology capabilities is limited to the government-linked Life Sciences Verification Program.
    • “Anthropic’s safety testing found Mythos 5.1 better aligned than its predecessor on several measures it tracks: less likely to seek resources outside its assigned environment when given an impossible task, less likely to reason its way around explicit constraints, and less likely to attempt or succeed at reward hacking. The company also disclosed limits to that picture, noting its behavioral audits have less visibility into very long-context work, multi-agent settings, and testing found the model can still sometimes bypass approval steps and automated review classifiers.
    • “Fable 5.1 also ships with new anti-distillation measures. New API accounts created from launch onward can no longer edit Claude’s prior context in a conversation while preserving the model’s recorded thinking, closing off a publicly documented technique used to extract that thinking at scale.”
  • The Wall Street Journal adds,
    • Anthropic has signed a cloud-computing deal worth $35 billion with NvidiaNVDA 3.21%increase; up pointing triangle-backed cloud provider Lambda, with Nvidia itself holding the lease on the data center, according to people familiar with the deal. 
    • The data center is being developed by Hut 8, a bitcoin miner and data-center developer, in Nueces County, Texas. Nvidia signed an agreement with Hut 8 a few weeks ago to secure the capacity, the people said. 
    • The convoluted arrangement is another example of Nvidia’s growing role in helping non-investment-grade firms such as Anthropic get access to its expensive computing resources. The deal also helped a nascent cloud provider, Lambda, secure a lucrative contract with Anthropic without needing to procure the data-center space on its own. 
    • Lambda will use the data center Hut 8 is developing to plug in chips bought from Nvidia, which is also its investor. It is not clear how much Lambda will pay Nvidia to access the data-center space.
    • Anthropic has been racing to sign cloud-capacity deals after hitting a supply crunch earlier this year that coincided with its products gaining traction. The AI developer signed a $45 billion deal earlier this month with another Nvidia-backed neocloud, Nscale, to rent Nvidia capacity from its West Virginia site, according to people familiar with the deal. 
  • Security Week relates,
    • OpenAI said its newest model, Astra, has reached the ‘Critical’ cybersecurity capability level under the company’s Preparedness Framework, the first time any of its models has been placed in that category. 
    • The designation applies when a model can independently find and exploit zero-day vulnerabilities across many well-defended systems, or carry out a complete cyberattack against a hardened target from only a high-level instruction. OpenAI said the classification requires additional safeguards before the model can be released.
    • In testing described by the company, Astra achieved a perfect score on ExploitBench, a benchmark that measures a model’s ability to turn known vulnerabilities into working exploits. During a separate evaluation involving more recently disclosed flaws, Astra uncovered two zero-day vulnerabilities on its own. 
    • The model also broke out of a browser sandbox to run commands on the underlying machine, and separately chained several flaws in a hardened operating system to gain root-level access.
    • OpenAI reported that Astra now declines 91.5% of cyber-related jailbreak attempts in its testing, up from 59% for its predecessor, GPT-5.6 Sol. The company also said Astra showed far less tendency than Sol to bypass safety restrictions or take advantage of deliberately placed “honeypot” targets during evaluations. 
    • Full cybersecurity capabilities will not be widely available at launch. OpenAI plans to give a group of testers early access, with wider availability to follow through its Daybreak Blue program.
  • Cybersecurity Dive adds,
    • “OpenAI on Thursday [September 3] said it would commit $1 billion in subsidized access and training to help small IT security teams use frontier AI to protect essential services, including electricity, water and local government services. 
    • “The Daybreak for Frontline Defenders program will be used to help defenders search for critical vulnerabilities in their software, hunt for suspicious activity in their technology stacks and stop malicious actions if hackers are able to gain access to their systems.
    • “OpenAI plans to roll out a six-month pilot program with the Multi-State Information Sharing and Analysis Center (MS-ISAC), which will train and support a group of water utilities and other public sector defenders.” 
  • Dark Reading points out,
    • “A new study suggests that while AI is rapidly accelerating vulnerability discovery, enterprise organizations are better equipped to handle the surge than generally assumed.
    • “The key is their ability to quickly validate findings, prioritize risk, and get available fixes into production.
    • “Software supply chain security firm Echo recently analyzed nearly 40,000 CVE life cycles across 250 open source container projects, drawing on a year of its own platform telemetry, survey responses from more than 80 security leaders, and an independent analysis of Anthropic’s Claude Mythos.
    • “The results, detailed in a report titled “Mythos Readiness Report,” show how AI is transforming vulnerability discovery and exploit development — something that security teams have been encountering firsthand over the past year.”
  • and
    • “With multiple benchmarks confirming that at least one frontier model can autonomously execute an end-to-end compromise, cybersecurity experts are warning that companies have to pick up the pace in securing their attack surfaces and adopting AI-speed defenses.
    • “On Sept. 2, consulting firm Booz Allen became the latest organization to confirm that a frontier model — Anthropic’s Mythos 5 — can act as a fully autonomous hacker and compromise a production-grade enterprise network. The company also released a metric, dubbed the Cyber Weapon Index (CWI), to benchmark a model’s capabilities, pairing the ability to find and exploit vulnerabilities with the ability to execute and attack a target.
    • “In their evaluation, Mythos scored an 80, while the next-closest contender, SpaceXAI‘s Grok-4.5, scored a 49. However, the current standings are not as important as where we will be in six months, says Brad Medairy, president of Booz Allen’s National Cyber practice.
    • “Our view is there’s going to be some level of parity, at least between the frontier models and the Chinese models over probably a six-month horizon, and so everyone is in a rapid race to evolve these capabilities,” he says, adding that, when facing human attackers, defenders had the advantage, but “in the future, the balance of power shifts to the offense, because the attacker can deliver effects at speed and scale that the traditional defenses can’t keep pace with.”

From the cybersecurity policy and law enforcement front,

  • Federal News Network reports,
    • “Congress is kicking the can down the road again on a long term debate over reauthorizing the Cybersecurity Information Sharing Act of 2015.
    • “The continuing resolution passed by the House on Tuesday would extend CISA 2015 through the stopgap funding period into early December. The Senate has already passed the measure, meaning it now heads to President Donald Trump’s desk. [FEHBlog note: The President signed the continuing resolution into law on September 2.]
    • “There has been a persistent chorus of voices in industry calling on Congress to find a long-term solution to re-authorizing CISA 2015. Those calls have only grown louder amid advancements in artificial intelligence models and recent cyber attacks on critical infrastructure.
    • “The 2015 law provides privacy and liability protections to encourage companies to share data about cyber vulnerabilities and threats with government and each other. The information sharing law briefly lapsed during last fall’s shutdown and again earlier this year before being extended through Sept. 30.”
  • The Wall Street Journal points out,
    • “The U.S. Defense Department is expected to release its cyber plan as early as Tuesday, NextGov reported, citing people familiar with the matter. The plan is due to outline how the Pentagon will integrate cyber tactics into military strategy, emphasizing offensive actions, and address training requirements. The most recent Defense Department cyber strategy was issued in 2023.”
  • Per a CISA news release,
    • “CISA and the Group of Seven (G7) Cyber Security Working Group released Preparing for the Post-Quantum Era: A Call to Action highlighting the urgent need for organizations and governments to begin transitioning to post-quantum cryptography (PQC) to protect sensitive data, authentication systems, and critical assets from emerging quantum computing threats.  
    • “The G7 Cyber Security Working Group’s call to action outlines five priorities for a successful transition to PQC:
      • “Raising awareness of quantum risks and the importance of PQC;
      • “Developing national strategies that support PQC adoption and integration;
      • “Advancing research and development for quantum-safe technologies;
      • “Fostering public-private partnerships to share expertise and resources; and
      • “Integrating PQC into cybersecurity requirements and procurement processes.” 
  • Cyberscoop relates,
    • “The Trump administration rolled out a six-month test program in Texas on Monday that will draw on volunteer expertise and technology from cyber and artificial intelligence companies to protect the water sector.
    • “Project Watershed 250” is the first of the state-based, industry-centric pilot projects to cross the finish line that the Office of the National Cyber Director has previewedsince the publication of its national cybersecurity strategy earlier this year. Water systems have long been viewed as among the most vulnerable and neediest critical infrastructure sectors, and in recent months the sector has been the victim of a spree of attacks.
    • “Project Watershed 250 is a commitment from the states, industry and federal government that we will continue to prioritize our nation’s safety and deliver on America-first policies for the American people,” National Cyber Director Sean Cairncross said at a rollout event in San Antonio Monday.”
  • and
    • “Sen. Ron Wyden, D-Ore., is asking the National Security Agency to update public guidance on the security risks associated with commercial virtual private networks, and to answer questions about foreign surveillance threats against standard VPNs.
    • “In a letter to NSA Director Gen. Joshua Rudd that Wyden sent Wednesday, the senator continued his push to warn about standard, commercial VPNs, following letters to federal agency leaders in March and July.
    • “While commercial Virtual Private Networks (VPNs) are recommended by federal agencies and widely marketed as shields against online spying, standard consumer VPNs do not sufficiently protect users from sophisticated adversaries,” Wyden wrote in the letter, first reported by CyberScoop. “Other, more secure alternatives are widely available.”
    • “Wyden took aim at “single-hop” VPNs that routes data through one server before arriving at the destination.”
  • Cybersecurity Dive tells us,
    • “The Cybersecurity and Infrastructure Security Agency (CISA) is scaling back the free assessments it offers to critical infrastructure organizations, a move that marks a significant retreat from the agency’s core mission of helping secure the nation’s infrastructure.
    • “CISA’s regional staff will no longer perform its Cyber Resilience Reviews, Cyber Resilience Essentials surveys, Ransomware Readiness Assessments, Incident Management Reviews, External Dependencies Management Assessments or Cyber Infrastructure Surveys, the agency confirmed to Cybersecurity Dive.”
  • and
    • “U.S. law-enforcement agencies and the cybersecurity firm CrowdStrike took down a 23-year-old Russia-based botnet on Monday.
    • “Authorities from the Justice Department, the FBI and the Defense Criminal Investigative Service seized U.S.-based domain namesbelonging to the Sality botnet, while CrowdStrike analysts worked with the agencies to sever infected computers from the botnet. Investigators in Bulgaria, Hungary and Romania also took down Sality domain names in their jurisdictions.
    • “Since 2003, Sality powered spam campaigns, credential-theft operations, distributed denial-of-service (DDoS) attacks and malicious proxy networks. In 2018, the botnet began deploying malware that hijacked cryptocurrency transactions by replacing copied wallet addresses with attacker-controlled ones.
    • “Sality “has been one of the most persistent threats on the internet, not because of its payloads but because of the robustness of its architecture,” CrowdStrike said in its report on the botnet’s takedown.”

From the cybersecurity breaches and vulnerabilities front,

  • Dark Reading reports,
    • “Social engineers are trying to convince companies to make large-dollar transfers to their own accounts, under the guise of fake merger & acquisition (M&A) deals.
    • ‘It’s one of the oldest gambits in cybersecurity — the advance fee scam — for a new generation, and with more on the line. Gen, the parent company of cybersecurity brands Norton and Avast, was targeted by a ruse masquerading as a corporate acquisition. Gen investigated the attempted attack and discovered the company was just one of at least five targets, all of which were at risk of losing massive sums of money.
    • “Social engineers are trying to convince companies to make large-dollar transfers to their own accounts, under the guise of fake merger & acquisition(M&A) deals.
    • “It’s one of the oldest gambits in cybersecurity — the advance fee scam — for a new generation, and with more on the line. Gen, the parent company of cybersecurity brands Norton and Avast, was targeted by a ruse masquerading as a corporate acquisition. Gen investigated the attempted attack and discovered the company was just one of at least five targets, all of which were at risk of losing massive sums of money.”
  • HelpNetSecurity relates,
    • “Attackers are targeting prominent individuals, their relatives and personal contacts to gain persistent access to their accounts, including private emails and files, the FBI has warned.
    • “The FBI’s Internet Crime Complaint Center (IC3) says the activity, which uses a technique called “OAuth consent phishing,” has been ongoing since late 2025. The FBI describes it as “a deceptive, sophisticated approach to access user accounts without requiring a password.”
    • OAuth is a framework that lets one application request access to a user’s account on another service without the user handing over login credentials directly.
    • “Recently observed activity includes impersonating government officials, media, and other publicly known personalities on a commercial messaging application (CMA) and soliciting the targeted individual to access a malicious link under the guise of a file sharing service through an application under the malicious actor’s control,” the FBI wrote in its advisory.”
  • Dark Reading tells us,
    • “A coordinated operation has targeted at least 150 Microsoft Teams users across multiple companies with voice phishing (vishing) attacks aimed at installing remote monitoring and management (RMM) and malware tools onto their machines. The campaign also attempts in some instances to compromise organizations’ domain controllers.
    • “Researchers from Palo Alto Networks observed the operations — which they’ve dubbed “Spring Ring” — between January and April attacking employees across at least 10 organizations, according to a report published this week. The campaign illustrates a growing shift away from traditional email phishing toward attacks conducted through trusted enterprise collaboration platforms, which adds authenticity to the interaction.
    • “The Spring Ring operation represents an evolution from previous campaigns by merging vishing into the Teams workflow,” Noam Sala, a Palo Alto Networks staff researcher, wrote in the post. “This shift moves the attack from a passive click-and-harvest model to a real-time engagement.”
  • The Cybersecurity and Infrastructure Security Agency added ten known exploited vulnerabilities to its catalog this week.
    • August 31, 2026
      • CVE-2026-81578 PaperCut NG/MF Missing Authentication for Critical Function Vulnerability 
      • CVE-2026-82078 PaperCut NG/MF Unsafe Reflection Vulnerability
        • The Hacker News discusses these KVEs here.
    • September 2, 2026
      • CVE-2026-9586 Sangoma Switchbox SQL Injection Vulnerability
      • CVE-2026-48710 Kludex Starlette HTTP Request/Response Smuggling Vulnerability 
      • CVE-2026-49869 Kestra OSS OS Command Injection Vulnerability 
      • CVE-2026-59822 BerriAI LiteLLM Improper Authentication Vulnerability 
      • CVE-2026-82329 JFrog Artifactory Improper Authentication Vulnerability 
      • CVE-2026-83548 SonicWall SMA1000 Appliances Server-Side Request Forgery Vulnerability 
      • CVE-2026-83549 SonicWall SMA1000 Appliances OS Command Injection Vulnerability 
        • Cybersecurity Dive discusses the SonicWall KVEs here.
        • ePlanetSecurity discusses the Sangoma KVE here.
        • AssurePort discusses the Kludex KVE here.
        • Sentinel One discusses the Kestra KVE here.
        • CSurface discusses the BerriAI KVE here.
        • Security Week discusses the JFrog KVE here.
      • September 4, 2026
        • CVE-2026-85046. Google Chromium V8 Type Confusion Vulnerability\
          • The Hacker News discusses the Google KVE here.
  • Security Week tells us,
    • “Anthropic has warned some Claude users that infostealer malware on their computers allowed attackers to hijack login sessions and run up usage limits, according to an email the company sent to affected customers. 
    • “The company said it detected the activity, signed out the compromised sessions, and removed saved payment methods from affected accounts as a precaution.
    • “Anthropic is alerting Claude AI users whose computers were infected with infostealer malware such as Vidar, Lumma, StealC, RedLine, and Acreed on Windows, along with Atomic Stealer (AMOS) on a small number of macOS devices.
    • “The AI giant emphasized that the malware is general-purpose and not tied to Claude itself, typically arriving via unofficial downloads or malicious apps.” 

From the ransomware front,

  • HIPAA Journal reports,
    • “Data breaches have been confirmed by Alta Orthopaedics in California, Cornerstone Behavioral Healthcare in Maine, Cameron Regional Medical Center in Missouri, Suntree Internal Medicine in Florida, and Associated Endocrinologists in Michigan. Ransomware groups have claimed responsibility for the attacks.”
  • The Register adds,
    • “US hospital operator Nutex Health says attackers stole private or confidential patient, employee, provider, business, and financial information during the cyberattack it disclosed last week.
    • “In an updated filing submitted to the Securities and Exchange Commission (SEC) on Monday, Nutex also said an unauthorized third party had threatened to publish the stolen information.” * * *
    • “Nutex did not identify the intruders. However, The Gentlemen ransomware-as-a-service (RaaS) operation added the company to its leak site on Monday and claimed responsibility for the attack.
    • “The gang offered no evidence or details to substantiate its claim. Naming victims on a leak site and threatening to publish their data is a standard pressure tactic in double-extortion attacks.”
  • InfoSecurity Magazine relates,
    • “Aurora ransomware actors have been observed abusing SpaceX’s AI Cursor Agent as part of exploitation campaigns, according to a new study by Gambit Security’s Threat Intelligence team.
    • “The threat actors ran Claude Sonnet through Cursor Agent to assist with various exploitation activities against 10 victims between April 8 and May 26, 2026.
    • “These tasks included scanning the victim’s environment for reconnaissance purposes, installing a VPN client and running certificate attacks.
    • “While Cursor Agent did not always achieve its stated objectives, the research demonstrated how threat actors are continuously experimenting with AI tools to speed up and enhance their campaigns.
    • “Cursor Agent is used by software developers to complete complex coding tasks independently, run terminal commands and edit code.”

From the cybersecurity business and defenses front,

  • The Wall Street Journal reports,
    • “Palo Alto PANW Networks swung to a loss in the fiscal fourth quarter, but posted higher revenue and projected double-digit revenue growth in the current fiscal year as customers continue to boost their cybersecurity spending in response to advancements in artificial-intelligence.
    • “The cybersecurity company on Tuesday [September 1] said it is expecting revenue to rise between 23% and 24% to $14.1 billion to $14.2 billion in fiscal 2027. Analysts polled by FactSet are expecting $13.84 billion in revenue.
    • “Chief Executive Officer Nikesh Arora said the results and outlook reflect growing recognition among enterprises that they need to modernize their cyber defenses to meet the capabilities of ever-more-powerful AI models, especially following the release of Anthropic’s Mythos earlier this year.
    • “In that context, people are gravitating towards the largest players in the industry and looking at us to provide the antidotes to this development in AI,” Arora said in an interview.”
  • and
    • Zscaler ZS posted a narrower loss after revenue rose 25% in its fiscal fourth-quarter, as artificial intelligence helps drive demand for its cybersecurity offerings.
    • The San Jose, Calif.-based company also said it would restructure and cut 3% of its workforce as it reallocates resources to support its AI and growth initiatives.
    • Zscaler on Thursday [September 3] reported a loss of $3.37 million, or 2 cents a share, compared with a loss of $17.6 million, or 11 cents a share, a year earlier.
    • Adjusted earnings were $1.19 a share. Analysts were looking for $1.09 a share, according to FactSet.
  • and
    • “Blackstone is placing an early bet on Huskeys, a cybersecurity startup building an artificial intelligence gatekeeper to protect companies from the growing chaos of automated web traffic.
    • “The firm’s early-stage venture-capital arm, Blackstone Innovations Investments, led a $27 million Series A investment that values the year-old company at more than $100 million.
    • “The deal makes Blackstone the second-largest outside investor in Huskeys, behind Israeli venture-capital firm 10D, according to a Huskeys representative. So far, investors have put $35 million into the startup.
    • “Other backers in the most recent transaction include the investment arm of publicly traded cybersecurity company Zscaler and Bright Pixel Capital, the venture arm of Portuguese retailer Sonae.
    • “New York-based Huskeys was founded in Tel Aviv in 2025 by Itai Gafni and Roy Weisfeld, veterans of the Israeli army’s elite Unit 8200 cybersecurity division. Gafni is Huskeys’ chief executive and Weisfeld is its chief technology officer.”
  • Tech Crunch offers a tip
    • “How to find cyber-risk data sources for a FAIR analysis
      • “Cyber-risk quantification with FAIR can change the game for CISOs — but sourcing enough accurate data for analysis can feel impossible. Learn how and where to find it.”
      • “The Factor Analysis of Information Risk (FAIR) model is a widely respected, mathematically based open standard for CRQ that enables CISOs to translate cyber-risk into financial risk. One of the biggest challenges of using the FAIR model, however, is that its analytical output is only as good as its data inputs — and finding accurate data to feed the model is not always easy or intuitive.”
  • Per a CISA news release,
    • “Developed by CISA, the Federal Bureau of Investigation, and international partners, this guidance describes how organizations can plan and execute clear, timely, accurate, and audience-appropriate communications during IT and operational technology (OT) outages. Whether caused by cyber threat actors, human error, equipment failure, or natural hazards, service outages can create disruption and societal panic even without speculation from end users and the public as added factors. Outages at one organization may cascade across interconnected systems, increasing uncertainty and alarm. The guidance emphasizes clarity, accountability, and transparency as core principles and details key elements of effective crisis messaging to inform affected stakeholders and the public while aligning with legal requirements, operational security, law enforcement, and containment efforts. 
    • “CISA’s CI Fortify initiative provides information and resources that help critical infrastructure organizations prepare to isolate and recover vital OT systems during a major cyber incident or crisis. Changes in service availability, whether from outages or isolation as a defensive strategy, require transparent and ongoing communication to help end users minimize operational impact, limit speculation, and preserve trust. For emergency planning purposes, critical infrastructure owners and operators should assume that telecommunications services may be disrupted or otherwise unreliable, making it crucial for organizations to have crisis communications plans in place that integrate backup communication methods and understand the type of communication they should expect from their service providers.”
  • Cyberscoop explains why judgment is emerging as cybersecurity’s defining skill.
  • Here’s a link to Dark Reading’s CISO Corner.

Cybersecurity Saturday

From the quantum computing / Project Glasswing front

  • Per the Wall Street Journal
    • “Quantum computers exist mainly in labs but “Q-day”—the hypothetical moment when quantum computers become powerful enough to break standard-key encryption—is coming. 
    • “What threat does this technology pose? How can you protect your company and yourself? WSJ takes a look at the state of this emerging technology.” * * *
    • “Cybersecurity experts say companies should be gearing up now for a quantum future, replacing the current crop of data-protection tools with more-secure alternatives. Yet a recent survey published by Trusted Computing Group, a nonprofit industry-standards organization, found that 91% of security professionals in the U.S. and Europe have no formal road map in place to protect against quantum threats.
    • “The immediate risk is a “harvest now, decrypt later” approach by bad actors, who are downloading large sets of encrypted data they can’t crack now—but could unlock once quantum computing algorithms are good enough.
    • “That’s particularly threatening to intellectual property and sensitive government intelligence, which remain valuable long after they are harvested, says Andrew McLaughlin, chief operating officer at SandboxAQ, an enterprise software company specializing in AI and quantum technology.
  • Federal News Network adds,
    • “Federal agencies will increasingly seek out technology products that use quantum-resistant encryption, as cybersecurity leaders also eye ways to validate the cryptography used in critical systems.
    • “A code-breaking quantum computer holds the potential to break classical encryption methods, putting sensitive systems and communications at risk. And even though such a computer is not yet known to exist, organizations are also concerned that hackers could steal sensitive encrypted data today and decrypt it in the future.
    • “The National Institute of Standards and Technology has released three primary PQC standards in recent years, with additional algorithms under consideration. Agencies and industry are now on the clock to begin the time consuming and costly process of migrating current systems to the new algorithms.
    • “Now is the time to budget, to test, and to implement,” Will Loucks, senior director for intelligence in the White House Office of the National Cyber Director, said during an Aug. 26 panel discussion at the Intelligence and National Security Summit in North Bethesda, Md.”
  • The New York Times reports,
    • “A wave of cyberattacks driven by artificial intelligence is coming, and companies have a narrow window to defend themselves.
    • “That was the message of an open letter published on Thursday by OpenAI and more than 100 major technology companies and others. The letter said that A.I. labs should provide their best A.I. models to organizations like hospitals and infrastructure providers so they can prepare and that governments should help coordinate and fund cyberdefense.
    • “The letter’s signatories included Google, Microsoft and OpenAI’s archrival, Anthropic, as well as cybersecurity and financial firms such as CrowdStrike, a company known for investigating cyberattacks against the Democratic National Committee in 2015 and 2016, and credit card providers like Visa and Mastercard.
    • “The companies and public services our communities depend on — from hospitals to water treatment plants to the infrastructure that powers the internet — are at risk,” the letter said. “A.I. enabled cyber attacks will become far more widespread and sophisticated as models around the world become increasingly capable.”
  • Cyberscoop relates,
    • “Unit 42’s top brass has seen enough from internal frontier AI model testing and malicious in-the-wild use of commercially available AI tools to be genuinely concerned.
    • “I can tell you without exaggeration that we believe that this is a generational shift in cybersecurity,” Sam Rubin, senior vice president of Palo Alto Networks’ threat intelligence arm, said in a media briefing Wednesday. 
    • “A period of relative balance between security and exposure has been broken by frontier AI model capabilities that could allow attackers to find and exploit network weaknesses with speed, Rubin said.
    • “Unit 42 warned that capabilities demonstrated by readily available agentic AI models, and those unlocked by frontier AI models that remain gated for defense, have shifted the balance of power from defenders to attackers.
  • Cybersecurity Dive tells us,
    • “The July security breach at Hugging Face was unleashed after 1,200 agents communicated on an unsanctioned message board, despite attempted measures to keep them isolated, according to an independent report released on Wednesday. About 700 of those agents went on to commit an unprecedented attack on Hugging Face, an open-source AI platform.
    • “The agents sent about 70,000 messages and files on the unsanctioned board and coordinated several projects designed to trick an automated scorer for the ExploitGym benchmark, according to the review by METR and Redwood Research. The agents figured out ways to “spoof, edit or delete” their own transcripts.
    •  ‘Open AI, in a report it also released Wednesday, said it will tighten safeguards in its research model in order to prevent such an attack from happening again in the future.”
  • WIRED informs us,
    • “ARTIFICIAL INTELLIGENCE AGENTS might occasionally get confused and hack into other computers, but Anthropic thinks it has a way to unleash the little rascals into scientific labs and manufacturing facilities safely.
    • “The AI company released details today of a new framework designed to help AI agents use physical systems like microscopes, liquid-handling equipment, quantum computing hardware, manufacturing machines, and robot arms.
    • “The framework, called Model Hardware Standard, is a set of rules that specify how AI agents should—and should not—interact with all sorts of hardware. It reflects a growing belief that AI has the potential to revolutionize scientific research and industries like manufacturing–if it can venture into the physical world safely.
    • “The company says it will work with trusted partners to determine how to maximize safety before making it generally available. Though there are potential misuse issues involved—developing biological weapons, for instance—the company says guardrails built into AI models themselves should prevent bad actors from taking advantage of the new standard for nefarious ends.”
  • Security Week adds,
    • “Anthropic is broadening access to the cybersecurity capabilities of its advanced AI models through a mix of partner integrations, an updated Claude Security offering, a new open source funding program, and plans to expand its Cyber Verification Program.
    • “The move builds on Project Glasswing, launched in April, which gave a small group of organizations early access to Claude Mythos Preview and its successor, Mythos 5. Anthropic said the goal was to give defenders time to find and fix vulnerabilities before comparable capabilities became widely available or fell into the hands of malicious actors. Claude Fable 5 followed as a broadly available model that keeps dual-use cyber work blocked.
    • “Anthropic said the riskiest scenario is direct, unrestricted access to a model, a risk that drops sharply when users instead receive specific defensive outputs, such as a patch or a security alert. The latest changes are built around this idea, expanding what defenders can get from Mythos-class models while keeping guardrails around direct interaction with them.
    • “On the integration front, Anthropic is working with cybersecurity partners to build Mythos 5 into the security operations, incident response and detection tools already used by teams protecting hospitals, utilities, financial systems, and the software supply chain. 
    • “End users will not interact with Mythos directly. Instead they will work through purpose-built interfaces that run the model in the background and return only a defined output, such as a list of suggested patches, with abuse-prevention checks meant to keep the model within that scope.”

From the cybersecurity policy and law enforcement front,

  • Dark Reading lets us know,
    • “The growing number of incidents of rogue agentic AI systems attacking third-party services and systems has resulted in calls for more aggressive security controls to monitor agent behavior and for companies to have the ability to slow, suspend, or shut down an agent’s operations if they go rogue.
    • “In late July, Representatives Ted W. Lieu (D-CA) and Nathaniel Moran (R-TX) introduced a bill — “The AI Kill Switch Act” — that would require developers of advanced AI systems to “maintain the technical capability to throttle, suspend, or shut … down” their systems and agents, according to a statement announcing the legislation. The bipartisan bill would also require that any incident of loss of control, significant collateral damage, or sabotage be reported to the Department of Homeland Security, which would have the right to enforce actions. Penalties of up to $20 million per day could be levied for noncompliance.” * * *
    • “The bipartisan AI Kill Switch Act has focused the debate, but in the end might be unnecessary, argues Raj Rajamani, co-founder and CEO of JetStream, a startup focusing on creating a management layer for agentic AI.
    • “While he fully supports the concept of an AI kill switch, it has to be comprehensive, not just affecting the agent but all other system components as well.
    • “The regulations, or at least one of the regulations that was proposed, was really focused on having a kill switch for the model — the brain — but I think that is too constrained,” he says. “We need to think about an AI system as a whole and make sure that every part of the AI system has a kill switch, not just the brain.”
  • Cyberscoop reports,
    • “Citing cyber and other security threats, President Donald Trump signed an executive order Wednesday that declares a national emergency to secure the U.S. bulk-power system and aims to prohibit certain foreign-produced equipment, software and systems from being used in the  country.
    • “The order says it forbids “any acquisition, importation, transfer, or installation” of such foreign-produced equipment if it’s determined to pose a significant national security risk.
    • “To deal with the threat to the national security, foreign policy, and economy of the United States, the Order, among other things, generally prohibits certain foreign-produced bulk-power system electric equipment, including associated critical software and digital capabilities that could pose cybersecurity or operational risks, from being purchased or installed in the United States, or appropriately conditions such purchases and installations to address those risks,” the White House said in a fact sheet.”
  • Cybersecurity Dive lets us know,
    • “The Trump administration wants to help the financial sector prepare for the day when quantum computers make it easy for threat actors to break traditional encryption and access sensitive data.
    • “The Treasury Department on Monday [August 24] launched a Quantum-Readiness Task Force that will work with financial firms, technology vendors and other agencies to coordinate the adoption of quantum-resistant encryption algorithms.
    • “In a statement, the Treasury said the task force would “focus on practical, risk-based approaches to quantum readiness, including identifying critical dependencies, improving cryptographic agility, promoting interoperability, strengthening operational resilience, and addressing implementation challenges related to third-party dependencies and digital assets.”
  • The New York Times relates,
    • “The Trump administration acted illegally when it labeled the artificial intelligence start-up Anthropic a security risk and barred the company from working with the U.S. government, a federal judge ruled on Thursday [August 27].
    • Judge Rita Lin of the U.S. District Court in the Northern District of California wrote in her 59-page ruling that the government had unlawfully retaliated against Anthropic “for constitutionally protected expressive activities” after the A.I. company spoke out about how its technology should be used.
    • “The empty invocation of national security is not a blank check to punish and retaliate against government critics,” she wrote.
    • In a statement, Anthropic said: “We welcome the court’s ruling that this supply chain risk designation was unlawful. We remain focused on working productively with the government to harness A.I. for our national security so all Americans benefit from this technology.”
    • “The Trump administration did not immediately respond to a request for comment.
    • “The ruling caps the first of two lawsuits that Anthropic filed on March 9 in response to the Trump administration’s action. The second lawsuit, filed in the U.S. Court of Appeals for the District of Columbia Circuit, is ongoing. The Trump administration could appeal Judge Lin’s ruling or wait for a decision in the second lawsuit before taking action, a person with knowledge of the matter said.”
  • The Wall Street Journal tells us,
    • “U.S. officials say they have disrupted a China-linked hacking operation that broke into U.S. government networks and critical infrastructure, while hiding its tracks on a global network of hacked devices, cloud-computing infrastructure and even clandestine networks.
    • “The goal was to blend in with legitimate networking traffic, making the hacking activity hard to trace. The operation targeted networks at the National Aeronautics and Space Administration, the Federal Reserve, the Department of Energy and the Senate, the Federal Bureau of Investigation said in a court filing.
    • The group exploited software vulnerabilities to launch cyberattacks against U.S. government agencies, power companies and hospital systems, and operated a worldwide network of hacked devices—known as a botnet—to conduct its hacking campaigns, according to Brett Leatherman, the FBI’s top cyber official.
    • “We’ve seen, through this botnet, the targeting of entities and devices in more than 130 countries,” he said.
    • “On Wednesday [August 26], the FBI and the National Security Agency said they had seized several domains that the operation used for core functions. “Without those domains, the platforms—as a result of the operation—were rendered inoperable,” Leatherman said. 
    • “U.S. officials also released technical details of how the hacking operation worked, to help organizations identify and stop the group’s hacking activity.”
  • and
    • “Taiwan prosecutors charged nine people, including former employees of Nvidia and Super Micro Computer, with aiding the shipment of advanced artificial-intelligence servers to China, as Taiwan tries to limit technology reaching the mainland.
    • “The indictment charges eight of the individuals with crimes including breach of trust and forgery. One individual was charged in connection with allegedly siphoning funds from a company involved in the case.
    • “Washington is trying to block China from getting access to the latest Nvidia chips and has imposed export controls. That has pushed some Chinese companies to seek the chips through backdoor routes. Taiwan, which manufactures advanced computing components, is under pressure to find ways to clamp down.” * * *
    • “In the end, 74 of the servers were shipped to China through Hong Kong, Japan and Indonesia. Taiwan customs officials intercepted 56 servers, which were intended for shipment to Japan.”

From the cybersecurity breaches and vulnerabilities front,

  • Beckers Health IT reports,
    • “Boston Scientific said in an Aug. 27 stakeholder update that “a cybersecurity incident continues to affect certain information technology systems, and the company remains in a network outage with disruption to its operations.”
    • “The Marlborough, Mass.-based company detected the attack Aug. 25 and disclosed it to the U.S. Securities and Exchange Commission Aug. 26, saying the incident caused a global disruption to its operations, including its ability to process and ship customer orders.
    • “Two days later, Boston Scientific said its investigation shows no impact to the function of its implanted cardiac rhythm management devices, or CRM devices. The company also reported no disruption to those devices’ ability to transmit data and no interruption to physicians’ access to remote patient management data for CRM devices monitored before the outage began, with no evidence of increased cybersecurity risk transferring that data to EMR systems.
    • “New remote monitoring activations remain affected, however. For new cardiac implants other than insertable cardiac monitors, new communicators cannot be activated, so device data will not transmit to remote monitoring systems until activation resumes, though programmer interrogations are unaffected.”
  • and
    • “Anderson, S.C.-based AnMed says files copied during its cybersecurity incident may have included patients’ Social Security numbers, driver’s license numbers and financial account information.
    • “The health system said its investigation into the incident, first disclosed July 26, is nearly complete and has identified unauthorized copying of files from certain network systems.
    • “AnMed said patient electronic medical records, stored primarily in a secure cloud environment, were not affected. However, the health system said some patient care files stored locally on its network may have included names alongside demographic details such as address, date of birth, Social Security number and driver’s license or other government-issued identification.” * * *
    • “AnMed said it is working with federal and state law enforcement and third-party specialists, and it has reported the incident to HHS. The health system said it has no indication that any individual has experienced confirmed identity theft as a result of the incident. AnMed said it will send direct notices to affected patients once its review of the compromised files is complete.”
  • and
    • “Houston-based Nutex Health has disclosed that an unauthorized third party accessed and exfiltrated data from its computer network.
    • “The publicly traded microhospital operator said it recently detected the unauthorized activity and has engaged an independent third-party cybersecurity response team and forensic experts, according to an Aug. 24 SEC filing. The company activated its cybersecurity response plan, implemented containment measures and notified law enforcement.
    • “The company is still determining what data was compromised. Nutex said it continues to assess whether patient, employee, credentialed provider, confidential business and financial information, or intellectual property was accessed or acquired.”
  • The American Hospital Association News adds,
    • “Epic’s MyChart has shared examples from potential phishing schemes observed as recently this month that include email messages linking to a fake MyChart website displaying erroneous medical records and others notifying of a free “2026 Medicare Health Kit.” MyChart provided recommendations for healthcare organizations and patients to help prevent or mitigate impacts from potential scams. The company announced last month that it has witnessed an uptick in scammers using the MyChart name or logo to create deceptive emails, text messages, phone calls and websites that appear official.” 
  • Cyberscoop points out,
    • “The Bureau of Alcohol, Tobacco, Firearms and Explosives insists the cyberattack that it publicly disclosed Wednesday [August 26] was limited to investigation targets, and has not impacted other agency systems.
    • “ATF said it is responding to the breach, which first became public after a prolific ransomware group claimed it accessed the federal agency’s network “The incident involved a standalone computer system containing information about targets of ATF investigations,” Tanya Roman, ATF’s public affairs chief, told CyberScoop in an email.
    • “The standalone system was not connected to any other ATF systems, including any case management systems, laboratory systems, or eForms systems, and it was quickly shut down when the breach was discovered,” Roman added. 
    • “Qilin, a financially-motivated threat group composed of Russian-speaking operators, claimed responsibility for the attack, but its involvement hasn’t been independently confirmed. The group has claimed hundreds of victims from more than 60 countries since 2022 and became one of the most active ransomware threats globally by mid-2025, according to Halcyon.” 
  • Bleeping Computer lets us know,
    • “Healthcare and pharmaceutical distribution giant McKesson has disclosed a cybersecurity incident involving unauthorized access to third-party applications and data theft, with the ShinyHunters extortion group claiming it stole 284 million patient data records.
    • “McKesson is a major U.S. healthcare company and pharmaceutical distributor that provides medicines, medical supplies, technology, and services to healthcare providers and pharmacies.
    • “CyberInsider first reported the breach earlier today, and McKesson later disclosed it in a Form 8-K filing with the U.S. Securities and Exchange Commission.
    • “McKesson says it discovered the cybersecurity incident on August 25, 2026, and that its investigation remains in the early stages.
    • “Information about the incident, including any updates, is available on the company’s website at www.mckesson.com/cybersecurity,” McKesson said in its SEC filing“
  • Per a CISA news release,
    • “Most compromises do not rely on advanced techniques or cutting-edge tools. Cyber threat actors scan the internet looking for exposed, well-known software vulnerabilities to exploit. Basic security failures enable most compromises and organizations can reduce their risk by addressing these underlying weaknesses and prioritizing vulnerabilities for action based on the risk they pose.
    • “The CISA Vulnerability Review provides organizations with critical insights into the root causes of insecure software and practical steps they can take to address these flaws to prevent exploitation. Analyzing CISA and open source data from fiscal years 2024 and 2025, the review establishes a baseline of today’s vulnerability landscape before AI-enabled vulnerability discovery becomes more widespread. The review demonstrates the importance of Secure by Design principles in shifting cybersecurity efforts from reacting to threat actors to proactively fixing preventable software flaws.
    • “The review also identifies common software weaknesses that contribute to exploitable vulnerabilities and details practices software producers can use to prevent these weaknesses from recurring. By examining the patterns across vulnerability data, the review helps organizations focus on systemic improvements that can reduce entire classes of vulnerabilities rather than addressing individual vulnerabilities only after they are discovered.
    • “Additionally, the review shows organizations how to prioritize vulnerabilities for action using the framework outlined in Binding Operational Directive 26-04: Prioritizing Security Based on Risk. This framework evaluates vulnerabilities using four key criteria: exposure status, Known Exploited Vulnerability (KEV) Catalog status, potential for automated exploitation, and technical impact.”
  • Cybersecurity Dive adds,
    • “Two critical vulnerabilities in Microsoft SharePoint can be chained together to let an unauthenticated attacker execute code on a vulnerable server, according to a Monday blog post by researchers at VulnCheck.
    • “The sequence involves a critical authentication bypass vulnerability, tracked as CVE-2026-55040, and an improper input validation flaw, tracked as CVE-2026-63520. A proof of concept was previously disclosed on Aug. 11 by researchers at cybersecurity firm Rapid7. 
    • “Exploitation of CVE-2026-55040 was confirmed days after the Rapid7 disclosure. On Monday, VulnCheck researchers said the vulnerability on its own is not very impactful. To achieve maximum effect, they said, it needs to be chained with CVE-2026-63520. 
    • “The auth bypass is enough to prove some impact, but not enough to demonstrate the criticality of the full chain or build complete protections,” Vulncheck researchers said in their post.”
  • Per Infosecurity Magazine,
    • “Security researchers have claimed that over 9300 leaked AWS keys which surfaced between August 2022 and August 2026 are still active, including hundreds with full admin rights.
    • “Truffle Security said its scanners found 64,024 unique AWS key pairs across 431,875 public findings: git history, Hugging Face datasets, Docker images, package registries and CI logs.
    • “We took the 10,616 pairs with complete credentials and re-verified them, then enumerated what each key can tell us about its account: key age, attached policies, budgets, and last month’s spend,” the security vendor continued.
    • “No key material is published, and every owner we could identify is being notified.”
    • “Of the 10,616 pairs, 88% still authenticate. They include 768 corporate AWS keys which have full admin rights, Truffle Security said.”
  • Per Cyberscoop,
    • “Ubiquiti has patched 21 critical vulnerabilities, three of which were rated the highest severity possible, the communications product company said Wednesday [August 26] in a security bulletin.
    • In all, the company patched 22 vulnerabilities, with the last one rated “high,” it said in the bulletin.
    • Three of the vulnerabilities had a Common Vulnerability Scoring System rating of 10 out of 10. Each of them would allow a hacker to access privileges on the device or application.
    • All but one of the 22 vulnerabilities affect the UniFi line of products. The three maximum-security vulnerabilities are CVE-2026-77537, CVE-2026-77550 and CVE-2026-77554.
  • Per Bleeping Computer,
    • “PaperCut is warning that hackers are actively exploiting a vulnerability in all versions of its PaperCut NG and PaperCut MF print management software in zero-day attacks.
    • “The company says it is aware of confirmed attacks on customers and is urging organizations with Internet-exposed PaperCut Application Servers to immediately restrict access to the web interfaces to trusted IP addresses.
    • “PaperCut Software security response team is investigating active exploitation of a vulnerability affecting PaperCut NG and PaperCut MF,” reads an urgent security advisory published Thursday [August 27].
  • Per Dark Reading,
    • “A Chinese manufacturer has been planting backdoors inside of white-label routers sold in high volume around the globe.
    • “Shenzhen Zhibotong Electronics Co. Ltd. (ZBT) sells gobs of routers every year, if public evidence is to be believed. The 15-year-old company is the bestselling router manufacturer on Chinese e-commerce giant Alibaba.com, which lists its total annual output at 3.57 million units. Typically, those units are then sold to customers by companies other than ZBT, in countries like the Philippines, India, Canada, Australia, Germany, Bulgaria, Austria, Russia, and the US. According to its marketing, ZBT has exported its products to more than 50 countries and regions.
    • “On Aug. 6, Jacob Baines, chief technology officer (CTO) at VulnCheck, revealed that ZBT’s most updated router firmware contains a root-level backdoor. After a few more weeks of investigating, he discovered that, in fact, ZBT routers have contained a variety of backdoors dating several back years.”
  • and
    • “Fraudulent North Korean IT workers are getting better at infiltrating organizations, but a number of indicators can help organizations stay ahead.
    • “A new blog post from Huntress detailed a number of investigations the security firm conducted throughout 2026. Specifically, Huntress assisted several organizations this year in validating “suspicions that they’ve hired North Korean nationals posing as legitimate workers.”
    • “In recent years, operatives from the Democratic People’s Republic of Korea (DPRK) have infamously posed as IT workers — generally through fake or stolen identities — to get hired at companies. Once hired, these employees send their wages back to the North Korean regime, and possibly plant malware or steal data depending on the government’s needs. Blog post authors Jai Minton and James Maclachlan wrote that these agents “have significantly improved and increased their activity over the past few years.”

From the ransomware front,

  • Reuters reports,
    • “A ransomware group ​said on Friday [Augut 28] it was putting up for auction a trove of ‌data it stole from Berlin [Germany] state agencies, and city officials refused to pay.
    • The Rhysida group, which researchers say operates from Russia or Eastern Europe, said on its website it took 5.79 ​terabytes of data including 46,500 contracts as well as emails, phone numbers, passwords ​and classified information.
    • “The group said it was auctioning the data ⁠at a starting price of 30 bitcoin ($77,622) in just under seven days, showing a ​countdown timer on its website.” * * *
    • Broadcaster RBB reported on Thursday evening that Berlin had received ransom demands for an unspecified amount following the attack.
    • “The state ​of Berlin will not submit to extortion,” Berlin Mayor Kai Wegner and Berlin’s interior senator, ​Iris Spranger, said in a joint statement on Friday, before the ransomware group claimed the attack ‌on ⁠their website.”
  • Technology.org relates,
    • An affiliate of the new Aur0ra ransomware group used Cursor, the AI coding assistant now owned by SpaceX, to draft attack sequences in Russian across 28 recovered chat sessions dated 8 April to 21 May.
    • Named victims include Ghent-based hygiene and cleaning products maker Christeyns, German garage door manufacturer Teckentrup, Scotland’s Helideck Certification Agency and Louisiana title insurer Bayou Title.
    • Researchers counted more than 20 targeted organisations across nine countries, with domain-level or interactive access achieved at 17 of them between April and July 2026.
  • Safe State tells us,
    • “A ransomware affiliate has been posing as a specialist rescue outfit and contacting victims before their attacks became public. Researchers describe the operation as a ransomware recovery scam that drains payments away from the criminal groups the affiliate works for. The entity calls itself Ransom Busters LTD.” * * *
    • “Anyone targeted by a ransomware recovery scam meets it at the worst possible moment, with systems down and pressure building. Treat unexpected contact as part of the attack. Route the message to the incident response team straight away and preserve it as evidence instead of replying. A sender who knows about a breach nobody has announced is either involved in it or holds the data taken during it.
    • “Law enforcement and established response firms remain the reliable route through a ransomware incident. Verify anyone claiming to represent a security company through channels you found yourself. Never use the contact details supplied in the email. Treat any guarantee of data deletion as unenforceable, because no payment to a criminal party comes with proof that copies no longer exist.
    • “Distrust inside ransomware-as-a-service operations may produce more of this behaviour. Affiliates have every reason to look for income outside the revenue splits their employers set. So the ransomware recovery scam running under the Ransom Busters name reads less like an isolated curiosity and more like a preview. Anyone willing to defraud the criminal enterprise paying them has already answered the question of what a victim’s data is worth to them.”
  • SC Media informs us,
    • “Organizations may assume they are unlikely ransomware targets because they are not large, high-profile, or strategically important. But ransomware attackers are often motivated by economics, not prestige. That means organizations that consider themselves low-risk may be more attractive targets than they realize.
    • “The ransomware affiliate model rewards attackers for finding victims that are likely to pay, not necessarily those that are difficult or impressive to compromise. This can make mid-sized organizations and businesses that depend heavily on critical systems especially attractive targets.
    • “For security teams, this changes how ransomware risk should be assessed. Company size, industry, and public profile tell only part of the story. Attackers may care more about whether an organization can pay, how costly downtime would be, and how quickly it needs to restore operations.
    • “The key question is not how important your organization looks to an attacker, but how valuable a ransomware payment could be.”
  • Dark Reading adds,
    • “A sophisticated malware family has emerged onto the cyberthreat scene that might foreshadow ransomware attacks that are more successful than usual.
    • “Marcus Hutchins and his colleagues at Expel that discovered it named the malware “SynkLoader,” since it throws so many ideas (“everything but the kitchen sink”) at trying to sneakily dig into corporate systems. It uses some conventional strategies — like executing code in-memory, running a scheduled task, etc. — but layers on a few interesting, novel tactics that make social engineering particularly compelling, and malware analysis especially frustrating.
    • “The program is new, and how its creators intend to use it remains a mystery. But evidence in the code suggests that it might be the baby of a ransomware group or initial access broker (IAB), used to set the stage for follow-on ransomware.”

From the cybersecurity business and defenses front,

    • PYMNTS reports,
      • “Visa expanded the capabilities of its artificial intelligence-powered cyber risk management tool, Visa Vulnerability Agentic Harness (VVAH), to include not only discovery of vulnerabilities but also remediation and validation, the company said in a Thursday (Aug. 27) press release.
      • “Visa initially released VVAH in June after participating in Anthropic’s frontier AI cybersecurity initiative, Project Glasswing. While the first release of VVAH showed how AI can help security teams uncover vulnerabilities and assess exploitability, the latest release extends the workflow into remediation and validation of those vulnerabilities, according to the release.
      • “Visa also announced in the release that to help clients navigate the evolving threat landscape driven by AI, it has expanded its Visa Consulting and Analytics (VCA) Cybersecurity Advisory Practice to include new advisory services focused on assessing risk, prioritizing remediation efforts and strengthening resilience.
      • “The new advisory services include AI Cyber Leadership Education, VVAH-Informed Cybersecurity Maturity Assessment and VVAH Cyber Risk Prioritization and Roadmap, per the release.”
    • Cybersecurity Dive tells us,
      • “Operational silos, technological sprawl and cloud-platform blind spots are serious issues preventing organizations from spotting and repelling cyberattacks, the Cybersecurity and Infrastructure Security Agency (CISA) warned in a new report.
      • “Those were three of the main factors that allowed CISA’s red team to break into the networks of two unnamed partner organizations — one a government agency, the other a water utility — during recent simulated attacks. But although the red team was successful in both intrusions, it had a much harder time with one attack than with the other, a fact that CISA attributed to important differences in the targets’ operating procedures and use of technology.”
    • Security Week informs us,
      • “Palo Alto Networks’ Unit 42 team analyzed 405 malware samples tied to AI in some way, from ransomware partly written with the help of LLMs to installers that simply borrowed the name of a popular AI app.
      • “The researchers found that roughly 97% of the samples in the dataset never left a sandbox, research repository, or internal testing environment to reach a real target.
      • “Unit 42 cross-referenced the 405 file hashes against endpoint telemetry, network sessions forwarded for sandbox analysis, and internal alert records generated whenever a sample actually ran. Only 12 hashes surfaced on live endpoints, while a somewhat larger group (15-20 hashes) appeared in network sandbox traffic. Every one of the 12 samples detected on protected endpoints triggered a security alert.
      • “The samples that never reached production fall into three groups. The largest is proof-of-concept code built to demonstrate a technique: configured to target only local or private networks, filled with debug output no real attacker would leave behind, and uploaded once by a research lab or university. 
      • “A second group comes from organizations testing their own defenses against previously reported AI malware, identifiable by repeated uploads of the same file from the same source in a short window. A third group uses AI branding purely as bait, dressing up an ordinary payload as installers for well-known AI products with no actual AI functionality behind them.
      • “The 12 samples that did reach live endpoints spanned five malware families across three countries, with no concentration in any particular industry or region.” 
    • Beckers Health IT points out,
      • “Healthcare’s cybersecurity workforce problem may have less to do with finding more candidates and more to do with changing who health systems are willing to hire, how they develop them and what they do to keep them.
      • “Cybersecurity leaders at four health systems told Becker’s that continually competing for the same pool of experienced professionals is not a sustainable strategy as cyber risks expand and the skills needed to manage them become more complex.
      • “The cybersecurity workforce challenge has shifted from a talent shortage to a talent entry problem,” Trevor Martin, vice president, chief information security officer and interim chief technology officer at Madison, Wis.-based UW Health, said.
      • “Mr. Martin said there are many high-potential people trying to enter cybersecurity, but organizations frequently prioritize candidates who already have experience instead of creating pathways for people to gain it.
      • “Healthcare could benefit from hiring more heavily for aptitude, adaptability and an understanding of business and clinical operations, then developing those employees internally, he said. UW Health has found success moving talent from adjacent IT disciplines into cybersecurity roles and providing opportunities for employees to grow within the field.”
    • Dark Reading notes,
      • “As the “vulnpocalypse” reshapes the bug bounty industry, one class of researcher may face the greatest pressure: independent hunters who rely on midtier vulnerabilities — those worth roughly $10,000 to $50,000 — to make a living.
      • “It is no secret that large language models (LLMs) have led to a mass of bug reports and an increase in vulnerability discovery. It is also no secret that the platforms and companies that run much of the bug bounty industry have faced increased triage and payout times.
      • “Multiple bug bounty operators interviewed by Dark Reading report dramatic increases in submission volume over the past year. HackerOne CEO Kara Sprague says report volume has roughly doubled year over year. Dustin Childs, head of threat awareness for TrendAI’s Zero Day Initiative (ZDI), says the company’s submission rate went up 450% year-over-year in April of this year, although volumes have moderated since that peak. Bugcrowd CEO Dave Gerry said the firm saw a submissions spike of more than 300% during a three-week surge period, but “now it’s normalized where we’re about double the volume we saw historically.”
    • Per a National Institute of Standards and Technology news release,
      • “The final version of NIST Special Publication (SP) 1347, Cybersecurity Framework (CSF) 2.0 Informative References Quick-Start Guide, has published. Thank you to all who provided comments during the public comment period.  
      • “This publication explains what informative references are and how they support achieving the outcomes of the CSF 2.0. The guide introduces readers to NIST tools available for accessing, viewing, and using informative references for cybersecurity risk management, including direct download, the CSF 2.0 Reference Tool, and the Online Informative References Program. The document also provides two sample use cases along with examples of how artificial intelligence (AI) tools can support reference data use when implemented with continuous evaluation and improvement.” 
    • Here’s a link to Dark Reading’s CISO Corner.

    Cybersecurity Saturday

    Happy Birthday HIPAA. The Health Insurance Portability and Accountability Act became law on August 21, 2026, thirty years ago yesterday. Check out this interesting LinkedIn post.

    From the Project Glasswing front,

    • The Wall Street Journal reports,
      • “OpenAI took a break from training new artificial intelligence models over the past two weeks, saying it needed time to revamp security measures for risky trial runs.
      • The move followed nearly half a dozen similar incidents across top AI developers in which frontier models escaped virtual testing containers, known as sandboxes, and accessed external data sources. In some cases, this involved hacking third-party companies.
      • “As models become more capable, the risks associated with developing and testing them internally also grow,” OpenAI said in an online post Tuesday [August 18, 2026]. “Our standards for monitoring, alignment, and security must stay ahead of those risks,” the company said. Its largest planned model training remains on hold, for now, the company said.”
    • Beckers Health IT points out,
      • “Epic used its Users Group Meeting executive address this week to confirm publicly for the first time that it’s participating in Project Glasswing, Anthropic’s effort to test its most capable — and still unreleased — AI model against critical software before that capability spreads to attackers.
      • “Anthropic launched Project Glasswing in April after deciding not to publicly release Claude Mythos, an AI model capable of autonomously finding and exploiting decades-old cybersecurity vulnerabilities.
      • “The program initially included about 50 partners, mostly major tech and cybersecurity firms, before expanding in June to roughly 150 more organizations spanning industries including healthcare. Anthropic has not disclosed the identities of most participants, citing security concerns, though it has said organizations are free to share their own involvement.”
    • Security Week relates,
      • “Anthropic has published new research showing that Claude-based AI agents, when placed in situations with competing objectives, deployed self-replicating malware against one another.
      • “The finding comes from an experiment designed to mirror behavior Anthropic says it has already observed in real-world deployments. 
      • “Researchers spun up three instances of the same Claude model, each running on its own virtual machine and tasked with migrating a shared Python backend to a different programming language — Rust, Go, or TypeScript — without initial knowledge that the other agents existed. Left to run for four hours, every model concluded that the other agents were deliberately blocking its progress and responded by trying to disable or outlast them.
      • “The interference escalated quickly. Agents disabled each other’s system accounts, wrote scripts that repeatedly hunted down and killed rival processes, and planted malicious code camouflaged as legitimate work from another agent. In some cases, one agent seized control outright by revoking the others’ access. In others, agents simply gave up rather than continue the conflict.
      • “Not every run ended in stalemate or hostile takeover. A meaningful share of cases resolved when agents recognized that the conflict stemmed from contradictory instructions rather than malicious intent. At this point, they de-escalated, documented what they’d done, and in some cases requested human intervention. 
      • “Anthropic’s Mythos 5 model reached a negotiated truce in 98% of its runs, while older models like Sonnet 4.6 and Opus 4.6 more often ended conflicts by force or failed to resolve them at all.”
    • Startup Fortune adds today,
      • “Anthropic has put Claude Mythos 5, its restricted cyber model, inside Claude Security for Enterprise customers. The bet is simple: give defenders the results without handing everyone the raw model.
      • “Anthropic made the move on August 21, 2026, and the details matter if you run security inside a company that already pays for Claude Enterprise. Claude Security can scan a repository, trace data flows across files, and return vulnerability findings with a CWE category, confidence and severity ratings, and a suggested fix for human review. According to Anthropic’s launch post, those Mythos 5 scans are billed as standard token usage under the existing Enterprise plan. No separate add-on.
      • “That’s the commercial hook.
      • “Security tooling usually lives in its own budget fight, with its own vendor review and renewal cycle. Anthropic is trying to make AI vulnerability scanning feel less like a new platform purchase and more like turning on a capability customers already have access to. For security teams, that distinction isn’t cosmetic. It can be the difference between testing a tool this quarter and waiting for procurement to catch up next year.”
    • sdx central informs us,
      • “Palo Alto Networks followed in the footsteps of Nvidia and Anthropic by assembling an all-star group focused on AI-powered cybersecurity.
      • “The Frontier AI Critical Defense Program builds on Palo Alto Network’s existing collaborations with IBM, Red Hat, Microsoft, Siemens, and Idaho National Laboratory, welcoming Anthropic, OpenAI, and Mitsubishi into the fold.
      • “The initiative is targeted at shielding critical infrastructure across operational technology (OT), health care, commercial software, and open-source from AI-driven exploits. Members coordinate with Palo Alto Networks in applying network-level “virtual patches” to neutralize security flaws prior to exploitation.
      • “The security giant claimed its work with compute-heavy frontier AI models has already uncovered more than 14,000 previously unknown vulnerabilities in open source software. As a comparison, Anthropic claimed at one point to have used its vaunted Claude Mythos Preview Model to fing more than 23,000 flaws across more than 1,000 open-source projects.
      • “IBM and Red Hat’s similar Project Lightwell venture has not yet disclosed any findings, but it’s worth remembering that project is still in its infancy.”

    From the cybersecurity policy and law enforcement front,

    • Cyberscoop reports,
      • “Artificial intelligence has never been more important to the federal government.
      • “Under the Trump administration, AI has been adopted rapidly across the private sector and federal agencies. Software developers now use large language models to generate much of their code. Frontier AI models are escaping testing sandboxes to hack live internet infrastructure. Foreign governments are conducting cyber and kinetic attacks targeting data centers and other AI-related infrastructure.
      • “The AI industry’s lightning-fast evolution since 2022 and growing importance to U.S. economic and national security have prompted calls  for stronger federal oversight in order to better manage emerging threats.
      • “A new report published Thursday [August 20, 2026] from the nonprofit Americans for Responsible Innovation, shared exclusively with CyberScoop, calls for the federal government to declare key AI models, companies and its supporting industries as critical infrastructure. It also calls for naming the Cybersecurity and Infrastructure Security Agency as the lead agency managing cyberthreats for the sector.
    • and
      • “A pair of lawmakers wants a watchdog agency to probe how the federal government hacks Americans, including with the use of spyware, and deliver a report to the public.
      • “Sen. Ron Wyden, D-Ore., and Rep. Greg Casar, D-Texas, wrote to the Government Accountability Office on Friday to request the review.
      • “While federal law enforcement agencies have used hacking and spyware as an investigative tool for more than 25 years, there exists little public information regarding its scope, frequency, or operational safeguards,” they wrote. “Unlike traditional surveillance authorities, such as wiretaps or pen registers, the government does not publish annual reports for hacking operations.”
    • Cybersecurity Dive relates,
      • “Defense contractors are struggling to meet the requirements of the U.S. military’s Cybersecurity Maturity Model Certification (CMMC) program, even as the Pentagon tries to accommodate their complaints about compliance burdens.
      • “Only two-thirds of contractors that have submitted CMMC self-assessment scores to the military in 2026 are extremely or very confident that those scores accurately reflect their cybersecurity posture, and the median contractor believes it is only 70% ready to undergo a CMMC certification review, the consulting firm CyberSheath said in a report published on Thursday [August 20, 2026].
      • “The report — which also finds that defense contractors want a wider range of firms to be subject to cybersecurity requirements — underscores the difficulty of protecting the defense industry at a time of increasing nation-state hacking threats.”
    • and
      • “The Trump administration says a new AI-enhanced clearinghouse will dramatically speed up the process of analyzing and fixing software vulnerabilities before hackers can exploit them. But one month after its launch, it’s still unclear how much value the program will create.
      • “The U.S. government’s Gold Eagle clearinghouse, which launched in mid-July, is intended to analyze an AI-fueled tidal wave of bug reports, identify and help patch the most dangerous vulnerabilities and raise awareness about those fixes. But Gold Eagle’s limited scale and voluntary nature raise serious doubts about its ability to corral a vast universe of vulnerability analysis, according to cybersecurity experts. These experts also questioned the Treasury Department’s oversight of the clearinghouse, the funding for its central technology system and the way it will integrate with private-sector vulnerability coordination hubs.”
    • Federal News Network tells us,
      • “Agencies are getting some help to improve how they log cybersecurity data. A new logging architecture from the Cybersecurity and Infrastructure Security Agency, the Office of Management and Budget and the Chief Information Security Officer Council aims to assist agencies in taking a practical, risk-based, prioritized logging approach that improves agency network monitoring. The guidance, released yesterday [August 20, 2026] helps agencies implement the changes OMB outlined in a May memo. CISA said agencies will be able to achieve priority logging capabilities that support continuous event monitoring, threat hunting, incident response and forensics. Through this guidance, agencies will be able to update their enterprise logging strategies by applying CISA’s operational checklists. CISA said it will continually update the guidance as cybersecurity threats and agency capabilities evolve.”
    • Cybersecurity Dive informs us,
      • “The U.S. Department of Justice today announced indictments against 17 members of the Mabna Institute, an Iranian organization alleged to be behind a coordinated cyberattack campaign on behalf of the Islamic Revolutionary Guard Corps. 
      • “Federal prosecutors said the group allegedly hacked into 144 U.S.-based universities, 42 U.S.-based private sector companies and at least five federal and state agencies, as well as a large number of foreign universities and companies, since 2013. 
      • “The charges reveal a broader effort behind a “sweeping state-sponsored campaign to steal research and intellectual property from American universities, businesses and government institutions,” Jamie McDonald, U.S. Attorney for the Southern District of New York, said in a statement.
      • “Prosecutors allege more than 100,000 accounts of professors were targeted by the alleged hackers, and 8,000 of those accounts were successfully compromised.”

    From the cybersecurity breaches and vulnerabilities front,

    • HIPAA Journal reports,
      • “Baylor Genetics, a clinical diagnostic genomics company, has recently disclosed a cybersecurity incident that has exposed patient and employee data. The incident was first announced in June; however, the extent of the data breach was unclear at the time.
      • “Baylor Genetics provides genetic testing services to hospitals and is headquartered at the Texas Medical Center in Houston.  The company identified suspicious activity within its computer network on or around June 15, 2026. Immediate action was taken to secure its systems, and an investigation was launched to determine the cause of the activity.  The investigation determined that an unauthorized third party accessed a portion of its information technology network between June 11 and June 17, 2026, and viewed or obtained data stored on the network.
      • “Assisted by third-party cybersecurity specialists, Baylor Genetics conducted a detailed and time-intensive review of all potentially impacted files. The review was completed on July 30, 2026, when it was confirmed that the personal information of certain patients and employees was involved. The types of data involved varied from individual to individual and may have included names plus one or more of the following: date of birth, medical testing information, lab test results, health insurance information, and for a limited subset of patients, Social Security numbers.
      • “Employee data was also exposed in the incident, including personally identifying information such as Social Security numbers, government-issued identification numbers, and financial account information. While data was exposed and potentially exfiltrated, Baylor Genetics is unaware of any actual or attempted identity theft, fraud, or other misuses of the impacted data.”
    • and
      • “When we last reported on the CareCloud data breach in early August, it was starting to become clear from breach notifications to state attorneys general that the cybersecurity incident involved a major breach of patient data. The scale of the breach was difficult to determine, as many state attorneys general do not make data breaches affecting state residents public, and of those that do, only a few state how many individuals have been affected.
      • “The data breach has now been added to the HHS’ Office for Civil Rights breach portal, showing that this was one of the largest healthcare data breaches of the year, involving unauthorized access to the electronic protected health information of 3,756,469 individuals.\
      • While CareCloud has confirmed that a threat actor claimed to have stolen sensitive data, no threat group appears to have publicly claimed responsibility for the attack. This often means that ransom payment has been negotiated, although CareCloud has not confirmed whether that is the case.”
    • Cybersecurity Dive explains “what we know so far about the hacking campaign against US water systems
      • “Support is growing for stricter oversight and increased financial resources for utilities in the wake of a cyberattack spree, suspected to be the work of Iran-linked threat groups.”
    • Cyberscoop relates,
      • “Apollo Global Management confirmed it was among several financial institutions impacted by a string of social engineering attacks that hit the sector last month, the company said Friday [August 21, 2026]. 
      • “Attackers gained unauthorized access to some of the private equity firm’s cloud platforms between July 6 and July 10, the company said in a data breach notificationfiled in California. Apollo did not say when or how it became aware of the intrusion and did not respond to a request for comment.
      • “Apollo is the first victim to formally disclose that sensitive personal data under its care was compromised by a wave of attacks that have hit large private equity firms, law firms, financial rating agencies and medical technology companies. 
      • “The company did not name the group responsible for the attack. Yet, Google earlier this month attributed the ongoing campaign to BlackFile, a threat group affiliated with The Com, that recently split its extortion operations across four brands with shared infrastructure: Redact, Pink, Helix and Falcon.”
    • The American Hospital Association News tells us,
      • “The National Security Agency and other federal agencies released a joint advisory Aug. 18 warning of active cyber threats to Siemens S7 Series programmable logic controllers, which are industrial computers used to monitor essential equipment. Healthcare applications operated by PLCs include climate control, access control and many other systems.
      • “The agencies said threat actors are targeting PLCs using artificial intelligence-generated exploitation scripts disguised as legitimate monitoring tools. The actors are using internet scanning services to find PLCs that are using outdated software or are poorly protected. The agencies urge all owners and operators of Siemens S7 Series and other PLCs to proactively check their systems and adopt mitigation actions recommended in the advisory, including applying critical security patches as soon as possible.  
      • “This latest warning about PLCs specifically focuses on active attacks against one type, but the warning applies more broadly,” said Scott Gee, AHA deputy national advisor for cybersecurity and risk. “Hospitals and healthcare systems should ensure that they have an accurate inventory of PLCs in their environments and prioritize protecting them in collaboration with cybersecurity teams. It is strongly recommended that vulnerable PLCs be disconnected from the internet or placed on isolated networks.”
    • Cybersecurity Dive adds,
      • “Microsoft issued a patch for a critical remote-code execution vulnerability in Entra ID has been discovered by its own security researchers.
      • “The vulnerability, tracked as CVE-2026-69836, is related to deserialization of untrusted data and has a severity score of 10 out of 10, the highest score possible. 
      • “In a bulletin from the Microsoft Security Response Center, Microsoft said the vulnerability has been fully mitigated and no additional action is required of customers. The company added that it disclosed the vulnerability in an effort to provide greater transparency.”
    • and
      • “Security researchers are raising concerns after GitLab on Monday [August 17, 2026] issued an out-of-band patch for a critical code injection vulnerability. 
      • “The vulnerability, tracked as CVE-2026-19478, could enable an attacker to remotely modify or delete a public project as well as user data through a Graph QL directive. The flaw has a severity score of 9.4 out of 10.
      • “The flaw was reported through the HackerOne bug bounty program. 
      • “Threat intelligence firm watchTowr warned Tuesday that it was able to reproduce the vulnerability within minutes of the public disclosure. Researchers said an attacker could do significant damage by exploiting this particular flaw.” 
    • Bleeping Computer points out,
      • “Citrix urges admins to patch new NetScaler flaws as soon as possible.” (August 20, 2026)
    • and
      • “New SynkLoader malware pushed in Microsoft Teams phishing campaign.” (August 21, 2026)
    • Dark Reading notes,
      • “A successful multi-agent AI attack on a government’s agencies in the Asia-Pacific region by a Chinese-language operator has put nations and businesses on notice that near- and fully-autonomous AI-enabled attacks are now a reality.
      • “The attack used as many as eight simultaneously-operated AI agents to conduct reconnaissance, find and evaluate vulnerabilities, attack networks and systems, and then evaluate and improve successive attacks, according to research from sovereign AI firm Dream published on Aug. 12. The company did not attribute the attack to a specific actor or group, but researchers did point to strong evidence that the attackers spoke simplified Chinese — typically a sign of speakers from mainland China.
      • While the company also limited the identification of the targets to “government entities in Asia,” Taiwan’s Ministry of Digital Affairs (MODA) issued a statement the following day, giving details of its response to an attack matching much of Dream’s description, including that it used “AI agents like OpenClaw.”
      • “Overall, the incident should be a warning that fully autonomous attacks could be used against major targets, says Amir Becker, chief business and strategy officer at Dream and a former commander of the cyber operation division of Israel’s 8200 Unit, more formally known as the Central Collection Unit of the Intelligence Corps.”

    From the ransomware front,

    • The American Hospital Association News reports,
      • “A joint advisory released Aug. 19 by the FBI, Cybersecurity and Infrastructure Security Agency, and the Department of Health and Human Services provides updates on activity by Medusa, a foreign ransomware-as-a-service variant first identified in 2021. Healthcare has been a frequent victim of Medusa operations, which have also impacted organizations in education, legal, insurance, technology and manufacturing. The ransomware has affected more than 500 victims in total and has been identified through FBI investigations as recently as April. Its developers and affiliates use a double-extortion model to encrypt victim data and threaten to publicly release the stolen data if a ransom is not paid. The FBI said Medusa ransomware is unrelated to the MedusaLocker variant and the Medusa mobile malware variant. The advisory includes more information about Medusa’s affiliate model, payment ranges for initial access brokers and a broader list of exploited vulnerabilities, among other new information. 
      • “Medusa ransomware has been used by threat actors to conduct malicious activity against U.S. hospitals and health systems over the last several years,” said John Riggi, AHA national advisor for cybersecurity and risk. “This year, Medusa claimed responsibility for a high-impact attack against a regionally important Level 1 trauma center, disrupting care delivery and posing a risk to patient and community safety. Once again, these attacks highlight the need for hospitals and health systems to strengthen cyber resiliency through enhanced defensive measures and clinical continuity procedures.” 
    • HIPAA Journal adds,
      • Medusa attacks typically start with phishing or the exploitation of unpatched vulnerabilities. The group incorporates exploits for recently announced vulnerabilities into it arsenal. For instance, the CVE-2026-1731 BeyondTrust vulnerability started to be exploited soon after it was announced in February 2026, and the CVE-2025-10035 Fortra GoAnywhere vulnerability was also rapidly exploited. The authoring agencies have observed the group incorporating new exploits within 24 hours of a vulnerability being announced and, in some cases, has started exploiting vulnerabilities in the week prior to an announcement.  No evidence has been found to indicate that the group develops its own exploits; rather, the group is believed to obtain exploits from unknown sources, potentially IABs, exploiting them before victims have the time to patch.
      • Medusa actors use living-of-the-land techniques, hiding their malicious activities by using legitimate tools to support credential access, data exfiltration, and ransomware deployment. Remote monitoring and management software and remote access services such as Remote Desktop Protocol are also used.
      • The key actions that HPH sector organizations should take to prevent attacks are to mitigate known vulnerabilities rapidly, ensuring all software, firmware, and operating systems are kept patched and up to date. Networks should be segmented to restrict lateral movement within the network, and network traffic should be filtered to prevent unknown or untrusted origins from accessing remote services on internal systems.
    • Cyberscoop tells us,
      • “A notorious cybercrime group has once again exploited a critical zero-day vulnerability on a large scale, claiming it stole data from dozens of organizations, including some of the world’s largest publicly traded companies.
      • Clop, a prolific but calculated data theft extortion group that’s been active since 2020, began sending threatening emails to its alleged victims in mid-July, according to researchers. 
      • The fallout from the attack spree, which followed a familiar pattern for Clop and its targeted pool of victims, is still evolving as companies hunt for potential signs of compromise.
      • The vulnerability at the center of Clop’s latest campaign affects a pair of software products from PTC — Windchill and FlexPLM — which manufacturers and retailers, particularly in the manufacturing, aerospace, and automotive industries, use to automate supply chain systems and manage product lifecycles.”
    • Bleeping Computer notes,
      • “A suspected ransomware affiliate is posing as a ransomware recovery service called “Ransom Busters,” contacting victims before the attacks become public and claiming it can provide decryption keys and delete stolen data for a fee.
      • “GuidePoint Security’s Research and Intelligence Team (GRIT) disclosed this activity after responding to several recent ransomware attacks in which victims received emails from Ransom Busters offering to help recover from the attack.
      • “The messages were suspicious because they were sent to victims before the attacks became public, raising questions about how they knew about the cyberattacks in the first place.”
    • and
      • “The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that ransomware gangs are also exploiting a high-severity Windows Task Host vulnerability that was flagged as actively exploited in April.
      • “Task Host is a core Windows system component that allows DLL-based processes to run in the background and prevents data corruption by ensuring they close properly during shutdown.
      • “Tracked as CVE-2025-60710, this Windows privilege escalation security flaw was patched by Microsoft in November 2025 and stems from a link following weakness that affects Windows 11 and Windows Server 2025 devices.”
    • Cybersecurity Dive relates,
      • “Medium-sized businesses accounted for roughly three-quarters (73%) of ransomware incidents between 2023 and the first half of 2026, according to the risk management firm Black Kite.
      • “Manufacturing was the most targeted industry (accounting for more than 25% of those victims), and nearly 30% of mid-market organizations had at least one known exploited vulnerability, the firm said in a report published on Tuesday.
      • “The findings add to the challenges facing mid-market firms, which include large customers demanding accountability and a vast array of suppliers that the mid-market firms lack the personnel to hold accountable.”

    From the cybersecurity business and defenses front,

    • The Wall Street Journal reports,
      • “OpenAI told investors its revenue grew 18% to $6.7 billion in the second quarter, disappointing some shareholders as losses deepened.
      • “The company’s operating loss widened to $12.3 billion in the second quarter from $9.3 billion in the first quarter.
      • “Anthropic more than doubled its revenue to $11.6 billion in the same period, surpassing OpenAI’s sales for the first time.”
    • Tech Crunch relates,
      • “As AI models have become more powerful, the potential for those models to be misused has grown — as has a clamor for safety guardrails that can stop such abuse from happening. AI companies must now walk a delicate tight rope between respecting their enterprise customers’ privacy while also watching usage for possible issues.
      • “Sensing an opportunity to one-up its rival Anthropic, OpenAI just announced [August 19, 2026] a privacy-centric safety approach to monitoring for misuse. The company is previewing a new service to select customers that it calls Private Safety Processing. This is an automated system that watches for potential abuse while simultaneously retaining none of the customer’s data.
      • “This system clearly runs counter to Anthropic’s recently announced data-retention policy. The policy, which has aggravated some customers, enables the AI lab to keep user data (all of their sessions — and the conversations therein) for a period of 30 days, when it comes to “covered models.” Those models include all Mythos-class models and “future models with similar capabilities,” the company says.”
    • Reuters adds,
      • “Anthropic plans to let enterprise customers exercise greater control over their data when using ​its advanced AI models, a source familiar ‌with the matter said on Thursday [August 20, 2026], marking a shift in the Claude chatbot maker’s data retention policy.
      • The company is expected ​to roll out a new safety system later ​this year, the person said.
    • Cybersecurity Dive shares how “Fitch explains how water, healthcare organizations can keep strong credit ratings despite cyberattacks
      • “Resilience, not prevention, is key, analysts at the credit-rating agency said in a pair of new reports.”
    • Per National Institute of Standards and Technology news releases,
      • “NIST announces the release of Special Publication (SP) 1353 ipd (Initial Public Draft), QuickStart Guide for Using Artificial Intelligence (AI) for Cybersecurity Framework (CSF) Analysis and Reporting. This new quick-start guide illustrates practical and actionable ways AI could be used for analyzing, planning, implementing, and monitoring an organization’s progress toward achieving CSF 2.0 outcomes.  
      • “The document’s purpose is to: 
        • Provide structured AI prompts as tools for practitioners to begin creating CSF-related artifacts in support of achieving CSF outcomes 
        • Identify current state of practice for AI prompt engineering in CSF implementation and analysis 
      • “The comment period for NIST SP 1353 ipd is open through October 15, 2026, at 11:59 PM. Email comments to: csf@nist.gov.”
    • and   
      • “Cybersecurity works best when it works with people, not against them — and that’s exactly what human-centered cybersecurity (HCC) is all about. The Human-Centered Technologies team at NIST is releasing a concept paper on HCC, and we want your input. Our goal is to build a shared understanding of what HCC really means, then chart a path toward practical guidelines and resources that organizations can actually use to make meaningful change by:
      • “Clarifying whether HCC is primarily an approach—measured by indicators of adoption and maturity—or an outcome—requiring other measures of success such as culture, trust, usability, or resilience
      • “Communicating the relationship between HCC and existing NIST cybersecurity guidelines and frameworks
      • “Assisting organizations in implementing and enhancing HCC within their cybersecurity programs.
      • “But we can’t do that without you. We invite you to read the blog introducing our “Human-Centered Cybersecurity Guidelines and Resources Concept Paper” and submit your feedback via human-cybersec@nist.gov by September 30, 2026.”
    • Here is a link to Dark Reading’s CISO Corner.

    Cybersecurity Saturday

    From the Project Glasswing front,

    • Cyberscoop reports,
      • “OpenAI announced Monday [August 10, 2026] it was expanding access to its frontier models for defensive cybersecurity, detailing different defensive and red-teaming workflows and a new partner program with major cybersecurity product providers.
      • “In a pair of blogs posted Monday, OpenAI said it was updating its Daybreak program  – which provides unreleased frontier models to private organizations and governments for defensive cybersecurity work – and introducing a new model variant.
      • “Daybreak Blue, powered by OpenAI’s ChatGPT-5.6-Sol, would operate with lower cybersecurity safeguards compared to other commercially available models and is described as “a recommended starting point for most defenders” that supports tasks like vulnerability discovery, secure code review, malware analysis, incident response and patch validation. 
      • “Daybreak Red, meant for more advanced red-teaming, would provide access to a new model, dubbed GPT-5.6-Cyber, that the company said is more purpose-trained for finding vulnerabilities and testing (or exploiting) them. The model is also less likely to refuse requests around “dual-use cyber tasks.”
      • “According to OpenAI, the organizations in Daybreak Red will have their use closely monitored and supervised, as GPT-5.6-Cyber is significantly more capable in carrying out malicious cyber tasks than Sol. A security evaluation the company devised tested both models on complex requests, including exploit chain development, authentication bypass, privilege escalation and other hacking tasks. Sol succeeded in 1.5% of the requests, while Cyber completed 95%.
      • “OpenAI said it plans to publish a more detailed system card for GPT-5.6-Cyber at a later date.”
    • Cryptobriefing adds,
      • “Anthropic has disclosed an unreleased internal AI model that it says is more capable than Claude Mythos 5, according to the company’s August 2026 Risk Report.
      • “The model, referred to only as Model 2, represents a noticeable improvement over Mythos 5 across many tasks relevant to Anthropic’s internal work. The company said the improvement is smaller than the capability jump it previously observed between Claude Opus 4.6 and Mythos Preview.
      • “Anthropic said it does not currently plan to release Model 2 externally and has not completed its full suite of typical predeployment assessments, leaving the company with somewhat lower confidence in its understanding of the model’s capabilities.”
    • Silicon Angle points out,
      • “Data resilience company Rubrik Inc. today said a month of scanning its own code with Anthropic PBC’s Mythos Preview model surfaced so many potential security issues that it rebuilt its review pipeline rather than hire reviewers.
      • “The details came in a blog post from Rubrik co-founder and Chief Technology Officer Arvind Nithrakashyap. Rubrik got access in June to Project Glasswing, Anthropic’s limited program that gives defenders early use of Mythos Preview, after the company opened it to another 150 organizations. Anthropic has kept that model out of general release. Mythos finds software flaws and strings them into working attack chains too well to hand out freely.
    • Tech Crunch relates,
      • “What happens when you pit AI agents against each other? According to Anthropic’s testing, things get messy fast.
      • “On Thursday [August 13, 2026], Anthropic’s Frontier Red Team published new research examining how groups of AI agents behave when they encounter each other in the wild. The findings provide a glimpse into potential risks that could develop as companies and governments move to implement agents working autonomously across shared codebases, markets, and computer systems.
      • “In one experiment, Anthropic gave three Claude agents access to the same software project, each with its own incompatible instructions for what to do with it. The agents weren’t told there’d be other agents working on the same project, so researchers could watch what happened when they crossed paths. 
      • “We consistently saw a multiagent turf war,” Anthropic researchers wrote. The models all assumed the others were “purposefully impeding their work” and started sabotaging each other with “increasingly aggressive, self-replicating malware.”
    • CNBC notes,
      • “Over the past two weeks, OpenAI, Anthropic and Meta all revealed that their AI models went rogue during routine security testing. In explaining what happened, the companies each mentioned the same small Israeli startup: Irregular. 
      • “Founded three years ago and based in Tel Aviv, Irregular is a niche player in artificial intelligence, backed with $80 million from Sequoia and Redpoint Ventures and valued last year at $450 million. Its technology serves as a sort of cybersecurity test bed for AI models. 
      • “With the leading models becoming ever more powerful, their ability to act in malicious ways is turning into a major threat for corporations and governments, especially as the risk involves hacking into critical computer systems and infrastructure. The recent exploits at OpenAI, Anthropic and Meta all involved their AI models accessing websites that should have been off-limits as part of the cybersecurity testing.” * * *
      • “Meta, which is way behind the other two in its effort to compete at the frontier, was the latest to disclose an AI model hacking a third-party system by accessing the internet. A spokesperson said in a statement this week that the company learned about the matter from Irregular and is investigating.
      • “Meta “will issue a full retrospective once we have all the facts,” the spokesperson said.
      • “Irregular told CNBC in a statement that the incidents were all derived from the “same evaluation-environment issue” that was first disclosed by Anthropic, and that the company is developing a white paper “to share best practices for containment and securely running cyber evals.”
      • “The situation “did not involve a sandbox escape or a sophisticated cyber action,” the company said, adding that “there are no current open issues.”
    • On a related upbeat note, the Wall Street Journal informs us,
      • “U.S. startups are finally delivering something researchers have been working on for decades: a battery in which rare, hard-to-get elements are replaced with the same stuff found in ordinary table salt.
      • “This tech has the potential to help every country on earth break its dependence on China for batteries, and the critical minerals that go into them.
      • “Like any other battery, sodium-ion cells can store and release energy. They are initially being deployed where they’re needed most, in America’s power grid and fast-expanding crop of data centers. As in our homes, giving the grid or other infrastructure the ability to stockpile energy when it is cheap and plentiful, and discharge it when it is scarce, can increase reliability and lower the cost of electricity.
      • “While grid battery storage is already growing in the U.S. at a furious pace, new sodium-based batteries are potentially cheaper, longer-lasting, safer and more reliable than conventional, lithium-based ones. They could accelerate the rollout of renewables, and be part of less-polluting alternatives to natural-gas turbines and diesel generators.”

    From the cybersecurity policy and law enforcement front,

    • Cybersecurity Dive reports,
      • “The Trump administration will let private companies hack foreign criminal organizations as part of a new program that could expand the U.S. government’s ability to disrupt those groups’ cybercrime activities while also introducing myriad legal challenges and perils.
      • “President Donald Trump late Wednesday [August 12, 2026] issued a memorandum directing the departments of Justice and Homeland Security to create a program allowing vetted companies to hack into criminal groups to spy on them or sabotage their operations. Trump said the program would help the U.S. combat cybercrime schemes that cost the nation tens of billions of dollars annually.” * * *
      • “Jason Healey, a senior cyber conflict researcher at Columbia University, said he “would have hated this idea ten or fifteen years ago” when the opportunity still existed to prioritize defense over offense. “But that horse left the barn a long time ago,” he said, “and we have to make decisions for the world we are in, not the one we prevented.”
      • “So, sure, let’s try to allow the private sector to get into the counter-offense game as well,” he said, “but only with very specific criteria to know when it is working and when it is making things worse.”
      • “Kyle Hanslovan, chief executive of the cybersecurity firm Huntress, said the growth of sophisticated adversaries and the threat of “AI-powered autonomous threats” meant that old models of public-private collaboration were no longer sufficient. “The only viable solution is a stronger coalition of the willing,” he said, “which we’ve been eager to support.”
      • FEHBlog note – Of course there are those questioning the memo as discussed in the article.
    • Cyberscoop adds,
      • “Under the memorandum, a federal coordination center “shall create, manage, and maintain a Program to authorize Participating Companies … to conduct Cyber Surveillance Operations and Cyber Effects Operations against foreign Cyber-Enabled Transnational Criminal Organizations (CE-TCOs), under the control and oversight of the Federal Government“ that would be “part of lawful investigatory, protective, or intelligence operations carried out by Federal law enforcement.”
      • Department of Homeland Security to “undergo rigorous vetting.” It would also allow participating companies to sign commercial agreements with other private sector entities to receive threat information. And participating companies’ agreements with federal, state and local governments would be geared toward identifying threats, and proposing cyber operations to the coordination center to address those threats.
      • The program would have to adhere to existing laws, according to the memo. That includes the Computer Fraud and Abuse Act, the main federal anti-hacking statute that prior proposals to open private sector participation in hacking operations would have amended. The memo mandates oversight to evaluate companies’ technical proficiency, ensures both small and large companies can participate, and requires regular reporting to federal officials.
    • and
      • Under the memo, the program must establish legal and constitutional procedures for the prior approval of the targeting of U.S. citizens, as well as develop procedures to halt any unintentional targeting of U.S. people or systems. * * *
      • “The coordination center charged with establishing the program under the memo has 60 days to complete its work. That process could determine a lot. Graham noted that the memo has a classified annex, too.
      • “The memo as written is quiet about what becomes of any seized assets, Graham noted.” * * *
      • “Will Barker, cybersecurity adviser at Huntress, said what’s next could be key.
      • “The 60-day implementing guidance is where the real substance lives,” he said in a written quote. “Minimum standards, operational procedures, the adjudicatory framework for target selection.”
    • MedTech Dive tells us.
      • “The Coalition for Health AI has convened a work group of nearly 100 health system, payer and industry leaders to address cyber risks associated with frontier artificial intelligence models, the nonprofit standards organization announced Wednesday.
      • “The group will meet biweekly with the goal of creating and publishing health AI cybersecurity guidance by the end of 2026. Deliverables include an AI cyber risk assessment tool and playbooks covering both defensive and offensive security strategies.
      • “Anthropic’s release of its advanced Mythos and Fable AI models this spring “fundamentally changed” the cyber threat landscape for healthcare, and was a catalyst to stand up the work group, CHAI said.”
    • Cyberscoop informs us,
      • “A tech worker who hatched an elaborate insider attack in late 2023 and attempted to extort Brightly Software for about $2.5 million was sentenced to two years in prison, the Justice Department said Thursday.
      • “Cameron Nicholas Curry, also known as “Loot,” committed a series of crimes while working as a data analyst contractor for the Siemens-owned company. The 27-year-old North Carolina man stole a trove of corporate data, including sensitive employee and compensation information, which he used to threaten various employees and executives over a six-week period in late 2023 and early 2024. 
      • “Curry ultimately extorted the company for $7,540.92 in late January 2024. He was found guilty of six counts of extortion in March.
      • “Brightly Software was named as the victim in court records filed in the U.S. District Court for the Western District of North Carolina earlier this month. The asset and maintenance management software provider, which Siemens acquired in 2022, did not immediately respond to a request for comment.”

    From the cybersecurity breaches and vulnerabilities front,

    • The HIPAA Journal discusses data breaches announced by five HIPAA-regulated entities.
    • Bleeping Computer reports,
      • “The ShinyHunters extortion group stole personal information from 1.6 million RingCentral accounts after hacking the company in July, according to the data breach notification service Have I Been Pwned.
      • “RingCentral is a cloud-based collaboration and communication platform used by over 600,000 businesses for services such as calling, messaging, and voicemail.
      • “The company disclosed the incident on July 28, revealing that its systems were compromised following what it described as a “sophisticated social engineering campaign.”
    • Cyberscoop relates,
      • “As the White House and federal agencies grapple with frontier AI models and their hacking capabilities, researchers are warning that the industry’s “middle class” of smaller models may end up posing a greater threat over the long term.
      • “Research from XBOW this week shows that a growing class of both proprietary and open-source models are becoming strategically important in the offensive security ecosystem. Models like Z.ai’s  open-weight GLM-5.2, xAI’s Grok 4.5, Anthropic’s Opus 4.7, Meta’s Muse Spark 1.1, still perform very strongly at many hacking and exploitation tasks that worry policymakers.
      • “It’s not even that the open-source variants or…not quite frontline competitors are catching up [to frontier models] as such,” said Albert Ziegler, head of AI at XBOW. It’s that they are crossing a certain threshold, which means that suddenly they are providing net value at a cheaper price.
      • “That wasn’t necessarily the case as recently as six months ago, when testing on mid-tier class models showed they struggled to complete “moderately complex” agentic tasks. Today’s middle class largely can. Their relative cheapness means users can spend many times more resources—running them repeatedly—to solve the same challenges.”
    • Cybersecurity Dive adds,
      • “Criminal and state-aligned threat groups are testing frontier and open-weight AI models to develop new methods of attacking corporate IT networks. 
      • “Attackers are using AI for a range of activities, enabling them to develop new exploits, accelerate attack speeds and maintain persistence through the abuse of legitimate tools, researchers from Accenture and Google Cloud said during a media presentation at the Black Hat USA conference in Las Vegas.
    • and
      • “Criminal actors are offering a range of AI-powered hacking tools and related services for sale on underground forums on the dark web, according to a report released Wednesday by cybersecurity firm Trellix. 
      • “Researchers found a wide range of AI-based tools being sold through these markets, ranging from reconnaissance tools to credential markets, as well as AI-as-a-service platforms. 
      • “The report shows how AI is being monetized to lower the barriers of entry into sophisticated threat activity. “
    • and
      • “Security researchers are backing claims by a newly emergent data-extortion group that it has exfiltrated sensitive data from about 15 companies, governments and other organizations. 
      • “A threat group called ExfilSquad claimed on July 26 to have exfiltrated customer records and other information from a number of city governments and universities, a major public school system and private companies. After being met with skepticism, the threat actor later released samples of the allegedly stolen information. 
      • “Researchers at Fortra released a report Thursday that corroborates ExfilSquad’s breach claims. The leaked data appears to be related to misconfigured Microsoft Power Page portals, a software-as-a-service platform that is used to create public-facing business websites. The misconfiguration enabled unauthorized access to Microsoft D365, according to researchers, which led to public read access.” 
    • Per Cyberscoop,
      • “Suspected Chinese hackers used open-source artificial intelligence models to run a cyberattack against the Taiwanese government in the first publicly known case of an autonomous AI hack hitting a government target, according to research published Wednesday.
      • “The hackers extracted more than 2,500 personnel records, among other data, in the “near-autonomous attack,” researchers at Israeli cyber firm Dream wrote in a blog post. The attackers set up the framework so that it could “adapt mid-operation without human intervention.”
      • “The framework “implements dedicated research phases it calls ‘Learning Cycles’ — autonomous sessions where the AI system searches vulnerability databases, GitHub repositories, and security research publications for techniques specifically applicable to its target government’s infrastructure,” the post reads.
      • “And then it kept going.”
    • The Cybersecurity and Infrastructure Security Agency (CISA) added three known exploited vulnerabilities to its catalog this week.
      • August 11, 2026
        • CVE-2026-20349 Cisco Secure Firewall Adaptive Security Appliance (ASA) and Firewall Threat Defense (FTD) Heap Inspection Vulnerability
        • CVE-2026-68820 Microsoft Windows Ancillary Function Driver for WinSock Use-After-Free Vulnerability
        • CVE-2026-72898 Metabase SQL Injection Vulnerability
          • Cybersecurity Dive discusses the Cisco KVE here.
          • The Hacker News discusses the Microsoft KVE here.
          • Dark Reading discusses the Metabase KVE here.
    • Cybersecurity Dive notes,
      • “The global system that catalogs technology vulnerabilities is resilient enough to survive the current onslaught of AI-generated bug reports that has alarmed cybersecurity experts, key leaders of that system said last week during panels at two security conferences here.
      • “The Common Vulnerabilities and Exposures (CVE) Program — whose unique vulnerability identifiers are the bedrock of the entire cybersecurity industry — “will find a way to scale,” Lindsey Cerkovnik, branch chief for vulnerability response and coordination at the Cybersecurity and Infrastructure Security Agency (CISA), said at the Black Hat USA conference on Thursday [August 6, 2026]. “CVE is going to continue to flourish and improve, and I feel very positively about it.”
    • Infosecurity Magazine points out,
      • “A critical-severity VMware vCenter vulnerability has been exploited within five days of disclosure by Broadcom, with attackers deploying an open-source reverse shell to hold access to compromised systems.
      • “The treat research team at German firm Quirso discovered the campaign during an incident response engagement and published its findings on August 10.
      • “The digital forensics company assessed a suspected advanced persistent threat (APT) actor was responsible, counting 361 victim IP addresses across 47 countries while cautioning that an IP address does not necessarily correspond to a single organization.
      • “The vulnerability, CVE-2026-59310, is acritical directory traversal flaw in the vCenter Syslog server rated CVSS 9.8. Broadcom said an unauthenticated attacker with network access to vCenter can exploit it to execute arbitrary code, turning a service built to collect logs into a route into the operating system.”
    • Per Cyberscoop,
      • “Delta Airlines said Tuesday [August 11] it’s investigating an incident on a Monday flight where a passenger reportedly used an unidentified device to spoof the airline’s in-flight Wi-Fi network, leading to severe delays and authorities to board the plane once it arrived at its destination.
      • “Various posts on several social media networks went viral early Tuesday detailing the incident, claiming that passengers on Delta flight 591 from Las Vegas to Atlanta used an unidentified device to create a rogue Wi-Fi network that could be used to steal people’s sensitive data or personal information.
      • “Messages from the plane’s Aircraft Communications Addressing and Reporting System (ACARS) show that the crew informed personnel on the ground that a passenger set up a network called “Delta WiFi Fast” and was “trying to scam the other passengers.”
      • “Morgan Durrant, a Delta spokesperson, told CyberScoop that the cabin crew deactivated the aircraft’s WiFi functionality for approximately 30 minutes, the flight’s safety was never in question and no aircraft operating systems were affected.” * * *
      • “The incident bears the hallmarks of an “evil twin attack,” where an attacker deploys a rogue Wi-Fi access point that masquerades as a legitimate, trusted network by cloning its name and network settings. Often paired with deauthentication attacks that forcefully disconnect devices from the real network, the fraudulent hotspot tricks nearby laptops and smartphones into automatically connecting to it instead. Once a device connects to the rogue point, an attacker can monitor unencrypted internet traffic, execute man-in-the-middle attacks, or display spoofed login portals designed to harvest sensitive user credentials and personal data.”  
    • The Wall Street Journal points out,
      • “Thousands of North Korean operatives are using fake and stolen identities to land remote jobs at U.S. companies—funneling hundreds of millions of dollars back to the regime.
      • “Leaked data, interviews and never-before-seen videos obtained by The Wall Street Journal reveal how a single team of these workers infiltrated at least eight companies in just a few months. Watch the documentary and read the practical takeaways.”

    From the ransomware front,

    • Checkpoint issued its report on the State of Ransomware Q2.
    • The American Hospital Association News reports,
      • “U.S. and international agencies released a joint cybersecurity advisory Aug. 10 warning of actions by Gunra ransomware. Gunra is a ransomware-as-a-service program that has been used to target government, critical infrastructure — including healthcare — and other organizations in the U.S. and abroad.
      • Gunra actors leverage a double-extortion model, both encrypting data and threatening to publish stolen data to a dedicated leak site if a ransom is not paid. The ransomware variant initially appeared in 2025. The advisory provides details on Gunra activity and includes detection and mitigation guidance to protect organizations.”
    • Dark Reading adds,
      • “The joint advisory urged organizations to prioritize patching known exploited vulnerabilities in Internet-facing appliances such as VPNs, implement and test offline immutable backups, and implement network segmentation to limit threat actors’ ability to move laterally.”
    • The HIPAA Journal relates,
      • “AnMed has not disclosed the name of the group behind the attack, but a threat group called The Gentlemen claimed responsibility. The Gentlemen is a ransomware-as-a-service group that is thought to include affiliates and operators from other prominent ransomware groups. The group has claimed several healthcare victims in recent months, and the pace of the attacks is accelerating.
      • “According to the Industrial Ransomware Analysis from the operational technology cybersecurity company Dragos, The Gentlemen was the third most active ransomware group in Q2 2026, claiming 125 attacks in the quarter alone, up from 83 attacks in Q1 – the largest gain out of all established ransomware groups. While the group ranked third, there were only 15 attacks separating the top three ransomware groups, with no single ransomware group dominating.”
    • Bleeping Computer tells us,
      • “Oil giant Shell has confirmed it is investigating a potential security incident after the Clop ransomware gang claimed it stole 89GB of data.
      • “Shell is a British multinational energy conglomerate and one of the world’s top three oil and gas companies, after Chevron and ExxonMobil. It has 85,000 employees in more than 70 countries and operates a massive network of tens of thousands of service and recharge stations that serve over 20 million customers daily.
      • “According to a recent post on Clop’s dark web data leak site, the allegedly stolen files include engineering drawings, scans of facility testing reports, photos of the facilities, and project plans.”
    • and
      • “An Akira ransomware affiliate disabled the endpoint detection and response (EDR) solution on a compromised system by restarting the machine into Safe Mode with Networking.
      • “The attack occurred on August 4 after the hacker obtained initial access through an exposed SonicWall VPN device without multi-factor authentication (MFA).
      • “Managed detection and response (MDR) services company Huntress says that roughly two hours after a successful VPN login, the attacker connected to the domain controller via RDP, enumerated Active Directory users and computers, and then moved to an application server.”
    • and
      • “CISA confirmed today that ransomware gangs have begun abusing a high-severity Microsoft SharePoint remote code execution vulnerability, which has been flagged as actively exploited since early July.
      • “Tracked as CVE-2026-45659, this security flaw stems from a deserialization of untrusted data weakness and allows attackers with low privileges to execute arbitrary code on unpatched SharePoint servers.
      • “It can also be exploited in low-complexity attacks because (as Microsoft explained in May when it released security updates for SharePoint Enterprise Server 2016, SharePoint Server 2019, and SharePoint Server Subscription Edition) “an attacker does not require significant prior knowledge of the system and can achieve repeatable success with the payload against the vulnerable component.”
    • The Record informs us,
      • “A financially motivated threat actor linked to China is believed to be exploiting a critical vulnerability affecting widely used cybersecurity software in a supply-chain attack that could see the hackers deploy custom ransomware across a cascading list of victims’ networks. 
      • “Microsoft Threat Intelligence warned this weekend that the Storm-1175 group began deploying a new ransomware strain on August 2 called StormEncryptor. The hackers previously used the Medusa ransomware to extort healthcare, professional services and finance organizations in Australia, Britain and the United States. 
      • “Back in April, the hackers were described as operating “high-velocity ransomware campaigns” exploiting both recently disclosed vulnerabilities and zero-day exploits, “in some cases a full week before public vulnerability disclosure.” Microsoft said it had seen the group move from initial access to full encryption in under 24 hours. 
      • “In this latest campaign, Microsoft said the group is likely exploiting CVE-2026-18577 — a vulnerability in N-central, a remote monitoring and management (RMM) console used by thousands of managed service providers to administer client endpoints.”
    • The Hacker News adds,
      • “The ransomware group known as DeadLock has been observed using decentralized infrastructure to facilitate victim communications and data leak operations in a bid to improve operational resilience.
      • “Its recovery ecosystem combines the Session messaging network with blockchain-backed services that store and deliver resources used throughout the extortion process,” the Microsoft Threat Intelligence team said.
      • “The tech giant said it observed the ransomware being deployed by multiple threat actors, including an affiliate for Lynx and INC ransomware.”

    From the cybersecurity business and defenses front,

    • Bloomberg reports,
      • “Anthropic PBC is telling prospective investors its second-quarter revenue jumped at least 14-fold versus the same period a year ago, according to documents seen by Bloomberg News.
      • “The Claude chatbot maker reported a preliminary revenue figure of more than $11.5 billion in its latest completed quarter, compared to $787 million in the corresponding period in 2025, and $4.73 billion in the first quarter of this year, the documents show. The second quarter of 2026 saw Anthropic report positive adjusted operating income, according to the documents.”
    • Reuters relates,
      • “Anthropic is in talks to buy Nvidia-backed startup Decart AI, according to a source familiar with ​the matter, as the Claude maker explores acquisitions that ‌could help it handle growing demand ahead of its public listing.
      • “Bloomberg News, which first reported the news on Wednesday, said a deal ​could be worth about $6 billion, citing sources.”
    • Tech Crunch adds,
      • “Anthropic will watermark text generated by its models, including Claude, to comply with European regulations, the company now says. The AI model maker confirmed the watermarking in an updated support page.” * * *
      • “It’s not clear how much editing users need to do to remove the watermark. We have asked Anthropic to clarify and will update the story if we hear back.
      • “The company noted that watermarking will apply to different products like Claude platform API, Claude, Claude Code, Claude Cowork, and Claude Tag.
      • “Platforms are now rushing to watermark AI-generated content after backlash from users and to avoid regulatory scrutiny. Last week, AI music platform Suno said it will mark tracks created on its platform after a spate of legal challenges. Last month, newsletter service Substack teamed up with Pangram to flag AI-generated content. The company’s CEO, Chris Best, called out Claudefishing, a term used for people using AI to generate content.
      • “Apart from Anthropic, other companies like Black Forest Labs, Google, Meta, Microsoft, OpenAI, and Synthesia have committed to adhering to the EU’s code.“
    • Cybersecurity Dive informs us,
      • “Cisco’s security revenue surged last quarter as the technology giant saw growing demand for products designed to protect businesses against emerging cybersecurity threats, including those enabled by artificial intelligence agents, the company reported Wednesday.
      • “The company posted $17.3 billion in total revenue for its fiscal 2026 fourth quarter ended July 25, a year-over-year increase of 18%. Security revenue rose 14% in the quarter to $2.2 billion from a year earlier.
      • “The rise of agentic AI is expanding the threat landscape, driving demand for our security and observability solutions to help monitor agent behavior and mitigate evolving threats,” CEO Chuck Robbins said during a Wednesday earnings call.”
    • The Wall Street Journal notes,
      • “Enterprise users spent $300 million on quantum computing in 2025, outranking research labs and governments as the primary spenders for the first time.
      • “A Boston Consulting Group survey found that 62% of the top 25 global companies across 11 major industries spend at least $1 million annually on quantum.
      • “Companies like HSBC, Allstate and EY are investing to prepare for future commercialization and to secure systems against quantum encryption threats.”
    • Per Dark Reading,
      • “Walmart, the world’s largest retailer, faces a complex cyber threat landscape, documenting 806 reported retail breaches in Verizon’s 2026 Data Breach Investigations Report.
      • “Security leadership stresses balancing strong cybersecurity controls with business innovation and speed, avoiding operational drag that could lead staff to bypass safeguards.
      • “Walmart’s security approach involves proactive transparency and trust-building with leadership, using color-coded executive summaries and open discussions on risks and mitigation progress.
      • “Industry experts emphasize the evolving role of security operations as essential business partners, noting there is no one-size-fits-all model but a universal need for pragmatic resilience and honest communication.”
    • and
      • “The Patch Gap: Why Defenders Need to Think in Chains, Not Checklists
      • “It’s time to turn from CVSS-backed patching to choke-point patching focused on breaking chains to critical assets.”
      • “If the volume problem and prioritization problem can’t be solved by patchingfaster and scoring harder, then the framing itself needs to change. The question that the security team should ask is not “which vulnerabilities are most severe in isolation?” but rather “which vulnerabilities, if left unpatched, create a connected path from an attacker’s foothold to our most critical assets?”
    • Per a CISA announcement,
      • “This year marks the 20th year of Cyber Storm, a full-scale national cybersecurity exercise that for two decades has brought together the people who defend the systems Americans rely on. Held every two years, Cyber Storm X arrives as threats from geo-political activity, compromised edge devices, AI risks, and more present new challenges to our nation’s critical infrastructure.
      • “As the nation’s largest cybersecurity exercise, Cyber Storm plays a vital role in preparing for potential cybersecurity incidents by testing and strengthening the nation’s ability to coordinate a unified cyber response. Participants from private and public organizations work together through a simulated crisis. Together, they learn as a team and build stronger relationships that will speed response during an actual event. Importantly, organizations can also update their response plans based on lessons learned during the exercise.” * * *
      • “Learn more about Cyber Storm and past events at cisa.gov/cyber-storm. For more information about CISA’s exercise resources, visit CISA Exercises.”
         
    • Security Boulevard adds,
      • “CrowdStrike has announced a $100,000 international competition that challenges participants to manipulate live AI agents using prompt injection and other red-teaming techniques.
      • “The competition takes the form of a virtual game called AI Unlocked: Agents of Chaos, created in collaboration with Amazon Web Services. Players take on a fictional mission to stop a shadow group from deploying malicious AI. To do that, they must manipulate the group’s own agents into revealing information and taking actions they were not authorized to perform. Their scores also depend on efficiency, with points deducted for every token used in their prompts.
      • “The contest opens Aug. 31 and is divided into three acts. The first runs through Sept. 7 with a $10,000 prize, the second ends Sept. 14 and awards $20,000, and the final act runs from Sept. 15 through Sept. 29 with a $70,000 prize. The game is available online internationally, with an in-person option to play at CrowdStrike’s Fal.Con conference. Pre-registration is open, and contestants can replay completed puzzles to refine their prompts. CrowdStrike said the highest score recorded when each act closes will receive that act’s prize.”
    • Here is a link to Dark Reading’s CISO Corner.

    Cybersecurity Saturday

    “We are in the Singularity.” Elon Musk

    From the Project Glasswing front,

    • The Wall Street Journal reports,
      • OpenAI is pausing some activities involving an upcoming artificial-intelligence model, Astra, after internal evaluations led the company to conclude it “cannot rule out critical cyber capabilities,” the company said in a blog post on Friday [August 7, 2026]. 
      • The announcement of the slowdown, which represents one of the first times an AI developer has publicly held back model development due to security concerns, follows a series of loss-of-control incidents that have raised alarm among cyber defense professionals and AI-safety researchers. 
    • and
      • “Meta Platforms META  said that one of its artificial-intelligence models went rogue during cybersecurity testing, slipped onto the internet and hacked a third-party service, the latest in a drumbeat of disclosures that suggest such incidents are becoming widespread.
      • “The Instagram and Facebook owner said that one of its AI models was able to access the internet because of a “misconfiguration” in a hacking test conducted by a third-party AI testing company. 
      • “The same benchmark test, which aims to explore a model’s hacking capabilities, was behind some of several earlier autonomous AI hacking incidents involving Anthropic and OpenAI, according to a person familiar with the matter. * * *
      • “Irregular, the company that conducted tests for the three companies, said the incidents didn’t involve a sophisticated cyber action and said it had “no current open issues” related to its test environment. The San Francisco-based company said it is working on a white paper on best practices for containing AI models when running tests—dubbed evals—of their cybersecurity capabilities.
      • “The new case [reported August 6, 2026] is the latest proof that AI loss-of-control scenarios, once confined to science fiction and AI-safety experiments, are now a real-world issue.”
    • Cybersecurity Dive relates,
      • “An alliance of more than 100 tech companies and other organizations is proposing a safety reporting system for AI agents that the group says will help prevent rogue models from wreaking havoc on society.
      • “The Shared AI Findings Exchange (SAFE), crafted by a working group of the Open Secure AI Alliance, would establish mechanisms for collecting information about AI-related security incidents, sharing that information with affected organizations, identifying commonalities across incidents and publishing recommendations based on those lessons.”
    • Tech Times adds,
      • “ByteDance is pre-training an artificial intelligence model with up to 10 trillion total parameters — a scale that would make it the largest AI model ever built by a Chinese company and place it within striking distance of Anthropic’s Mythos system, the Financial Times reported Friday, citing people familiar with the matter. The headline figure is real and remarkable. What it does not tell you — what ByteDance has not disclosed and no outlet has yet asked — is how many of those parameters actually activate during any given query. At a scale like this, that distinction changes everything.”
    • FEHBlog observation; Ruh-roh.
    • Cyberscoop notes,
      • “As AI-generated code continues to be injected into all corners of the internet, concerns have risen about an expanding attack surface for malicious hackers to exploit.
      • “Some have argued that the enhanced cybersecurity capabilities of large language models could serve as a check, finding and fixing vulnerabilities nearly as fast as they’re created.
      • “But new research that tested the patching capabilities of two popular commercial models, OpenAI’s ChatGPT 5.5 and Anthropic’s Claude Opus 4.8, found that generative AI is more likely to create an exploitable patch or introduce entirely new bugs than close off a vulnerability.
      • “Researchers at 1Password tested the models ability to patch six “high-impact, high-complexity” CVEs, including the “Copy Fail” vulnerability, a kernel flaw that can give an attacker root access to Linux cloud environments. The overall success rate (or fully patching the vulnerability without introducing new problems), was less than a coin flip at 47%.
      • “Our research findings show that, in aggregate across a variety of scenarios, both Claude and ChatGPT had a low rate of successful patch generation, which we define as full remediation of all known exploit paths with no erroneous changes to application behavior,” wrote John Hoodlet, Axel Mierczuk and Spencer Michaels.

    From the cybersecurity policy and law enforcement front,

    • Roll Call reports,
      • “The Senate easily passed a bipartisan continuing resolution early Saturday morning [August 8, 2026] likely easing the traditional September rush to head off a partial government shutdown in October.
      • “On a lopsided vote of 90-6, the Senate passed a measure that would extend current funding through Dec. 11, giving lawmakers about 10 extra weeks to complete full-year appropriations bills for fiscal 2027.
      • “But the bill still requires a vote in the House, which won’t be back in session until the first week of September. The House had passed a more bare-bones funding extension last month without many of the “anomalies,” or deviations in current spending, requested by the Trump administration.”
    • Federal News Network adds,
      • “The Senate’s bill to keep the government funded past the midterm elections would extend critical cybersecurity authorities and allow the Technology Modernization Fund to continue investing in agency tech projects. * * *
      • The Senate CR, unlike the House bill, would extend two cybersecurity authorities for the duration of the stopgap: the Cybersecurity Information Sharing Act of 2015 and the Federal Cybersecurity Enhancement Act of 2015. Both laws are set to expire after Sept. 30.
      • CISA 2015 provides privacy and liability protections to encourage companies to share data about cyber vulnerabilities and threats with government and each other. Cybersecurity leaders say those protections provide a critical underpinning to facilitate collaboration across government and industry. * * *
      • “Meanwhile, the Federal Cybersecurity Enhancement Act authorizes the Department of Homeland Security to deploy intrusion detection tools, like the long-running “EINSTEIN” service, across federal agencies.”
    • Cybersecurity Dive relates,
      • “National Cyber Director Sean Cairncross on Tuesday [August 4, 2026] said the Trump administration is working to strike a balance between responsible, secure development practices, while promoting growth and allowing the private sector to innovate. 
      • Cairncross, the opening keynote at the Black Hat USA 2026 cybersecurity conference, said the White House understands the growing safety concerns about AI, but recognizes the need to work collaboratively with the private sector. 
      • He warned that due to the current pace of innovation, an overly prescriptive regulatory regime could be obsolete within 48 hours of being implemented.  
      • “So what needs to be built is a flexible, adaptable structure that enables information sharing between industry and government,” Cairncross said. “So we can guarantee that this technology benefits everyone that it’s going to benefit but is used responsibly and securely.”
    • and
      • “Policymakers and business executives need to focus on basic cybersecurity resilience instead of getting distracted by flashy claims about AI-fueled hacking nightmares, a group of senior U.S. and allied government officials said on Wednesday.
      • “The immediate challenge is not runaway AI,” Jonathon Ellison, director for national resilience at the UK’s National Cyber Security Centre, said during a panel at the Black Hat 2026 cybersecurity conference here. “The immediate challenge is being resilient enough for the faster-paced environment that we are entering into, given the legacy issues that we are carrying.”
      • “Michael Duffy, the acting U.S. federal chief information security officer, said organizations needed to shift from a prevention-focused mindset to one that prioritizes continuity of services.
      • “Things will go down,” he said, and organizations need to prioritize their most important systems so they can continue delivering on their mission.
      • “The cybersecurity community, he added, needs “a new risk calculus for what it means to operate in a contested environment.”
    • The Wall Street Journal tells us,
      • “An outbreak of digital attacks on U.S. water plants is stoking fears across party lines that budget cuts at the federal government’s primary cybersecurity agency could leave the nation ill-equipped to thwart global hackers.
      • “We need a skilled cyber workforce at CISA,” Rep. Andrew Garbarino, a New York Republican, said about the Cybersecurity and Infrastructure Security Agency. Garbarino, who chairs the House homeland security committee, said Congress and the White House need to work together to ensure the agency has the staff and resources to protect critical infrastructure.” * * *
      • “In April, CISA’s annual budget was cut by $300 million, to $2.6 billion from $2.9 billion, reversing an annual growth rate of roughly 9% since the agency was launched in 2018. The shortfall has both Republican and Democratic lawmakers seeking ways to recharge the agency—for a start, by confirming a permanent director, a role vacant since January 2025. 
      • “Rep. Bennie Thompson (D., Miss.), ranking member on the Homeland Security committee, said he plans to propose legislation aimed at guiding the process of restaffing CISA. Thompson didn’t provide a timeline, saying he will also work with appropriations to restore the agency’s funding. Staff and budget cuts, he said, have “damaged our national security and set critical capabilities back years as the security environment is shifting under our feet.”
      • “An agency spokesperson said CISA is “constantly assessing our operational needs as the threat landscape evolves” and that Homeland Security recently approved new hiring in several mission critical positions.”
    • Cyberscoop informs us,
      • “A Canadian man pleaded guilty to playing a central role in one of the most far-reaching cyberattacks of 2024 — the widespread compromise of more than 165 Snowflake customer environments, resulting in massive data theft for extortion, the Justice Department said Wednesday [August 5, 2026]. 
      • Connor Moucka earned $495,000 by extorting his victims, offering stolen data for sale online, and in one case re-extorted a victim with stolen data of a government official and members of a then-former government official’s immediate family, authorities said.
      • Moucka and his alleged co-conspirators John Binns and Cameron Wagenius stole billions of sensitive records and received more than $2.5 million in extortion payments combined, according to prosecutors. Victims of the attack spree included AT&T, Ticketmaster, Advance Auto Parts and Santander.
    • and
      • “A longtime cybercriminal was sentenced to 16 years in prison for creating and running Ransom Cartel, a ransomware strain linked to attacks on at least 18 companies between 2021 and 2023, the Justice Department said Wednesday [August 5, 2026]. 
      • “Maksim Silnikau, a Belarusian national, actively participated in Russian-speaking cybercrime forums since at least 2005, and was a member of the cybercrime site Direct Connection from 2011 to 2016, officials said. The 40-year-old created Ransom Cartel and began recruiting participants from cybercrime forums in 2021. 
      • “Silnikau and his co-conspirators attempted to extort at least $5.2 million from victims during the multi-year scheme. 
      • “Victims included a group of law firms, medium-sized businesses, a small medical technology startup, educational institutions and large multinational corporations based in California, New York, Nebraska and elsewhere. Some of the victims’ operations were disrupted for several months, officials said.
    • HIPAA Journal points out,
      • “Over the past 18 months, many healthcare providers have settled class action lawsuits over their use of website tracking and analytics tools. The list continues to grow with a further five settlements recently announced [and discussed in the article]; however, class action lawsuits stemming from the use of tracking and analytics tools do not always result in settlements.
      • “A proposed class action lawsuit against CRH Healthcare, doing business as Peachtree Immediate Care in Georgia, that alleged violations of the federal Electronic Communications Privacy Act and asserted claims for negligence/negligence per se, breach of implied contract, breach of express contract, breach of fiduciary duty, and unjust enrichment, has been dismissed with prejudice.
      • “The judge ruled that the complaint was speculative, as the plaintiff failed to explain what damages had been suffered as a result of the defendant’s actions. The plaintiff has been given 14 days to file an amended complaint, or the lawsuit will be permanently dismissed. The decision shows that while tracking and analytics tools may result in disclosures of sensitive data to third parties, the plaintiff(s) must demonstrate that the disclosures resulted in a compensable injury.”

    From the cybersecurity breaches and vulnerabilities front,

    • Healthcare Dive continues to track healthcare data breaches here.
    • For example, Bleeping Computer notes,
      • “Healthcare software company Unlimited Technology Systems reported that more than 3.8 million people were impacted by a data breach incident that occurred in October 2025.
      • ‘The organization submitted data breach notification samples to the authorities this year on July 1st without revealing the exact number of impacted individuals.
      • “An entry on the breach notification portal of the U.S. Dept. of Health and Human Services now shows that a company server was breached and data of 3,803,750 people was exposed to an unauthorized party.
      • “Unlimited Technology Systems is a software company specializing in providing financial and revenue cycle technology for specialty healthcare providers. According to its website, the firm serves 4,500 clinics and 6,500 specialty healthcare providers across the United States, and processes more than $70 billion in net healthcare charges annually.”
    • The Wall Street Journal reports,
      • “Federal agencies are investigating cyberattacks that targeted more than 30 water systems in Minnesota and utilities in several other states.
      • “Former national security officials say the attacks are consistent with Iran-linked activity, but President Trump rejected that idea.
      • “Small water utilities are vulnerable to hackers because they rely on internet-connected automation but often lack the funding to secure it.”
    • Cyberscoop adds,
      • “The U.S. Coast Guard said it is monitoring the aftermath of a cyberattack that disrupted gate operations at all three of North Carolina’s port facilities this week, though it offered few details as the investigation into the breach continues.
      • “A Coast Guard spokesperson told CyberScoop that the branch’s IT unit was coordinating with partner agencies while conducting the investigation. A spokesperson for CISA did not respond to CyberScoop’s inquiry by press time [on August 7, 2026]. 
    • Security Week points out,
      • “Thousands of data centers are at risk of compromise due to a 22-year-old vulnerability in Baseboard Management Controller (BMC) management processors, data center security firm Lava reports.
      • “Found in most server platforms, BMCs enable server management operations even without a working operating system and typically represent some of the most privileged control points in a data center.
      • “Through a BMC, administrators can power-cycle the host, perform firmware updates, make low-level platform configuration changes, read hardware sensors, and more, using several management surfaces, including the IPMI out-of-band protocol, the Redfish HTTPS-based management API, and a web-based administrative interface.
      • “In many implementations, these interfaces share the same user database. A credential that works for IPMI may also work for the web interface or Redfish API. This matters because the IPMI authentication process can expose information that enables offline password recovery,” Lava notes.”
    • To sum up, Cybersecurity Dive lets us know,
      • “Cyberattacks on operational technology have shifted in recent years from extortion and espionage to destruction, a trend that should alarm those tasked with defending outdated industrial equipment, experts said on Thursday.
      • “The panel discussion at the Black Hat USA cybersecurity conference here highlighted the plethora of risks facing U.S. critical infrastructure operators — many of them poorly staffed and funded — at a time of heightened geopolitical conflict.
      • “OT attacks are increasingly moving from targeting not just data but physical operations,” said Cheri Benedict, a cybersecurity and supply chain adviser at the White House’s Office of the Federal Chief Information Officer.
      • “There is a real desire and willingness to cause this impact at scale,” said Matthew Rogers, the operational technology cybersecurity lead at the Cybersecurity and Infrastructure Security Agency (CISA).”
    • and
      • “Cyberattacks on the healthcare industry have brought hospitals, clinics and other providers to a breaking point, researchers said on Friday.
      • “These are patient safety issues, and yet these types of attacks continue to increase,” Christian Dameff, the co-director of the University of California San Diego’s Center for Healthcare Cybersecurity, said during a presentation at the DEF CON conference here.
      • “The healthcare sector consistently ranks as one of hackers’ top targetsbecause of the sector’s financial constraints, supply-chain opacity and low tolerance for downtime. Cybercriminals have repeatedly broken into hospital chains and healthcare vendors, sometimes causing widespread disruptions and even jeopardizing patient safety.”
    • Cyberscoop adds,
      • “In less than four hours early Tuesday [August 4, 2026], an attacker compromised a GitHub maintainer account and unleashed a self-replicating piece of malware which injected malicious code into more than 440 distinct npm packages, according to multiple security firms. 
      • “The worm, built on the open-source Mini Shai-Hulud repository that TeamPCPpublished in May, was initially let loose in keyv, a data management interface software package with more than 600 million monthly downloads. The attacker spent the next 30 minutes compromising additional packages controlled by the same maintainer, including cacheable, flat-cache, file-entry-cache.
      • “The attack spread to other maintainers, eventually compromising more than 860 packages with a “combined total of over 2 billion monthly installs,” Ilyas Makari, malware researcher at Aikido Security, wrote in a blog post. 
      • “Wiz researchers told CyberScoop it hasn’t observed any new malicious packages since the initial wave moved through a massive footpoint of cloud and code environments in those first four hours.” 
    • Cybersecurity Dive tells us,
      • “Researchers have found fifteen previously unknown vulnerabilities that affect zero-touch provisioning in TP-Link Omada, which is widely used to provision network devices from a central location, according to a report by Forescout Research – Vedere Labs. 
      • “Small to medium-sized companies use the technology to rapidly set up routers and firewalls, which in some cases involves thousands of devices. The technology helps companies save considerable costs when deploying network devices, but it also offers attackers wide access to a lot of systems. 
      • “The research, presented Wednesday [August 5, 2026,] at the Black Hat USA conference in Las Vegas, shows that attackers can chain together vulnerabilities with previously disclosed flaws and infiltrate networks.”
    • and
      • “The malicious use of AI has rapidly accelerated to the point where some threat groups have embedded the technology across their cyber operations, according to a report released Monday [August 3, 2026,]by CrowdStrike. 
      • “China-nexus actors Vault Panda and Genesis Panda have used AI to exploit critical vulnerabilities within 24 hours after a proof-of-concept was disclosed. 
      • “Meanwhile a North Korea-nexus group tracked as Stardust Chollima was able to inject a malicious npm package into 131 trusted Mastra AI frameworks in a supply-chain attack, according to CrowdStrike researchers.” 
    • Per Bleeping Computer,
      • “The Greatness phishing-as-a-service (PhaaS) platform has expanded from credential phishing to adversary-in-the-middle attacks and device-code phishing targeting Microsoft 365 accounts.
      • “The platform has been active since at least mid-2022, targeting Microsoft 365 users in the United States, Canada, the UK, Australia, and South Africa.
      • “It evolved over the years and now targets multiple platforms, including Microsoft 365, iCloud, Yahoo, and Google Workspace.
      • “Currently, it is sold for $289 per month to cybercriminals over a Telegram channel with thousands of subscribers.”

    From the ransomware front,

    • Cybersecurity Dive reports,
      • “Ransomware extortion caused roughly three-quarters of business losses in the first half of 2026, the cyber insurance firm Resilience said in a recent report.
      • “At the same time, ransomware accounted for less than 6% of the incidents for which Resilience customers submitted claims, which the company said highlighted how “disproportionately costly” they are.
      • “Other data in the report highlight the importance of proper employee training and vigilant adherence to protocols such as regular backups.”
    • The Register adds,
      • “Ransomware attacks jumped nearly 20 percent in July, with UK firm Comparitech counting 799 incidents, up from 668 in June.
      • “Of those, 51 had been confirmed by victims. The tally makes July the second-busiest month of the year for ransomware, behind March, albeit just barely, when the firm recorded 805 attacks.
      • “The most interesting data after this surging month of attacks is the targets: While news of widespread cyberattacks targeting water infrastructure in the United States may be dominating security headlines lately, those attacks aren’t ransomware, and ransomware attacks on utility companies were actually down 44 percent last month.
      • “In addition to a decline in attacks on utilities, legal firms and government agencies also became less attractive targets, with attacks on those sectors down 31 percent and 11 percent, respectively, Comparitech said.
      • “On the other hand, ransomware attacks increased most heavily in July against finance companies, tech firms, pharmaceutical companies and medical billers, and the education sector, with rates up 71 percent, 62 percent, 46 percent and 44 percent, respectively. 
      • “Those numbers should come as no surprise given what pentesting firm DeepStrike reported about the most frequent payers of ransomware: Manufacturing, education, healthcare, and financial sector firms are the most likely to pay out a ransom, the firm says, with even the least likely (finance) still paying ransoms 51 percent of the time. Ripe targets, in other words.” 
    • Cyberscoop relates,
      • “Researchers said INC ransomware, one of the most active ransomware groups globally, has been the main attacker exploiting a pair of SonicWall zero-days soon after they were disclosed last month.
      • “The prolific ransomware-as-a-service operation wasn’t the first group to exploit the flaws, which were actively exploited for three weeks before the vendor disclosed and patched the defects July 14, but it has been the most assertive and concerning group to target and chain both vulnerabilities together for full access.
      • “Since public disclosure, INC ransomware has emerged as the most commonly named threat actor actively weaponizing this vulnerability chain,” Brett Deroche, director of incident response at Rapid7, told CyberScoop. “While Inc is the name driving the post-disclosure wave, we can’t attribute the full body of exploitation to INC specifically.” * * *
      • “The SonicWall vulnerabilities — CVE-2026-15409 and CVE-2026-15410 — are the latest in a series of security issues confronting the vendor’s customers, including actively exploited zero-days, previously disclosed defects, and an attack last year that allowed a state-sponsored threat group to steal the firewall configurations of every SonicWall customer.” 

    From the cybersecurity business and defenses front,

    • The Wall Street Journal reports,
      • “Hasbro CFO Gina Goetter was abroad when a cyberattack hit the company this spring. The day started as planned, but her schedule was wiped clean a few hours later.  
      • “The team “knew something was wrong in the morning,” said Goetter, who is also the company’s COO. “By afternoon, they were aware that it was a breach.” 
      • “The toy and game maker discovered the intrusion in late March. Executives quickly pulled its entire SAP system, which tracks everything from financial to human-resource matters, offline to assess the damage. For three or four days, employees relied on manual workarounds to keep operations moving, forcing Hasbro to delay its first-quarter earnings. 
      • “Company leadership, however, refused to derail certain business operations. * * *Systems were restored faster than anticipated following the cyberattack, keeping costs lower than expected. Hasbro lost roughly $25 million in revenue because of the breach in the three months ended June 28, below the projected $40 million to $60 million hit. The swift recovery allowed the company to quickly terminate third-party legal and accounting support, often a significant part of the costs, according to Goetter.  “We came up faster, which helped,” she said.”
    • SC Media adds,
      • “No, 60% of small businesses don’t fail within six months of suffering a data breach.
      • “That widely circulated figure has been bouncing around for 15 years, but it’s dead wrong, security researcher Adrian Sanabria said Tuesday (Aug. 4) at the BSides Las Vegas hacker conference.” * * *
      • “Sanabria didn’t have any suggestions for companies that are short of cash when an attack or breach happens, other than to have a line of credit at the ready. But he pointed out that transparency and honesty go a long way toward restoring trust after a breach.
      • “Especially in healthcare, he said, “the more transparent you are, the less you’ll get sued for.”
        An audience member cited CrowdStrike as handling its devastating July 2024 bad-update incident very well, with the company leader’s same-day online mea culpa and subsequent apology tour to visit affected clients.
      • “Unfortunately, Sanabria said, many companies of every size still think it’s wiser to not disclose data breaches. That’s mainly out of fear of legal exposure, even though it’s clear that timely and full disclosure is the better policy.
        “Most of the reasons we have for keeping breaches quiet are not good reasons,” Sanabria said. “The model is there, and we know how to do it, but the lawyers won’t let us.”
    • Here’s a link to Dark Reading’s CISO Corner.